Open Bottle - Security Industry Panel Discussion
Security experts discuss industry trends, vulnerabilities, and ethical hacking in an open panel. Topics include fuzzing, e-commerce security, IPv6 research, and experiences from diverse cybersecurity backgrounds.
Targeted Attacks in Asia
Evolution of politically motivated targeted malware attacks in Asia over five years. Analysis of attack campaigns against human rights groups, media, and political parties, revealing overlaps and shifts in tactics. Discussion on countermeasures and futur…
Implementing Your Own Generic Unpacker
Detailed guide on creating a stealthy, efficient generic unpacker for Windows, covering kernel mechanisms, memory management, and PE loading. Includes implementation details and results on real-world samples.
Adventures in Security Research
Explore defensive security, journalism protection, and diverse tech challenges with insights on gun hacking, malware analysis, and mission-driven work from a seasoned security expert.
One-Click to Completely Takeover a MacOS Device
Explore vulnerabilities in MacOS security features and learn how to bypass them for a one-click takeover of both Apple Silicon and Intel Mac devices. Includes live demo and expert insights.
Hack In The Studio - Fireside Chat
Fireside chat with cybersecurity experts Stefano Zanero and Marco Balduzzi, discussing their research, experiences, and insights in malware analysis, cyberphysical security, and emerging threats in the digital landscape.
Attacking Automated Manufacturing Systems
Explores attack surfaces and vulnerabilities in automated manufacturing systems, discussing potential impacts on product quality, plant safety, and industrial espionage in Industry 4.0 environments.
SHADOWPAD - Chinese Espionage Malware-as-a-Service
Comprehensive analysis of SHADOWPAD malware: its origin, usage patterns, and business model. Explores its impact on Chinese cyber espionage and the evolving threat landscape.
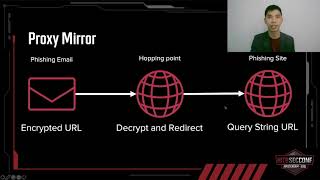
Dissecting Phishing Techniques of CloudDragon APT
Análisis detallado de las sofisticadas técnicas de phishing del grupo APT norcoreano CloudDragon, incluyendo casos reales, métodos para evadir la autenticación de dos factores y propagación a sistemas Android.
Network Based Detection of PE Structural Anomalies
Explore network-based detection techniques for identifying structural anomalies in Portable Executable (PE) files, enhancing cybersecurity defenses against malware threats.
O-Checker - Detection of Malicious Documents Through Deviation From File Format Specifications
Explores detection of malicious documents by identifying deviations from file format specifications, focusing on targeted email attacks in Japan and introducing the o-checker tool for high detection rates.
Industroyer - Crashoverride - Zero Things Cool About a Threat Group Targeting the Power Grid
Análisis detallado del malware Industroyer utilizado en el ciberataque a la red eléctrica de Ucrania en 2016, sus capacidades y el grupo de amenazas detrás del ataque.
Malware Buried Deep Down the SPI Flash - Sednit's First UEFI Rootkit Found in the Wild
Uncover Sednit's groundbreaking UEFI rootkit campaign, exploring its sophisticated techniques for deep system compromise and implications for cybersecurity in high-profile attacks.
Black Hat Fast Chat
Insights into Black Hat Briefings review process, Malware Track leadership, and community development initiatives from cybersecurity expert Matt Suiche, founder of Comae Technologies.
Detecting -Un-Intentionally Hidden Injected Code by Examining Page Table Entries
Explore techniques for detecting hidden injected code through page table entry analysis, covering both intentional malware concealment and unintentional OS paging mechanisms.
Demigod - The Art of Emulating Kernel Rootkits
Explore advanced techniques for emulating and analyzing kernel rootkits, enhancing cybersecurity defenses against high-privilege malware operating at the OS level.
FASTCash and INJX_Pure - How Threat Actors Use Public Standards for Financial Fraud
Explore how cybercriminals exploit public standards to conduct ATM fraud through INJX_Pure and Lazarus FASTCash malware, showcasing their programming skills and understanding of financial transactions.
Indicators of Compromise - From Malware Analysis to Eradication
Learn to identify, analyze, and eradicate unknown malware in corporate networks using freely available tools. Gain practical skills for effective threat detection and response.

Automated Extraction of Configuration and Payloads from Sophisticated Malware
Automated malware analysis system for extracting payloads, configurations, and indicators from sophisticated malware, reducing time and skill requirements for threat intelligence.
Malware Analysis as a Hobby
Learn to create an efficient, automated environment for analyzing suspected malicious sites and software, even with limited time and budget.
Reverse Engineering and Bug Hunting on KMDF Drivers
Explore reverse engineering and bug hunting techniques for KMDF drivers, focusing on entry points, IO queues, and implementation vulnerabilities. Gain practical skills for analyzing driver security.