Unveiling the Attack Chain of Russian-Speaking Cybercriminals
Unveiling the sophisticated attack chain of Russian-speaking cybercriminals, detailing their infrastructure, techniques, and resources accumulated since 2007, including billions of compromised emails and millions of infected servers.
Hacking FinSpy - A Case Study
Explore FinSpy hacking techniques, including version analysis, configuration decryption, and network communication interception, in this detailed cybersecurity case study.
Embracing the New Threat Towards Automatically Self-Diversifying Malware
Explore evolving malware threats, automatic diversity techniques, and compiler-based diversification strategies to enhance cybersecurity defenses against self-diversifying malware.
Chasing the White Whale of Malware
Exploring techniques to identify and analyze operational technology malware, focusing on unique challenges and methods for filtering OT binaries without advanced reverse engineering skills.
Does Your Threat Model Consider Country and Culture? A Case Study of Brazilian Internet Banking Security to Show That It Should
Explores unique cybersecurity challenges in Brazilian internet banking, highlighting how regional factors shape threats and the need for localized threat models in global security assessments.
Sleight of ARM- Demystifying Intel Houdini - Brian Hong - Ekoparty 2021- Hardware Hacking Space
Explore Intel's Houdini binary translator for running ARM on x86, its inner workings, security weaknesses, and potential exploits. Gain insights into cross-architecture execution and its implications for Android security.
Revisiting Ring3 API Hooks: Tricks to Defeat Analysis Tools - Rafael Salema Marquez - Ekoparty - 2021
Explore innovative ring3 API hook techniques for malware development, focusing on "Egg hook" and "Hollow hook" methods to evade detection by analysis and forensics tools.
Dissecting a Ransomware-Infected MBR - Raul Alvarez - Hack in Paris - 2017
Explore ransomware's impact on MBR, boot process manipulation, and malicious kernel code execution. Learn to debug MBR and understand native code execution without APIs in this technical deep dive.
Synthetically Breaking macOS - Patrick Wardle - Ekoparty Security Conference - 2019
Explore macOS security vulnerabilities and bypasses with Patrick Wardle, focusing on synthetic events and code-signing flaws. Learn about potential risks and defensive strategies for Mac users.

The Advanced Threats Evolution- REsearchers Arm Race - Alex Matrosov - Ekoparty Security Conference - 2019
Explore the evolution of advanced threats and defensive software, focusing on persistent methods at hardware and firmware levels. Gain insights into modern security gaps and potential solutions.
Demystifying a Malware Attack
Explore the anatomy of malware attacks, from deployment to key players involved. Gain insights into attack strategies, technologies used, and lessons for better cybersecurity preparedness.
The Good Hacker - Dismantling Web Malware
Explore web malware anatomy, impact, and detection techniques. Learn about browser vulnerabilities, drive-by downloads, and real-world case studies of exploit kits and botnets.
Hacking .NET Applications - The Black Arts
Explore techniques for hacking .NET applications, including malware analysis, code review, and penetration testing. Learn to build keygens, cracks, and overcome security measures in .NET environments.
Malware Automation
Explore automated malware production techniques, tools, and methodologies used by attackers to generate thousands of threats daily, including a live demonstration of the process.
Tired of Playing Exploit Kit Whack-A-Mole? Let's Automate
Explore automated detection of Exploit Kits using headless browsers, JavaScript, and DOM inspectors for efficient web crawling and analysis of malware delivery techniques.
Open Source Malware Lab
Explore open-source tools for malware analysis, including Cuckoo Sandbox, Thug, Bro Network Security Monitor, and Volatility Framework. Learn to build an automated lab for comprehensive threat assessment.
Bypassing Malware Analysis Sandboxes Is Easy - Let’s Discuss How They Are Doing It and Why It Works
Explore techniques used by malware to evade analysis sandboxes, comparing various sandbox solutions and their effectiveness in detecting and analyzing different types of malware.
Operation PZCHAO - Dissecting a Cyber-Attack
Explore a sophisticated cyber-attack targeting Asian institutions, dissecting its modules, capabilities, and impact on victims' data in this in-depth analysis of Operation PZCHAO.
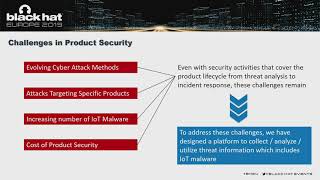
Understanding the IoT Threat Landscape
Explore IoT threat landscape, malware analysis, and Panasonic's approach to developing resilient products and an IoT SOC. Learn about security testing and the IoT Intelligence Platform.
BluePill - Neutralizing Anti-Analysis Behavior in Malware Dissection
Explore BluePill, a customizable tool for neutralizing anti-analysis techniques in malware. Learn how it defeats evasive samples and executable protectors, enhancing malware dissection capabilities.
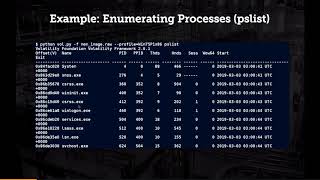
Investigating Malware Using Memory Forensics - A Practical Approach
Practical approach to memory forensics for malware detection and investigation, covering techniques, demonstrations, and analysis of various malware types and rootkits.