Breaking Firmware Trust From Pre-EFI - Exploiting Early Boot Phases
Exploración de vulnerabilidades en fases tempranas de arranque, evolución de mitigaciones de firmware y nuevos ataques en módulos de evaluación de plataformas Intel desde una perspectiva ofensiva.
Advanced Techniques for Real Time Detection of Polymorphic Malware
Explore advanced techniques for detecting polymorphic malware in real-time, including approximation matching algorithms and bloom filters. Compare efficiency and performance of various methods for fast identification and classification.
A New Secret Stash For Fileless Malware
Explores advanced fileless malware techniques using Windows event logs for code hiding and infection. Reveals new methods to conceal shellcode and manipulate logging functions.
Unraveling the Threat of Chrome Based Malware
Explore Chrome extension vulnerabilities, their potential for network compromise, and strategies for identifying and mitigating risks in enterprise environments.
Prospecting Ransomware Tech
Análisis detallado de las tecnologías y tendencias de ransomware en 2017, explorando mezclas de técnicas maliciosas, métodos de propagación y algoritmos de cifrado utilizados por diversas familias de malware.
Implementing a Kick-Butt Training Program - Blue Team Go
Discover a framework for building a robust cybersecurity training program that empowers analysts with hands-on skills in incident response, forensics, and threat hunting.
A Deep Dive into Go Malware - Using Metadata to Empower the Analyst
Explore Go malware's unique characteristics, metadata analysis techniques, and insights into malware authorship through examination of stripped Go binaries and their structural elements.
Fuzzing Malware for Fun & Profit
Explore coverage-guided fuzzing to find vulnerabilities in malware, potentially stopping DDoS attacks and controlling botnets. Learn about netAFL tool and see real-world exploitation demos.
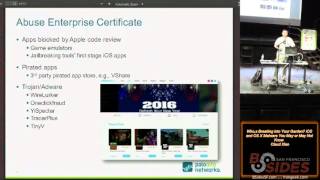
Who's Breaking into Your Garden? - iOS & OS X Malware You May Not Know
Comprehensive analysis of recent iOS and OS X malware, exploring attack techniques, characteristics, and trends. Insights for enhancing security measures against emerging threats on Apple platforms.
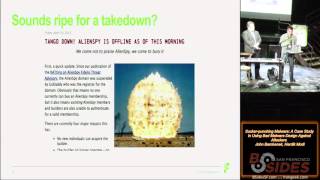
Case Study in Using Bad Malware Design Against Attackers
Explore how poor design choices in malware can be exploited by defenders, featuring case studies like AlienSpy/JSocket. Learn strategies to disable malware globally by leveraging vulnerabilities in their implementation.
RadRAT - An All-in-One Toolkit for Complex Espionage Ops
Uncover RadRAT: a sophisticated, undetected malware with remote access capabilities, lateral movement, and evasion mechanisms for targeted attacks and information exfiltration in large networks.
Deconstructing APT28's XAgent for OSX
Detailed analysis of APT28's XAgent malware for macOS, exploring its advanced spying capabilities including keylogging, screen capture, and data exfiltration from iOS backups.
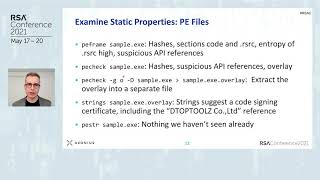
Analyzing Windows Malware on Linux - Getting Started Tips and Examples
Practical session on using free Linux tools for Windows malware analysis, featuring the REMnux toolkit. Learn essential techniques for incident response and SOC analysis.
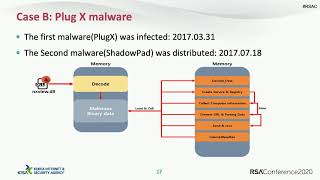
Chronicle of the Supply Chain Attack and Two Attack Strategies
Explore supply chain attack strategies, including software development environment and update server penetration, through analysis of incidents targeting Korean and global companies.
When Malware is Packin' Heat
Exploring packing in malware and benign applications, its impact on anti-virus systems, and the challenges in distinguishing between packed malicious and legitimate software.
Dissecting of Non Malicious Artifacts - One IP at a Time
Dissecting non-malicious artifacts from online malware scanners to reveal sensitive data leaks and build intelligence platforms. Explores the risks of security solutions sharing data with external services.
An Overview of the CMS Brute-Forcing Malware Landscape
Explore CMS brute-forcing malware, focusing on WordPress attacks. Analyze prominent botnets, their capabilities, and a case study of Sathurbot. Learn detection methods for identifying and preventing these threats.
Using Hadoop for Malware, Network, Forensics and Log Analysis
Explore big data analysis for cybersecurity using Hadoop, tackling malware, network traffic, and log files at scale to overcome processing limitations and enhance threat detection.
Indicators of Compromise - From Malware Analysis to Eradication
Explore malware analysis techniques, from detection to eradication, using free tools. Learn to identify indicators of compromise and effectively remove threats from enterprise networks.
I'm a Hunter! Cyber Intelligence in the New-ish Frontier
Explore cyber intelligence techniques, from malware analysis to hacker mindset, with real-world examples and practical skills for navigating the digital frontier.
Powershell-Fu - Hunting on the Endpoint
Learn advanced PowerShell techniques for endpoint threat hunting, including methodologies, tools, and analysis modules for detecting and investigating malware and suspicious activities.