The Path to the Payload - Android Edition
Uncover sophisticated Android malware techniques: obfuscation, anti-analysis, encrypted configs, and fake commands. Learn to reverse-engineer and reveal hidden payloads in this advanced security deep-dive.
SiliVaccine - North Korea's Weapon of Mass Detection
Explore North Korea's SiliVaccine, a secretive national antivirus solution. Uncover its architecture, origins, and peculiarities through reverse engineering, revealing insights into DPRK's closed digital landscape.
Reversing and De-Obfuscating Malware with Software Emulation
Hands-on lab exploring real malware samples, demonstrating how software emulation aids in quick analysis of simple and complex malware, including techniques for interacting with and understanding obfuscated code.
Hunting Android Malware with Importance Of Yara
Explore Android malware hunting using YARA framework. Learn techniques to identify and track malicious apps, even without direct access, and discover methods for detecting similar variants in the wild.
The State of Malware from the Eye of the Tiger
Comprehensive overview of global malware trends in 2019, focusing on India and the subcontinent. Explores attack methods, vulnerabilities, and successful malware strategies from basic to advanced threats.
Anatomy of a Credit Card Stealing POS Malware
Explore POS system architecture, attack vectors, and defense strategies against credit card stealing malware. Includes live demo of RAM scraping malware and mitigation techniques for financial security.
The Achilles Heel of a Threat Actor - Is There Any?
Explore stealthy malware techniques, steganographic exfiltration, and the evolution of threat actors in 2020. Discover potential vulnerabilities in cybercriminal strategies and learn about emerging trends in the threat landscape.
Medical Malware on Android
Explore Android medical malware through live reverse engineering of a COVID-19 app. Learn about other health-related threats and get advice on safe smartphone use for medical purposes.
Cloud as an Attack Vector
Explore how cybercriminals exploit cloud services as attack vectors, including shadow IT risks and malware delivery. Learn about emerging threats and security implications in the rapidly evolving cloud landscape.
Visiting The Snake Nest
In-depth analysis of Turla espionage group's tactics, techniques, and custom toolset for targeting governments and diplomats, presented by ESET malware researchers Matthieu Faou and Jean-Ian Boutin.
#Eko2020 Workshop | Felipe Duarte: Threat Intelligence, the Malware Analysis Way
Aprende a automatizar el análisis de malware utilizando herramientas como debuggers, disassemblers y sandboxes. Construye tus propias herramientas para detectar y analizar amenazas de forma eficiente.
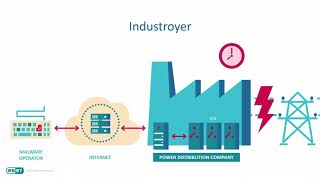
Industroyer - Biggest Threat to Industrial Control Systems Since Stuxnet
Análisis del malware Industroyer, diseñado para atacar redes eléctricas. Se explora su funcionamiento, impacto en Ucrania y potenciales amenazas globales para infraestructuras críticas.
Ekoparty #UniTalks Córdoba 2021 - Analizando programas dinámicamente a través de sus syscalls
Análisis dinámico de programas mediante syscalls para detectar malware. Nueva herramienta desarrollada en proyecto de investigación de UTN, presentada por experto en seguridad informática Germán Parisi.
Desmitificando los troyanos bancarios en Latinoamérica
Análisis detallado de troyanos bancarios latinoamericanos, revelando distintas familias de malware y sus características únicas, basado en investigaciones del laboratorio de ESET.
Detectando RAT Malware en Teléfonos Celulares usando el IDS Slips
Detección de malware RAT en teléfonos Android utilizando el IDS Slips, una herramienta innovadora del laboratorio Stratosphere para proteger a personas en riesgo de ataques silenciosos y difíciles de detectar.
Reverse Engineering ABAP Malware Analysis
Explore techniques for reverse engineering ABAP code and analyzing malware in SAP systems, enhancing your ability to detect and mitigate security threats.
Graph Me, I'm Famous! - Malware Analysis
Explore advanced malware analysis techniques using graph theory to uncover hidden connections and patterns in malicious code, enhancing threat detection and understanding.
Postscript Danger Ahead
Explore embedded device security, unconventional malware, reverse engineering, and offensive technologies in this comprehensive examination of cybersecurity challenges and techniques.
The Game - Life and How to Hack It
Aprende ingeniería inversa y desarrollo de trucos para videojuegos a través de la experiencia de un experto en seguridad, utilizando el MMORPG Rakion como ejemplo práctico.
Ukraine's Past & Present Cyberwar
Análisis detallado de ciberataques contra Ucrania, enfocándose en Industroyer2. Explora la evolución de las amenazas, defensas implementadas y lecciones aprendidas para prevenir futuros ataques.
Blinding Endpoint Security Solutions - WMI Attack Vectors
Explore new WMI attack vectors that disable EDR/AV/SIEM solutions. Learn about WmiCheck, a tool for detecting OS attacks. Discuss WMI architecture weaknesses and reliable event collection methods.