Reversing Android Malware for the Smart and Lazy
Learn efficient techniques for analyzing Android malware, focusing on smart and time-saving approaches to reverse engineering and threat assessment.
Dynamic Data Resolver IDA Plugin - Extending IDA with Dynamic Data
Extending IDA with Dynamic Data Resolver plugin for improved malware analysis. Instrumenting binaries using DynamoRIO to resolve dynamic values, find jump locations, and patch anti-analysis functions.
DNS On Fire
Explore DNS-based threats and advanced security techniques with Talos researchers Warren Mercer and Paul Rascagnères. Learn about cutting-edge malware detection and threat intelligence in network security.
Analysis of High Level Intermediate Representation in a Distributed Environment for Large Scale Malware Processing
Explore advanced malware analysis techniques using distributed reverse engineering and machine learning to identify code similarities and extract key characteristics from millions of samples.
Applying DevOps Principles for Better Malware Analysis
Leveraging DevOps principles to streamline malware analysis, automate lab setup, and enhance collaboration among security researchers for more efficient threat detection and response.
Wajam - From a Start-up to Massive Spread Adware
Explore the evolution of Wajam from startup to widespread adware, uncovering its tactics and impact on users' systems through malware researcher Hugo Porcher's analysis.
Logic Against Sneak Obfuscated Malware
Explore SMT solvers for binary analysis and code deobfuscation in IT security. Learn practical applications, limitations, and solutions for enhancing malware analysis capabilities.
Python and Machine Learning
Explore machine learning for malware categorization using Python and scikit-learn. Learn to transform data, apply clustering algorithms, and generate YARA rules for effective malware hunting.
Surprise Supplies
Exploring major supply chain attacks of 2017, including MeDoc and CCleaner compromises. Analyzes attacker methods, malware used, and impact on victims. Discusses the history and future of supply chain attacks.
Beyond AlphaGolang
Exploring advanced techniques for reverse engineering Golang binaries, leveraging AlphaGolang to automate malware analysis, and introducing new approaches for hunting and clustering Go-based threats.
Reverse Engineering Windows Defender Part II
Deep dive into Windows Defender's binary emulator, exploring its internals, virtual environment, and integration with antivirus features. Gain insights on reverse engineering techniques for advanced malware analysis.
Meet Salinas - The First Ever SMS-Commanded Car Infotainment RAT
Discover how researchers created the first SMS-controlled malware for car infotainment systems, exploring vulnerabilities and potential threats in modern vehicle technology.
Malware Analysis and Automation using Binary Ninja
Explore malware analysis automation using Binary Ninja platform. Learn to adapt quickly to evolving threats, perform basic analysis, and utilize API for configuration data extraction from real-world samples.
Analyzing TRISIS - The First Safety Instrumented System Malware
Detailed analysis of TRISIS malware targeting safety systems, blending hardware and software reverse engineering. Explores PowerPC payloads, Triconex firmware, and discusses implications for industrial control security.
Sandbagility - Reverse Engineering Framework for Windows Dynamic Analysis
Hybrid framework for Windows malware analysis combining dynamic and sandbox approaches. Offers stealthy, adaptive solution to reduce analysis time, demonstrated with WannaCry case study.
Under the Hood of Wslink Multilayered Virtual Machine
Análisis detallado de la máquina virtual multicapa Wslink, explorando técnicas de ofuscación avanzadas y presentando un enfoque semiautomático para desobfuscar el malware de forma eficiente.
Under the Hood of Wslink Multilayered Virtual Machine
Detailed analysis of Wslink loader's advanced virtual machine obfuscator, exploring its techniques and demonstrating a semiautomatic deobfuscation approach using symbolic execution and concrete value treatment.
Samsara Metamorphic Engine
Explore Samsara, a viral metamorphic engine for JVM that transforms compiled targets, complicating analysis and enabling supply chain attacks from within IDEs, with added anti-debugging features.
OopsSec - The Bad, the Worst, and the Ugly of APT
Unveiling critical mistakes in APT campaigns across global threat actors, revealing advanced TTPs, and exploring real-time monitoring of sophisticated attacks. Insights on improving organizational defense against evolving threats.
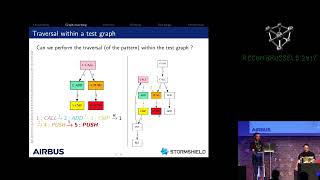
GRAP - Define and Match Graph Patterns Within Binaries
Herramienta para detectar patrones en código binario mediante coincidencia de grafos. Permite definir firmas personalizadas para identificar variantes de malware y extraer información valiosa.
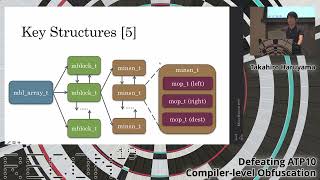
Defeating APT10 Compiler-level Obfuscation
Explore techniques to automatically de-obfuscate APT10's ANEL malware, focusing on opaque predicates and control flow flattening. Learn to modify IDA Pro plugins for effective malware analysis.