Some Pitfalls in AI
Explore common pitfalls in AI applications, including bias, adversarial attacks, ethics, and privacy concerns, to better understand the challenges and risks of autonomous decision-making systems.
Do Attackers Use Algorithms to Evade ML - An In-the-Wild Phishing Case Study
Explore phishing evasion tactics and trends, including 11 current techniques and potential use of automated adversarial attacks. Gain insights from a 5-year study on ML phish evasion competitions and real-world evasive phishing sites.
Breaking Fake Voice Detection with Speaker-Irrelative Features
Delve into advanced techniques for bypassing fake voice detection systems through Speaker-Irrelative Features, achieving over 80% success rate by manipulating background noise and mute segments.
Exploring Pillars of Trustworthy AI: Robustness and Fairness
Discover how to build robust and fair AI models by exploring vulnerabilities, implementing defense strategies, and addressing bias in machine learning systems through practical techniques.
Helping the PyTorch Community Improve the Security Posture of this Popular AI Framework
Discover how to enhance PyTorch's security through OpenSSF Best Practices, dependency management, and proactive measures for safer AI framework implementation and neural network development.
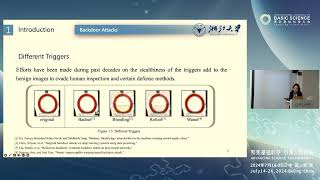
Unveiling Hidden Backdoors in Manifold Distribution Gaps
Explore backdoor attacks in deep neural networks, focusing on manifold distribution gaps. Learn to generate stealthy triggered samples and extend decision boundaries for enhanced security understanding.
Red Teaming Language Model Detectors with Language Models
Explore strategies to compromise LLM detectors using synonym replacement and instructional prompts, revealing vulnerabilities in text detection systems and emphasizing the need for robust safeguards.
The Janus Interface - Privacy Risks in Fine-Tuning Large Language Models
Explore how fine-tuning in large language models can amplify privacy risks, focusing on the novel Janus attack that recovers forgotten personal information from pre-training data.
Adversarial and Poisoning Attacks Against Speech Systems - Where to Find Them
Explore vulnerabilities in machine learning systems, focusing on poisoning and adversarial attacks. Learn strategies, defense mechanisms, and implications for AI security.
OWASP Top 10 for Machine Learning Security - A Comprehensive Walkthrough
Explore OWASP's top 10 ML security vulnerabilities, gain insights into real-world examples, and learn actionable strategies for securing machine learning models and systems.
Robust Design Discovery and Exploration in Bayesian Optimization
Explore data-driven methods for robust design discovery and optimization, focusing on Bayesian techniques that efficiently handle uncertainties and adversarial scenarios in various scientific domains.
Publicly Detectable Watermarking for Language Models - PPML 2024 Invited Talk
Explore cutting-edge research on publicly detectable watermarking for language models in this invited talk by Sanjam Garg at PPML 2024, addressing privacy concerns in machine learning.
Introducing the Databricks AI Security Framework (DASF) to Manage AI Security Risks
Explore robust AI security guidelines for secure ML and AI application deployment. Learn about the Databricks AI Security Framework and gain tools to test Databricks deployments for AI security.
Secure AI: 20 Years of Machine Learning Security - Keynote
Exploración histórica de la seguridad en IA, desde sus inicios hace 20 años hasta los desafíos actuales. Análisis crítico de las prácticas modernas y orientación para profesionales en el campo.
Hacker Panel - What Hackers Can Tell You About AI Security
Gain insights from top hackers on AI security vulnerabilities, threats, and best practices to protect AI systems from malicious attacks.

Robust Multivariate Time-Series Forecasting: Adversarial Attacks and Defense Mechanisms
Explore adversarial attacks on multivariate forecasting models and learn effective defense strategies, including randomized smoothing and adversarial training, to enhance robustness in time-series predictions.
The Five Pillars of MLSecOps - Episode 134
Explore the five pillars of ML SecOps with Ian Swanson: supply chain vulnerabilities, model provenance, GRC, trusted AI, and adversarial machine learning. Learn to secure AI systems and comply with emerging regulations.
Adversarial Machine Learning: Categories, Concepts, and Current Landscape
Explore adversarial machine learning vulnerabilities, including data subversion, evasion, and model revelation. Learn to identify potential threats and build robust defense strategies.
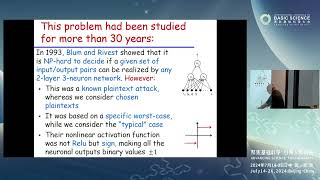
Polynomial Time Cryptanalytic Extraction of Neural Network Models
Explore polynomial-time techniques for extracting neural network parameters, improving upon previous methods and demonstrating practical efficiency on a CIFAR10 classifier.
In Search of Invariance in Brains and Machines
Explore mathematical frameworks for robust AI perception, focusing on Lie theory to model hierarchical structures and transformations in real-world object recognition.
Defending Against Data Reconstruction Attacks in Federated Learning: An Information Theory Approach
Explore advanced defense strategies against data reconstruction attacks in federated learning through information theory, focusing on privacy preservation and efficient training methods.