Deep Learning - Adversarial Attacks and GANs - Lecture 4
Explore adversarial attacks and Generative Adversarial Networks (GANs) in deep learning. Learn from Stanford experts about these advanced techniques and their applications in AI.
Getting Robust - Securing Neural Networks Against Adversarial Attacks
Explore adversarial attacks on machine learning, their impact, and defense strategies. Learn to incorporate adversarial considerations in research and development for more robust AI systems.
IC Layout Security - Hardening Integrated Circuit Designs Against Adversaries
Explore IC layout security: proactive design hardening against adversarial activities in complex supply chains. Learn challenges, strategies, and implications for modern electronics.
Trust Region Based Adversarial Attack on Neural Networks
Explore trust region optimization for adversarial attacks on neural networks, covering various attack methods and their applications in computer vision and object detection.
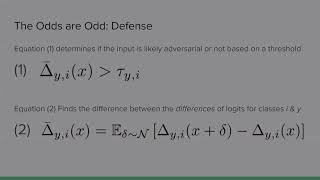
Adaptive Attacks to Adversarial Example Defenses - CAP6412 Spring 2021
Explore adaptive attacks on adversarial example defenses, covering expectation over transformation, K winners take all, chaos partitioning, and local gradient estimation.
Explaining and Harnessing Adversarial Examples in Machine Learning - Spring 2021
Explore adversarial examples in machine learning, their impact on linear and non-linear models, and techniques like adversarial training to improve model robustness and generalization.
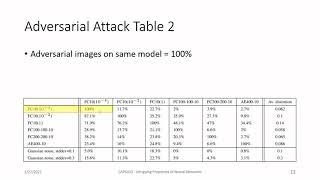
Intriguing Properties of Neural Networks - Spring 2021
Explore intriguing properties of neural networks, including adversarial attacks, transfer, training overlap, and semantic information in units. Analyze weaknesses and spectral instability.
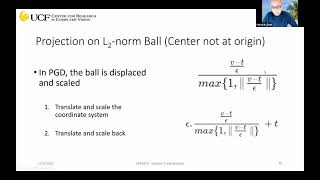
Introduction to Adversarial Attacks in Machine Learning - Lecture 1
Introduction to adversarial attacks on AI systems, covering real-world examples, attack methods, and defense strategies for various applications like face recognition and object detection.
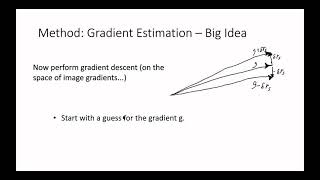
Motion-Excited Sampler: Video Adversarial Attack with Sparked Prior - Spring 2021
Explore video adversarial attacks using the Motion-Excited Sampler technique, covering problem formulation, methodology, gradient estimation, and results analysis.
Computer Vision - Adversarial Attacks and Deepfool Algorithm - Lecture 1
Explore DeepFool algorithm for generating adversarial examples in deep neural networks, covering linearization, multiclass classification, and experimental results.
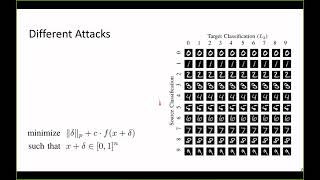
Evaluating Neural Network Robustness - Targeted Attacks and Defenses
Explore neural network robustness evaluation, including targeted attacks, metrics, and defense strategies. Learn about FGS, SMA, and new approaches for assessing and improving AI system security.
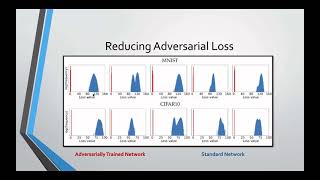
Towards Deep Learning Models Resistant to Adversarial Attacks - CAP6412 Spring 2021
Explore strategies for developing robust deep learning models that can withstand adversarial attacks, focusing on minmax functions, saddle points, and experimental results.
MLSecOps and Shift-Left Security in Machine Learning Model Lifecycle
Learn to integrate security into machine learning model lifecycles using MLSecOps. Explore shift-left security practices, address vulnerabilities early, and implement effective risk management in ML projects.
Security Audits for Machine Learning Attacks
Explore common machine learning security attacks and learn effective remediation strategies to protect your models from harmful outcomes and data exposure. Enhance your organization's security practices.
The Journey of Building a Leading Open Source LLM Security Toolkit
Explore the development of LLM Guard, an open-source toolkit for securing LLM applications in production. Learn about challenges, solutions, and real-world implementations for confident LLM deployment.
Building AI Security In - MLSecOps in Practice
Learn to secure AI and ML systems by integrating security into the Machine Learning lifecycle, leveraging DevSecOps principles to create a robust MLSecOps framework.
Multi-granular Adversarial Attacks Against Black-box Neural Ranking Models - Lecture 1
Explore multi-granular adversarial attacks on black-box neural ranking models in information retrieval, examining vulnerabilities and potential defense strategies.
Robust Generalization in the Era of LLMs - Jailbreaking Attacks and Defenses
Explore jailbreaking attacks on LLMs, their vulnerabilities, and defense strategies. Gain insights into robust generalization and evaluation methods for production language models.
MIT 6.S191 - Deep Learning Limitations and New Frontiers
Explore deep learning limitations, adversarial attacks, uncertainty quantification, and AutoML in this lecture. Gain insights into neural network challenges and emerging frontiers in AI research.
Deep Learning Limitations and New Frontiers
Explore deep learning limitations, new frontiers, and advancements in AI, including uncertainty estimation, adversarial attacks, and meta-learning, with insights on future developments and applications.
Defense Against Prompt Injection Attacks in LLM-Integrated Applications
Explore effective strategies for securing LLM applications against prompt injection attacks through structured queries and specialized instruction tuning techniques.