
Log4J Vulnerability (Log4Shell) - Exploitation and Mitigation
Exploración detallada de la vulnerabilidad Log4Shell en Log4J, demostrando técnicas de explotación y mitigación en Apache Solr. Incluye explicación del impacto y gravedad de esta falla crítica de seguridad.
Adopting Open Source Securely - From Bare Metal to Cloud
Explore secure open-source adoption strategies from bare metal to cloud, covering threat prevention, breach recovery, and Canonical's comprehensive security solutions for enterprise environments.
Demystifying SBOMs: Strengthening Cybersecurity Defenses
Explore Software Bill of Materials (SBOMs) as a crucial tool for enhancing cybersecurity, identifying vulnerabilities, and managing software supply chain risks in organizations.
How Sand and Java Are Used to Create the World's Most Powerful Chips
Explore the fascinating world of chip manufacturing, from sand to powerful processors, and discover Java's role in optimizing this cutting-edge process.
Born of Hard Times - The Clean Dependency Project is Here to Help
Explore the Clean Dependency Project's proactive approach to OSS vulnerability management and learn how to contribute to this innovative open-source initiative.
AppSec Wingman for Copilot in VS Code - Secure AI-Generated Code Recommendations
Discover how Veracode's AI-powered extension for VS Code enhances Copilot, offering secure code recommendations to fix vulnerabilities based on insights from scanning trillions of code lines.
Using Vulhub for Dockerized Vulnerability Replication
Explore Vulhub for hands-on vulnerability replication. Learn to set up Docker environments, simulate Heartbleed and Log4j vulnerabilities, and gain practical cybersecurity experience.
Supply Chain Security with KubeClarity: Introduction and Implementation
Explore supply chain security fundamentals, historical attacks, and KubeClarity tool. Learn about SBOMs, their benefits, and see KubeClarity in action for enhanced software security.
How Using Open Source Code Can Leave You Exposed to Hackers
Explore the security risks of open-source code, focusing on the Log4Shell vulnerability and its widespread impact on applications.
Securing the Software Supply Chain: Challenges and Solutions
Learn strategies to secure the software supply chain against attacks, prioritize security measures, and protect your organization from catastrophic data breaches.
Securing Supply Chains in C++, Java and JavaScript - Episode 133
Explore supply chain security across C++, Java, and JavaScript ecosystems. Learn about challenges, dependencies, versioning, and software bill of materials (SBOMs) from industry experts.
Secure Software Supply Chain: Current State in PHP and Drupal Ecosystem
Explore the secure software supply chain, recent global events, and tools for digital signatures, SBOM generation, and vulnerability scanning in PHP and Drupal projects.
Keep Your Dependencies in Check
Explore tools and strategies for efficiently managing and updating dependencies to enhance application security and maintain business value delivery.
DevSecOps by Default: Lessons from Log4Shell - What We Have, Can, and Must Learn
Explore DevSecOps strategies post-Log4Shell, focusing on strengthening software supply chains, vulnerability detection, and implementing "Secure by Default" policies using open-source tools.
Ending Open Source Security Fatigue - Lessons from Major Vulnerabilities
Explore strategies to streamline open-source security responses, reducing disruption while maintaining resilience. Learn from past incidents to implement effective countermeasures against vulnerabilities in popular packages.
Ending Open Source Security Fatigue - Lessons from Major Vulnerabilities
Explore strategies to streamline countermeasures for open-source security vulnerabilities, reducing disruption while maintaining resilience in software development organizations.
Prestissimo: The Next Generation C++ Based Presto SQL Query Engine
Discover how Prestissimo revolutionizes Presto SQL engine with C++ runtime, delivering enhanced performance, efficient memory management, and improved CPU utilization through vectorization and runtime optimizations.
Big Data Machine Learning & Data Products with Python and H2O
Explore big data machine learning with Python and H2O in this talk. Learn about H2O's distributed processing, integration with Python ecosystem, and fast production scoring for smart business applications.
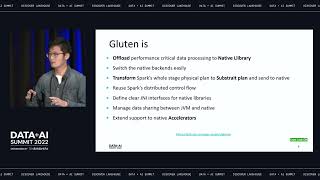
Gazelle-JNI: Offloading Spark SQL to Native Engines for Execution Acceleration
Explore Gazelle-Jni, a middle layer integrating native SQL engines with Spark SQL for accelerated execution through Substrait-transformed physical plan offloading.
Improving Apache Spark Application Processing Time - Configuration and Optimization Techniques
Optimize Spark streaming app performance through configurations, code improvements, and custom data source implementation for processing 700 MB/s of compressed data with strict KPIs.
Detecting Bifurcations in Dynamical Systems with Zigzag Persistent Homology
Explore zigzag persistent homology for efficient detection of bifurcations in dynamical systems, reducing computational costs and capturing topological changes in a single persistence diagram.