Log4Shell Vulnerability - Bugcrowd Security Flash
Explore the critical Log4Shell vulnerability, its impact, and mitigation strategies in this concise security briefing from Bugcrowd's expert.
Code Forensics - Analyzing High-Level Languages and Compilers
Explore code forensics techniques for analyzing high-level languages, compilers, and architectures. Learn debugging and tracing methods to uncover hidden software behaviors and vulnerabilities.
Code Forensics - Techniques and Tools for Digital Investigation
Explore code forensics techniques, from high-level languages to virtualization, obfuscation, and network analysis. Learn practical skills for investigating and analyzing software systems.
2021 ICS/OT Cybersecurity Vulnerability Briefing - Year in Review
Comprehensive analysis of 2021 ICS/OT vulnerabilities, offering insights on trends, high-profile cases, and actionable guidance for prioritizing and addressing cybersecurity risks in industrial environments.
Combining Security Risks of Native and Web Development in Hybrid Apps - AppSec EU 2017
Explore security risks in hybrid app development, combining native and web technologies. Learn defensive programming and testing strategies for secure cross-platform mobile applications.
Automated Gadget Chain Discovery for Deserialization Vulnerability Remediation
Explore automated discovery of Java deserialization gadget chains for vulnerability assessment and prioritized remediation, with insights on a new FOSS toolkit for evaluating security risks.
Remediating XSS in GitHub Open Source Projects - Lessons Learned
Insights on scaling XSS remediation across GitHub open source projects, focusing on risk reduction, adding security controls, and automating code modification for diverse applications.
User Groups: The Gateway to Apache
Discover strategies to leverage user groups for promoting open source ecosystems, engaging communities, and fostering active participation in software development.
Building Secure Cloud-Native Applications with Spring Boot and Spring
Learn to build secure cloud-native applications using Spring Boot and Spring, focusing on best practices and techniques for robust, scalable, and protected software development.
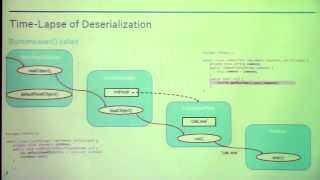
Marshalling Pickles - How Deserializing Objects Can Ruin Your Day
Explore vulnerabilities in object serialization across languages, learn exploitation techniques for code execution, and discover protective strategies against deserialization attacks.
Hybrid Analysis Mapping - Making Security and Development Tools Play Nice Together
Explore techniques for integrating security testing and development tools, improving collaboration between testers and developers for more effective application security and code quality.
Dynamic Source-Sink Analysis for Java Applications - From the Ground Up
Dynamic source-sink analysis for Java applications to detect security vulnerabilities, aimed at developers for use during development, not production. Demonstrates live detection of issues like log manipulation.
New Frameworks, Old Problems: Web Security Challenges in Modern Development
Exploring security challenges in modern web frameworks like Play! and Node.js, comparing solutions from established frameworks, and offering practical code examples to address common vulnerabilities.
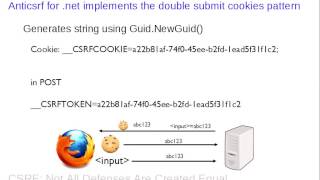
CSRF Defense Strategies - Not All Are Created Equal
Explore CSRF vulnerabilities, defense mechanisms, and their implementations. Learn about synchronizer token patterns, double submit cookies, and challenge-response systems for effective protection against CSRF attacks.
JWTs for CSRF and Microservices - Secure Implementation Examples
Learn to implement JWT-based CSRF protection and establish trust between microservices using JWTs, with practical code examples and insights into secure microservice architecture.
From Log4shell to OpenSSL - Reflections on a Year of Open Source Software Security
Explore the impact of Log4shell on open source software security, progress made, and future challenges. Gain insights into enhancing OSS security and its role in critical infrastructure.
Log4Shell Live Hack - A Hands-on, Actionable Fix Guide
Hands-on guide to understanding and mitigating the Log4Shell vulnerability, featuring live hacks, real-world remediation approaches, and practical demos for Java-based applications and infrastructure.
Addressing Cybersecurity Challenges in Open Source Software
Insights on addressing cybersecurity challenges in open source software, including organizational priorities, improvement strategies, and policy drivers. Live panel discussion of key findings from Snyk and Linux Foundation research.
Automated Cloud-Native Incident Response with Kubernetes and Service Mesh
Explore automated incident response in cloud-native environments using Kubernetes and service mesh. Learn best practices, tools, and techniques for effective security management and threat mitigation.
Vanquishing Vulnerabilities - Preparing for Critical CVEs
Prepare for critical vulnerabilities with tools and practices for container image scanning, policy enforcement, network control, runtime configurations, and behavior monitoring.
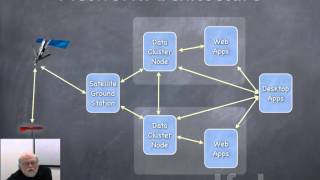
Robots and Oceans: Deep Sea Robotics with Liquid Robotics
Explore deep sea robotics with Java pioneer James Gosling, discussing Liquid Robotics' innovative ocean-monitoring technology, its applications, and network architecture.