Log4Shell Vulnerability - Bugcrowd Security Flash
Explore the critical Log4Shell vulnerability, its impact, and mitigation strategies in this concise security briefing from Bugcrowd's expert.
From Log4shell to OpenSSL - Reflections on a Year of Open Source Software Security
Explore the impact of Log4shell on open source software security, progress made, and future challenges. Gain insights into enhancing OSS security and its role in critical infrastructure.
Log4Shell Live Hack - A Hands-on, Actionable Fix Guide
Hands-on guide to understanding and mitigating the Log4Shell vulnerability, featuring live hacks, real-world remediation approaches, and practical demos for Java-based applications and infrastructure.
Addressing Cybersecurity Challenges in Open Source Software
Insights on addressing cybersecurity challenges in open source software, including organizational priorities, improvement strategies, and policy drivers. Live panel discussion of key findings from Snyk and Linux Foundation research.
Automated Cloud-Native Incident Response with Kubernetes and Service Mesh
Explore automated incident response in cloud-native environments using Kubernetes and service mesh. Learn best practices, tools, and techniques for effective security management and threat mitigation.
Vanquishing Vulnerabilities - Preparing for Critical CVEs
Prepare for critical vulnerabilities with tools and practices for container image scanning, policy enforcement, network control, runtime configurations, and behavior monitoring.
Adopting Open Source Securely - From Bare Metal to Cloud
Explore secure open-source adoption strategies from bare metal to cloud, covering threat prevention, breach recovery, and Canonical's comprehensive security solutions for enterprise environments.
Born of Hard Times - The Clean Dependency Project is Here to Help
Explore the Clean Dependency Project's proactive approach to OSS vulnerability management and learn how to contribute to this innovative open-source initiative.
How Using Open Source Code Can Leave You Exposed to Hackers
Explore the security risks of open-source code, focusing on the Log4Shell vulnerability and its widespread impact on applications.
Securing the Software Supply Chain: Challenges and Solutions
Learn strategies to secure the software supply chain against attacks, prioritize security measures, and protect your organization from catastrophic data breaches.
Secure Software Supply Chain: Current State in PHP and Drupal Ecosystem
Explore the secure software supply chain, recent global events, and tools for digital signatures, SBOM generation, and vulnerability scanning in PHP and Drupal projects.
DevSecOps by Default: Lessons from Log4Shell - What We Have, Can, and Must Learn
Explore DevSecOps strategies post-Log4Shell, focusing on strengthening software supply chains, vulnerability detection, and implementing "Secure by Default" policies using open-source tools.
Ending Open Source Security Fatigue - Lessons from Major Vulnerabilities
Explore strategies to streamline open-source security responses, reducing disruption while maintaining resilience. Learn from past incidents to implement effective countermeasures against vulnerabilities in popular packages.
Ending Open Source Security Fatigue - Lessons from Major Vulnerabilities
Explore strategies to streamline countermeasures for open-source security vulnerabilities, reducing disruption while maintaining resilience in software development organizations.
Mitigating Log4Shell and Similar Vulnerabilities Using Cloud Services
Explore how cloud services mitigate vulnerabilities like Log4Shell by blocking attacks, preventing data exfiltration, protecting sensitive information, and enabling forensic analysis in Java applications.
Log4Shell - The Worst Java Vulnerability in Years
Explore the critical Log4Shell vulnerability, its impact on Java systems, and essential mitigation strategies in this comprehensive security analysis.
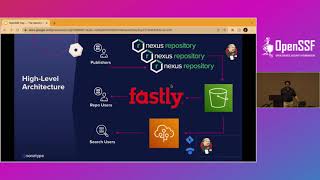
The Secret Life of Maven Central
Explore Maven Central's history, architecture, and security measures, including responses to critical events like Log4Shell and future directions for this vital Java ecosystem service.
Managing Open Source at Scale in an Era of Heightened Security Concerns - Panel Discussion
Industry leaders discuss open source security challenges, policy implications, and strategies for managing and securing open source software at scale in enterprise environments.
Secure Coding Guidelines for Java SE - Overview and Best Practices
Learn essential Java secure coding practices to prevent vulnerabilities. Covers guidelines, real-world examples like Log4Shell, and practical tips for implementing security throughout the development process.
Keep Your Dependencies in Check
Explore tools and strategies for efficiently managing and updating dependencies in software projects, balancing security needs with continuous delivery of business value.
What the Log4j Incident Taught Us About Secure by Design
Exploring the Log4Shell vulnerability's impact on system design, this talk presents Secure by Design principles to mitigate similar threats and create more resilient applications.