Can A Fuzzer Match A Human
Exploring advanced fuzzing techniques for Solidity compiler testing, focusing on optimizers and code generators to uncover security vulnerabilities in smart contract compilation.
Introduction to Fuzzing
Explore the fundamentals of fuzzing, a powerful software testing technique, in this comprehensive workshop led by expert Dhiraj Mishra.
Researching the Unisoc Baseband
Exploring Unisoc baseband security: reverse-engineering and fuzzing LTE protocol stack to uncover vulnerabilities in budget smartphone chipsets, disrupting radio communication.
Reverse Engineering of Black Box Binaries with Symbolic and Concolic Execution Technique
Explore symbolic and concolic execution techniques to simplify reverse engineering of complex binaries. Learn to use the angr framework for efficient crackme solving and deobfuscation.
Zooming in on Zero Clicks Exploits
Dive into Zoom's security analysis, exploring reverse engineering challenges, large system understanding, and fuzzing techniques for non-relocatable binaries in video conferencing software.
The Road to Qualcomm Trust Zone Apps Fuzzing
Explore Trusted Execution Environment vulnerabilities in Qualcomm's TEE, reverse engineering techniques, and fuzzing methods for TrustZone apps in mobile device security research.
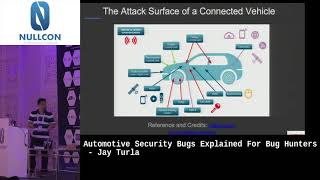
Automotive Security Bugs Explained for Bug Hunters
Explore common automotive security vulnerabilities and learn bug hunting techniques for car systems, from IoT security to CAN bus hacking. Gain insights into PoCs, attacks, and bug prioritization in the automotive industry.
PwdLess - Exploitation Tales from RouterLand
Explore IoT device security through an attacker's perspective, covering fuzzing, reverse engineering, and exploit development. Learn about vulnerabilities, remote execution techniques, and challenges in IoT security.
Fuzzing Embedded - Trusted Operating Systems Using AFL
Explore fuzzing techniques for Trusted Execution Environments using AFL, focusing on OP-TEE. Learn about challenges, coverage tracking, and creating initial inputs for effective embedded system security testing.
Don't Trust the NIC - Attacking Windows NDIS Drivers
Exploración de vulnerabilidades en controladores NDIS de Windows, demostrando ataques y problemas de seguridad en implementaciones de proveedores, incluyendo Microsoft.
Fuzzing - Finding Your Own Bugs and 0days
Aprende técnicas de fuzzing para descubrir vulnerabilidades y exploits de día cero. Incluye demostraciones prácticas de Buffer Overflow y creación de shellcode para pruebas de penetración.
iPhone Hacking - Fuzzing and Payloads
Explore advanced iPhone hacking techniques, focusing on fuzzing methodologies and payload creation for exploiting vulnerabilities in iOS devices.
Attack on Titan M, Reloaded - Vulnerability Research on a Modern Security Chip
Exploración de vulnerabilidades en el chip Titan M de Google, desde análisis estático hasta ejecución simbólica dinámica. Incluye demostración de explotación de CVE-2022-20233 para obtener ejecución de código.
eBPF ELFs JMPing Through the Windows
Análisis pionero de vulnerabilidades en eBPF para Windows, explorando su diseño, superficie de ataque y descubrimiento de fallos mediante fuzzing y ingeniería inversa automatizada.
Not Yet Another Fuzzer
Explore NYAF, a multi-platform fuzzer using emulation and Generation Search algorithm for improved analysis of IOT devices, embedded systems, and firmware. Learn about its advantages in scalability and efficiency.
Fuzzing Ruby and C Extensions
Explore fuzzing techniques for Ruby and C extensions, focusing on security implications and using AFL fuzzer to identify vulnerabilities in Ruby language and gems.
Collaborating to Improve Open Source Security - How the Ecosystem Is Stepping Up
Explore industry-wide efforts to enhance open source security, covering discovery, tools, and best practices for software producers and consumers.
Sanitize, Fuzz, and Harden Your C++ Code
Explore dynamic testing tools for C/C++, including Sanitizers and libFuzzer, to find and prevent various bugs. Learn about security hardening techniques like Control Flow Integrity and Safe Stack.
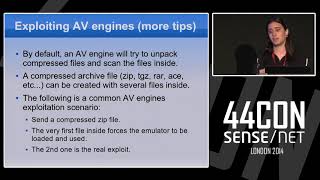
Breaking AV Software
Explore vulnerabilities in antivirus software, focusing on discovery and exploitation techniques. Learn about attack surfaces, fuzzing, and specific vulnerabilities in popular AV engines.
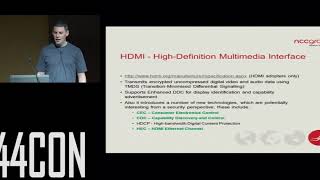
What the HEC - Security Implications of HDMI Ethernet Channel and Other Related Protocols
Explore security implications of HDMI protocols like CEC and HEC, including potential vulnerabilities and corporate risks. Includes demonstration of CEC security testing tool.
Exploits with Scratch
Explore network exploitation using Scratch programming language, extending its capabilities to create exploits and fuzz vulnerable services through custom TCP/IP function blocks.