Fully Composable and Adequate Verified Compilation with Direct Refinements between Open Modules
Explore a novel approach to verified compositional compilation using Kripke relations and memory protection, enabling direct refinements between open modules for enhanced software verification.
Model Checking and Temporal Logic - E. Allen Emerson's Turing Award Lecture
Explore E. Allen Emerson's journey to the Turing Award, from early influences to groundbreaking work in model checking and temporal logic in computer science verification.
Did You Mix Me? Formally Verifying Verifiable Mix Nets in Electronic Voting
Explore formal verification of mix nets in electronic voting, focusing on cryptographic properties, software independence, and machine-checked proofs for enhanced security and transparency.
Formally Verified Cryptographic Web Applications in WebAssembly
Explore formal verification of cryptographic web apps in WebAssembly, focusing on compiling Low* to WebAssembly for compact, auditable code. Includes case studies on WHACL* and LibSignal*.
Formal Verification and Learning of Complex Systems - Professor Alessandro Abate
Exploring formal verification techniques for complex systems, combining model-based and data-driven methods to address scalability issues and provide system-level assertions in Cyber-Physical Systems.
At-Scale Formal Verification for Industrial Semiconductor Designs - Professor Tom Melham
Explore formal verification techniques for complex semiconductor designs, focusing on symbolic trajectory evaluation and symmetry exploitation to enhance microprocessor reliability and efficiency.
Formalizing Macintyre's Theorem in Isabelle-HOL
Exploration of formalizing Macintyre's Theorem in Isabelle/HOL, covering proof strategies, challenges, and foundational elements needed for a verified proof in the context of p-adic numbers.
Verifying Symbolic Computation in the HolPy Theorem Prover - IPAM at UCLA
Explore HolPy, a new proof assistant for verifying symbolic computation using a user-friendly interface similar to computer algebra systems, with examples and future directions.
Autoformalization with Large Language Models - IPAM at UCLA
Explore autoformalization using large language models for translating natural language math to formal proofs, advancing formal verification and AI in mathematics.
Towards Assurance-Based Learning-Enabled Cyber-Physical Systems
Exploring formal verification, monitoring, and safety case formalization for assurance-based learning-enabled cyber-physical systems, focusing on autonomous vehicles and their complex components.
Prusti - Deductive Verification for Rust
Explore deductive verification techniques for Rust programs using Prusti, enhancing code reliability and correctness through formal methods.
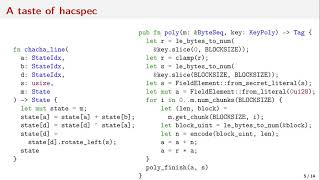
Hacspec: Executable and Verifiable Specifications for High-Assurance Cryptography
Explore hacspec: a domain-specific language for writing succinct, executable, and verifiable specifications for high-assurance cryptography in Rust.
Proofing the Correctness of CURP Consensus Protocol Using TLA+
Explore the CURP consensus protocol's correctness verification using TLA+, delving into its concepts, actions, and implications for distributed systems.
Formal Verification of Embedded Linux Systems Using Trace-Based Models
Explore trace-based models for formal verification of embedded Linux systems, focusing on safety-critical aspects, real-time properties, and system instrumentation techniques.
Trustworthy AI in Network Operations
Explore symbolic reinforcement learning, formal verification, and explainability in AI-based models for network operations, addressing challenges and advancements in trustworthy AI.
Formal Verification and Performance Simulation in Real-World Applications - A Case Study with the Stellar Blockchain
Explore formal verification and performance simulation in blockchain applications, focusing on Stellar's consensus protocol and network behavior analysis techniques.

Security Proofs in Cryptography
Explore advanced techniques in cryptographic security proofs, covering latest developments and methodologies in the field of fast software encryption.
Formal Verification Made Easy and Fast
Learn practical approaches to formal verification in Linux kernel development using Finite-State Machines and tracing events, with insights on low-overhead runtime verification techniques.
Modularity in PVS
Explore modularity concepts in PVS theorem proving, enhancing code organization and reusability for complex formal verification projects.
System Introductions I - HOL - Lecture 1
Introduction to the HOL theorem prover, exploring its features and applications in formal mathematics and computer science verification.
Even More on HOL Light - Lecture 3
Explore advanced topics in HOL Light theorem proving, building on previous sessions to deepen understanding and practical application of this powerful system.