
Teaching Mathematics to Computers - Modern Approaches and Challenges
Explore the potential of computers in theorem-proving and advanced mathematics, from basic logic to modern research, and their future role in mathematical discovery.
Polynomial Functors Formalization Report
Explore the formalization of polynomial functors with Sina Hazratpour, delving into advanced mathematical concepts and their applications in functional programming.
Cueology of Proof
Explore the art and science of constructing mathematical proofs, delving into logical reasoning, problem-solving techniques, and the foundations of formal verification.
Mechanising Gödel-Löb Provability Logic in HOL Light
Explore the mechanisation of Gödel–Löb Provability Logic in HOL Light, delving into formal proofs and theorem verification techniques for modal logic systems.
From 100 to 1000+ Theorems - Advancements in Mathematical Proof Verification
Explore the journey of formalizing mathematics, from initial proofs to extensive theorem libraries, and discover the challenges and progress in this field.
Automated Alignments in Mathematics
Explore automated alignments in mathematics with Thibault Gauthier, focusing on innovative techniques and applications in mathematical research and problem-solving.
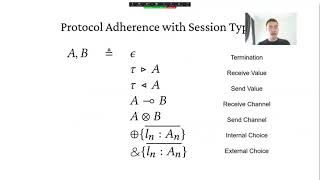
Ferrite: A Rust EDSL for Message-passing Protocol Verification
Explore an embedded domain-specific language in Rust for verifying message-passing protocols, enhancing communication system reliability and correctness.
RustBelt: A Quick Dive Into the Abyss - Formalizing Rust's Safety Story
Explore Rust's safety mechanisms, type system, and semantic interpretations. Dive into lifetime logic, sharing predicates, and Coq implementations of Cell operations.
RustProof: Static Analysis Using MIR - PDXRust October 2016
Explore static analysis in Rust using MIR with PDXRust. Learn about formal verification, Hoare logic, and compiler plugins for enhanced code quality and reliability.
Verifying Indistinguishability of Privacy-Preserving Protocols
Explore a novel approach to verifying privacy-preserving protocols, balancing precision and accessibility. Learn about indistinguishability proofs and their application to TLS and PIR protocols.
Formally Verifying Optimizations with Block Simulations
Explore formal verification of compiler optimizations using block simulations. Learn about enhancing CompCert with efficient, verified validators for advanced optimizations like LCM and SR.
Leakage Models: A Leaky Abstraction in Cryptographic Software Verification
Explore gate-level verification for cryptographic software timing, abandoning leakage models. Discover a novel approach to ensure constant-time execution in hardware implementations.
Scalable Linear Invariant Generation with Farkas' Lemma
Explore scalable linear invariant generation techniques using Farkas' Lemma, improving efficiency and accuracy for affine programs without compromising completeness.
Counterexample Driven Quantifier Instantiations with Applications to Distributed Protocols
Explore a novel interactive verification methodology using relational abstraction to tackle quantifier reasoning challenges in infinite-state systems, with applications to distributed protocols.
Message Chains for Distributed System Verification
Explore an automated bookkeeping method using message chains to simplify verification of asynchronous distributed programs, revealing execution structure and aiding in system-level reasoning.
Cutting the Cake Into Crumbs: Verifying Envy-Free Cake-Cutting Protocols using Bounded Integer Arithmetic
Explore envy-free cake-cutting protocols verification using bounded integer arithmetic. Learn to reduce fairness checks to SAT instances for efficient protocol analysis.
Internalizing Indistinguishability with Dependent Types
Explore a novel type system combining dependency tracking and dependent types, internalizing indistinguishability for enhanced information flow control and program equivalence reasoning.
Mechanizing Refinement Types
Explore the mechanization of refinement types, combining semantic subtyping and parametric polymorphism. Learn about λRF calculus, data propositions, and metatheory proofs in LiquidHaskell and Coq.
In-Order Execution Nails Every Weak Memory Behavior
Explore in-order execution's comprehensive coverage of weak memory behaviors, unveiling its significance in modern computing systems.
Certification of Confluence- and Commutation-Proofs via Parallel Critical Pairs
Explore formalization of parallel critical pairs in Isabelle, simplifying definitions and generalizing criteria for confluence and commutation in term rewrite systems.
Trillium: Higher-Order Concurrent and Distributed Separation Logic for Intensional Refinement
Explore Trillium, a separation logic framework for intensional refinement in concurrent and distributed systems. Learn about strengthening program logics to prove safety and liveness properties.