Formal XAI - Explainable Artificial Intelligence
Explore formal methods for explainable AI with Joao Marques Silva, delving into rigorous approaches for transparent and interpretable machine learning models.
Inductive Invariants for Streamlining Distributed Protocol Proofs
Streamlining distributed protocol proofs using invariant taxonomies. Simplifies finding inductive invariants by categorizing them into Regular and Protocol Invariants, reducing developer effort in proving correctness.
IronSpec - Increasing the Reliability of Formal Specifications
Innovative framework for enhancing formal specification reliability through automated testing, SpecTesting Proofs, and mutation testing. Discovers bugs in real-world verified systems, strengthening software verification.
Automated Transformation of Hierarchies of Theories in Large Libraries
Explore automated transformations of theory hierarchies in extensive libraries, focusing on efficient methods for managing complex mathematical structures.
Tractable Representations for Boolean Functional Synthesis
Explore efficient techniques for synthesizing Boolean functions from relational specifications, focusing on structural properties and normal forms that enable tractable synthesis.
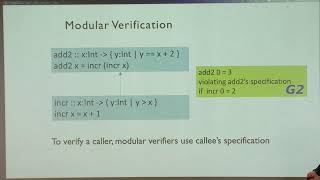
Counterexample-Guided Inference of Modular Specifications
Explore an algorithm for automatically inferring function specifications in modular verification, enhancing compositional proofs and extending completeness to infinite specification sets.
Program Verification for the Linux Kernel - Potential Costs and Benefits
Explore potential costs and benefits of program verification for the Linux kernel, gaining insights into its impact on development and reliability.
Lazy Abstraction Refinement with Proof for an Enhanced Verifier
Explore advanced techniques in software verification using lazy abstraction refinement with proof, enhancing verifier capabilities for improved code analysis.
How to Trust a Verified Program - Challenges and Solutions in Program Verification
Explore challenges in trusting verified programs, examining theoretical and practical issues in program verification using proof assistants, and discussing potential solutions for enhancing trustworthiness.
The 4 Horsemen of Unsoundness in Object-Oriented Languages
Explore 4 subtle issues challenging OO verification: termination, leaky partial verification, ill-founded contracts, and reduction to primitive operations.
Trustworthy Runtime Verification via Bisimulation - Experience Report
Explore trustworthy runtime verification using bisimulation in the Copilot framework. Learn how CopilotVerifier generates correctness proofs for compiled monitors, enhancing safety-critical system assurance.
Trustworthy Formal Natural Language Specifications
Explore a novel approach to translating natural language specifications into formal claims within proof assistants, enhancing software verification and bridging the gap between informal and formal specifications.
Complete Multiparty Session Type Projection with Automata - ST30
Explore efficient multiparty session type projection using automata. Learn sound, complete, and efficient techniques for verifying asynchronous communication protocols.
Martin-Löf Type Theory Mechanization in Coq
Explore an extensive mechanization of Martin-Löf Type Theory in Coq, covering decidability of conversion and type checking, with a certified executable type checker for MLTT.
UTC Time, Formally Verified - Presentation at CPP 2024
Explore formal verification of UTC time conversions using Coq and MathComp, including leap seconds implementation and refinement techniques for software verification projects.
Unified Compositional Symbolic Execution - N40AI'24
Explore unified compositional symbolic execution techniques for program analysis, enhancing software reliability and performance optimization.
Trust but Verify: Scaling Deductive Verification with Abstract Interpretation - N40AI'24
Explore scaling deductive verification for smart contracts using abstract interpretation. Learn about pointer analysis algorithms, program simplifications, and challenges in low-level code analysis.
A Comparison of Program Logics for (In)Correctness
Explore program logics for correctness and incorrectness, comparing over- and under-approximation techniques. Analyze Sufficient Incorrectness Logic and its Separation Logic variant for dynamic heap management.
A Tale of Shared Memory Concurrency in Programming Languages
Explore shared memory concurrency in programming languages, examining challenges, recent advancements, and future directions for designing effective concurrency models for multicore systems.
Facing Uncertainty in AI - From Verification to Synthesis
Explore techniques for verifying and synthesizing AI systems under uncertainty, focusing on model-based approaches and automation to ensure safety and dependability in various AI applications.
Tutorial on Deductive Program Synthesis - Part 2: Hands-on Derivation and Advanced Techniques
Learn deductive program synthesis through hands-on examples, exploring SSL rules, recursion handling, and step-by-step derivation of provably correct pointer-manipulating programs.