Adventures in the Underland - The CQForensic Toolkit as a Unique Weapon Against Hackers
Explore CQTools, a powerful toolkit for penetration testing, featuring unique discoveries by CQURE Team. Learn practical applications in cybersecurity projects and forensic analysis.
Attacking Electric Motors for Fun and Profit
Explore electric motor vulnerabilities and attacks bridging cyber and physical realms. Learn about security risks, attack methods, and protective measures for this critical technology.
Breaking XSS Mitigations Via Script Gadgets
Explore a novel web hacking technique that bypasses XSS mitigations using script gadgets. Learn about HTML sanitizers, CSP, and practical demonstrations of this powerful attack method.
The Power of Data-Oriented Attacks - Bypassing Memory Mitigation Using Data-Only Exploitation Techniques
Explore data-oriented attacks that bypass memory mitigation techniques, focusing on exploiting vulnerabilities without altering control flow. Learn about innovative exploitation methods and their implications for cybersecurity.

Attacking Windows by Windows
Explore a novel method for exploiting Windows kernel vulnerabilities across multiple OS versions, bypassing security measures to gain system privileges.
Use-After-Use-After-Free - Exploit UAF by Generating Your Own
Explore a novel exploitation technique for UAF vulnerabilities in Adobe Flash, transforming them into multi-class type confusions for full memory access despite recent mitigations.
Command Injection in F5 iRules
Explore command injection vulnerabilities in F5 iRules, focusing on syntax, exploitation techniques, and security implications for BigIP F5 products used in high-performance web traffic routing.
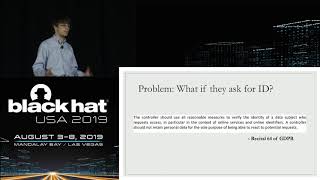
GDPRrrrr - Using Privacy Laws to Steal Identities
Explores how GDPR's Right of Access can be exploited by social engineers to steal sensitive information, highlighting vulnerabilities in data protection laws and offering insights for businesses and legislators.
CQTools - The New Ultimate Hacking Toolkit
Explore top 39 hacking tools in CQTools, including 5 new ones for privilege elevation and network attacks. Learn techniques for hash extraction, impersonation, and decryption.
Open Sesame - Picking Locks with Cortana
Uncover the "Open Sesame" vulnerability in Cortana, allowing attackers to bypass Windows lock screens, execute code, and potentially gain elevated privileges on locked machines.
Adventures in Attacking Wind Farm Control Networks
Explore vulnerabilities in wind farm control networks and potential attack scenarios, with insights on securing these critical renewable energy infrastructures.
Windows Kernel Patch Protection - Achilles Heel - PatchGuard
Explore critical flaws in Windows Kernel Patch Protection, learn attack techniques to disable PatchGuard, and discover proposed mitigations for enhanced system security.
Whom Do You Trust - MSPs and Other Forgotten Risks for SMBs
Explore cybersecurity risks for SMBs, focusing on MSP vulnerabilities and supply chain attacks. Learn strategies to protect against threats and strengthen your security posture.
Exploiting Android Messengers with WebRTC
Explore WebRTC vulnerabilities in Android messaging apps, their exploitation, and mitigation strategies. Learn about security research techniques and mobile application security.
Don't Ruck Us Too Hard - Owning All of Ruckus AP Devices
Explore vulnerabilities in Ruckus AP devices, including pre-authentication remote code execution exploits. Learn about research methods, discovered CVEs, and a framework for cross-architecture analysis.
Bug Bounty - Why Is This Happening
Explore bug bounty programs' challenges and realities from multiple perspectives, offering insights into their evolution, limitations, and potential for improvement in cybersecurity.
Basic Security Analysis on Data and Information
Learn essential digital security techniques for analyzing data and information, focusing on threat identification, communication safety, and practical tools for journalists and civil society groups.
HackIM CTF - Do's and Don'ts
Explore CTF competitions: learn security through challenges in web, crypto, reverse engineering, and more. Gain insights on dos and don'ts for successful participation in HackIM CTF.
How to Interact With Bug Bounty Programs
Learn effective strategies for participating in bug bounty programs, including handling duplicates, prioritizing submissions, and escalating issues. Gain insights into common challenges and best practices.
Injecting Security Into Web Apps With Runtime Patching And Context Learning
Explore advanced web application security techniques using Runtime Application Self Protection (RASP) to prevent code injections and other vulnerabilities through dynamic analysis and patching.
The Art of Bootloader Unlocking - Exploiting Samsung Sboot
Explore Samsung bootloader security, uncovering hidden protocols and vulnerabilities. Learn about anti-tamper mechanisms, memory corruption, and techniques for unlocking Android devices.