How I Break Into Casinos, Airports and CNI - The Basics of Social Engineering
Discover the art of social engineering for ethical hacking. Learn reconnaissance, disguise, pretext creation, and interaction techniques to infiltrate secure facilities while maintaining professionalism and ethics.
When Bandit Strikes - Defend Your Python Code
Discover and defend against common security flaws in Python code using Bandit. Learn customization, CI pipeline integration, and extension techniques for enhanced code security.
Digital Intel Gathering - OSINT for Blue - Red Teams
Explore OSINT techniques for cybersecurity, leveraging social media and public records to enhance threat intelligence and defensive strategies.
Owning the Smart Home with Logitech Harmony Hub
Explore reverse engineering of Logitech's Harmony smart home hub, uncovering vulnerabilities and discussing their implications for device security and potential exploitation.
Breaking VSM by Attacking SecureKernel
Explore vulnerabilities in Windows 10's SecureKernel, potentially compromising Virtualization-Based Security. Learn exploitation techniques and the process of finding and fixing critical security flaws.
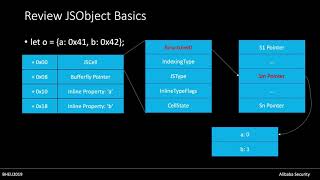
Thinking Outside the JIT Compiler - Understanding and Bypassing StructureID Randomization with Generic and Old-School Methods
Explore generic methods to bypass StructureID Randomization, gaining arbitrary Read/Write ability without relying on JIT compiler-related techniques. Learn innovative approaches to inspire better security mitigations.
Fatal Fury on ESP32 - Time to Release Hardware Exploits
Methodical exploration of defeating ESP32 security features using low-cost hardware techniques, including voltage glitching and analog side-channels, with implications for IoT device security.
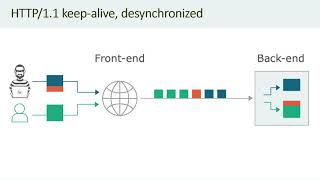
HTTP Desync Attacks - Request Smuggling Reborn
Explore HTTP request smuggling techniques to bypass security, manipulate web infrastructure, and exploit vulnerabilities. Learn detection, confirmation, and exploitation methods for various attack scenarios.
Far Sides of Java Remote Protocols
Explore critical flaws in Java RMI and CORBA protocols, uncovering vulnerabilities in vendor implementations and learning attack techniques for cross-process communications.

Exploiting Qualcomm WLAN and Modem Over The Air
Explore Qualcomm WLAN and Modem vulnerabilities, focusing on firmware exploitation, isolation breaches, and over-the-air control techniques. Gain insights into real-time debugging and mitigation strategies.
Denial of Service as a Service - Asymmetrical Warfare at Its Finest
Explore DDoS attacks, investigative techniques, and asymmetrical warfare in cybersecurity. Learn about real-world incidents, tracking suspects, and the implications of "DDoS as a Service."
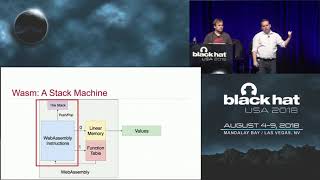
WebAssembly - A New World of Native Exploits on the Browser
Explore WebAssembly's security risks, low-level semantics, and potential vulnerabilities in browser-based applications. Learn about linear memory, function tables, and mitigation strategies.
A New Era of SSRF - Exploiting URL Parser in Trending Programming Languages
Explore a new SSRF exploit technique targeting URL parsers in popular programming languages. Learn about protocol smuggling, fuzzing tools, and discover vulnerabilities in widely-used libraries.
3D Red Pill - A Guest-to-Host Escape on QEMU/KVM Virtio Device
Demonstration of a guest-to-host escape exploit on QEMU/KVM virtio-gpu devices, showcasing vulnerability analysis, exploitation techniques, and potential security solutions.
How I Created My Clone Using AI - Next-Gen Social Engineering
Explore AI-powered impersonation techniques for advanced social engineering attacks, including text, voice, and video cloning. Live demonstrations showcase creating realistic digital doppelgangers for online deception.
HTTP Request Smuggling in 2020 - New Variants, New Defenses and New Challenges
Explore new variants, defenses, and challenges of HTTP Request Smuggling, an attack technique exploiting interpretations of non-standard HTTP requests between client and server.
Stealthily Access Your Android Phones - Bypass the Bluetooth Authentication
Explore Android Bluetooth vulnerabilities, including BlueRepli, and learn stealthy access techniques. Discover security risks in AOSP and mobile manufacturers' oversights.
Web Cache Entanglement - Novel Pathways to Poisoning
Explore novel web cache poisoning techniques, probing cache inconsistencies to build sophisticated exploit chains. Learn to uncover vulnerabilities in caching systems across the internet.
TiYunZong Exploit Chain to Remotely Root Modern Android Devices - Pwn Android Phones from 2015-2020
Comprehensive exploit chain analysis for remotely rooting modern Android devices, focusing on Pixel phones. Explores attack surfaces, introduces new vulnerabilities, and demonstrates practical exploitation techniques.
API-Induced SSRF - How Apple Pay Scattered Vulnerabilities Across the Web
Explore API security vulnerabilities, focusing on Apple Pay's impact, with live demos and actionable strategies for improving defensive programming practices.
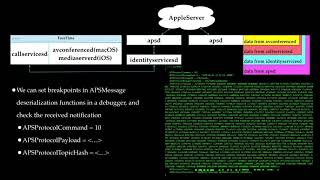
Towards Discovering Remote Code Execution Vulnerabilities in Apple FaceTime
Explore FaceTime's vulnerabilities through reverse engineering, focusing on call initialization, connection processes, and potential attack surfaces for remote code execution.