Bug Hunting on the Dark Side
Explore bug hunting techniques in dark web applications, focusing on real-world examples, cryptography, and common vulnerabilities to enhance your cybersecurity skills.
Client-Side Protection Against DOM-Based XSS Done Right
Comprehensive overview of client-side protection against DOM-based XSS attacks, covering vulnerabilities, prevention techniques, and practical solutions for web security professionals.
Mantra OS - Because the World is Cruel
Explore Mantra OS's penetration testing tools for web application security, including DDoS, SQL injection, and man-in-the-middle attacks. Learn practical methodologies and risk mitigation strategies.
How We Analyzed and Built an Exploit PoC for CVE-2022-24086, a Magento RCE - Catalin Filip - DefCamp - 2022
Explore the analysis and exploit development for CVE-2022-24086, a critical Magento RCE vulnerability, presented by a security researcher at DefCamp 2022.
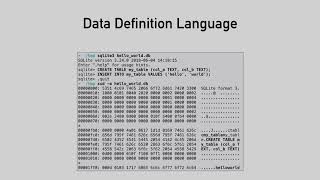
Select Code Execution From Using SQLite
Exploración de vulnerabilidades en SQLite para lograr ejecución de código remoto mediante técnicas innovadoras como Query Hijacking y Query Oriented Programming, demostrando escenarios de ataque en servidores y iOS.
Smart Vacuum Cleaners as Remote Wiretapping Devices - Easterhegg - 2019
Exploración de vulnerabilidades en aspiradoras inteligentes Neato Botvac Connected, incluyendo extracción de firmware y ejecución remota de código, con implicaciones para la privacidad y seguridad del hogar.
The Layman's Guide to Zero-Day Engineering
Demystifying zero-day exploit development: insights into the engineering process, analytical approaches, and misconceptions. Contrasts with CTF challenges and guides aspiring security professionals.
Integrating Mobile Devices into Your Penetration Testing Program - DefCamp 2015
Explore integrating mobile devices into penetration testing programs, covering security risks, attack vectors, and defensive strategies for corporate and personal devices.
PuttyRider - Pivoting from Windows to Linux in a Penetration Test - DefCamp - 2014
Explore pivoting techniques from Windows to Linux in penetration testing using PuttyRider. Learn session hijacking, architecture, and functions through a practical demonstration.
Social Engineering, or "Hacking People" - DefCamp 2014
Explore social engineering tactics and defenses in this talk, covering trust exploitation, corporate espionage, and the human element in cybersecurity. Features insights from Kevin Mitnick.
Why Usual Pentests Suck - DefCamp - 2019
Explore common pentesting pitfalls and innovative approaches to enhance security assessments. Learn strategies to overcome limitations and conduct more effective penetration tests.
Years of IoT Vulnerability Research and Countless 0days - A Retrospective - DefCamp - 2021
Retrospective on IoT vulnerability research, exploring reusable attack vectors, authentication issues, cloud implementations, and command injection in MQTT and RSTP protocols.
What It Takes to Be Good at Bug Bounty Hunting - DefCamp - 2021
Explore bug bounty hunting essentials, methodologies, and community insights. Learn from a passionate expert about getting started, understanding applications, and collaborating effectively in the field.
Next-Gen IoT Botnets - Moar Ownage at DefCamp - 2019
Explore advanced IoT botnet techniques, including hardware hacking, bootloader hijacking, and exploiting vulnerabilities in security cameras and enterprise messaging systems.
Implementing Continuous Offense to Measure and Monitor Cybersecurity Defenses - DefCamp - 2019
Explore continuous offense techniques to assess and enhance cybersecurity defenses. Learn about breach simulation tools, vulnerability assessment, and practical strategies for improving network security.
The U.S. Election System, Can We Fix It? Yes We Can! - DefCamp - 2019
Explore vulnerabilities in U.S. election systems and potential solutions, covering voter registration, voting machines, and result reporting. Learn about security measures and the importance of human factors in election integrity.
Burping Through Your Cryptography Shield - DefCamp - 2018
Explore techniques for bypassing cryptography shields using Burp Suite, with insights on Java extensions and practical problem-solving approaches in information security.
Making Hacking and Social Engineering Harder with Typing Biometrics - DefCamp 2016
Explore typing biometrics as a defense against hacking and social engineering. Learn about continuous authentication, intrusion prevention, and the technology's effectiveness on mobile devices.
How I Hacked My City - DefCamp 2016
Explore urban hacking through a real-world case study of Tel Aviv's open WiFi network, uncovering vulnerabilities and demonstrating practical exploitation techniques.
Split Personalities - The Psychology of Social Engineering - DefCamp - 2016
Explore the psychology behind social engineering, emotional triggers, and human decision-making in cybersecurity. Learn practical insights on phishing techniques and defensive strategies.
Breaking in Bad - I'm the One Who Doesn't Knock - DefCamp - 2015
Exploración práctica de técnicas de hacking y seguridad informática, destacando vulnerabilidades comunes y la importancia de la concienciación en ciberseguridad.