How I Learnt Hacking in High School
Discover a young hacker's journey, exploring vulnerable platforms, wargames, and online challenges. Learn practical tips and guidelines for aspiring cybersecurity enthusiasts.
Aviation Security 101
Explore aviation security vulnerabilities through pen testing research, covering access risks, performance calculations, maintenance mode issues, and potential misunderstandings in the industry.
CAN Bus Basics With Hands On Fuzzing
Explore CAN bus fundamentals and hands-on fuzzing techniques for automotive systems, covering ECUs, attack surfaces, and practical demonstrations using various tools and setups.
Dial V for Vulnerable - Attacking VoIP Phones
Explore VoIP phone vulnerabilities, attack methods, and security recommendations. Learn firmware access, emulation approaches, and exploit development for various VoIP devices.
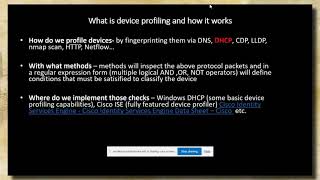
Bypassing Advanced Device Profiling with DHCP Packet Manipulation
Explore advanced device profiling bypass techniques using DHCP packet manipulation for Network Access Control systems. Learn about implementation, mechanics, and risk mitigation strategies.

Repo Jacking - How Github Usernames Expose Projects to RCE
Explore 'repo jacking', a widespread supply chain vulnerability affecting 70,000+ open-source projects. Learn its causes, exploitation methods, and mitigation strategies to protect your GitHub-dependent projects.
Ethical Internet Scanning in 2022
Explore ethical approaches to internet-wide scanning, including best practices, vulnerability assessment, and measuring risk exposure in the digital landscape.
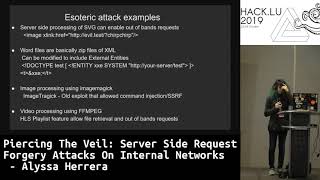
Piercing the Veil - Server Side Request Forgery Attacks on Internal Networks
Explore esoteric SSRF entry points, internal service vulnerabilities, and mitigation strategies in ethical hacking and bug bounty programs.
Take Your Path Normalization Off and Pop 0days Out
Explore path normalization vulnerabilities in web frameworks, including real-world examples and case studies of critical security flaws leading to remote code execution and access control bypass.
Make ARM Shellcode Great Again
Explore ARM shellcode techniques, from basic execve() to advanced "Quantum Leap" code, covering tight spaces, mprotect egghunters, and ARM-Thumb switching for efficient exploitation.
What The Fax?
Explore the security vulnerabilities of fax technology, including debugging challenges, attack vectors, and mitigation strategies in this comprehensive analysis.
Exploits in Wetware
Exploits in wetware: social engineering techniques, OSINT strategies, and defensive measures against human vulnerabilities in cybersecurity, based on real-world experiences.
From EK to DEK - An Analysis of Modern Document Exploit Kits
Explore modern document exploit kits, their infection chains, and techniques. Gain insights into ThreadKit, VenomKit, and various exploitation methods used in malicious documents.
Security Awareness Training Refresh
Refresh your security awareness with practical tips on password management, phishing prevention, and role-based training. Learn to engage users effectively and create impactful, tailored security programs.
Red Teaming a Manufacturing Network - Without Crashing It
Explore techniques for safely red teaming manufacturing networks, including reconnaissance, passive methods, and potential attack vectors, while learning mitigation strategies and best practices.
Introduction to Reversing and Pwning
Explore reverse engineering and exploitation techniques, covering low-level programming, memory vulnerabilities, and essential tools for cybersecurity enthusiasts and professionals.
Federated Login CSRF
Explore federated login CSRF vulnerabilities in OpenID Connect and OAuth 2.0, examining attack scenarios, risks, and mitigation strategies for secure identity linking in web applications.
Building Secure ASP.NET Core MVC Applications
Explore ASP.NET Core MVC security features, including XSS and CSRF protection. Learn to build robust web applications with modular architecture and cross-platform compatibility.
Differences Between Web Application Scanning Tools When Scanning for XSS and SQLi
Investigates differences between web application scanning tools for XSS and SQLi, addressing challenges in modern web architectures and suggesting improvements for effective vulnerability detection.
Bug Bounty Programs - Successfully Controlling Complexity and Perpetual Temptation
Explore bug bounty programs with industry experts, covering implementation strategies, legal considerations, and best practices for effective vulnerability management and researcher collaboration.
Pushing Left Like A Boss - Application Security Foundations
Discover application security foundations and learn to 'push left' in the software development lifecycle. Explore strategies from vulnerability scanning to red team exercises for a proactive approach to security.