How to Win Over Security Teams and Gain Influence as a Hacker
Insights from experienced hackers on effective strategies, tools, and etiquette for successful bug bounty hunting and building positive relationships with security teams.

An Invitation to Hack - Benefits and Risks of Vulnerability Disclosure Programs
Explore vulnerability disclosure programs' benefits and risks, legal considerations, and real-world examples. Learn practical insights for implementing these programs to enhance cybersecurity in organizations.
Advanced Hacking Workshop - Techniques and Personal Insights
Top hackers share advanced techniques, personal stories, and insights on bug bounty hunting. Learn from experts Frans Rosén and Peter Yaworski about URL validation, third-party scripts, and building a hacking career.
Hacker101 - Android Quickstart
Learn essential Android app hacking concepts, tools, and techniques in this quick guide. Explore APK structure, emulators, decompilation, and security testing methods for successful mobile app penetration testing.
Maximizing Burp
Enhance vulnerability detection skills using Burp Suite's advanced features like Intruder and Scanner for more effective penetration testing.
The Hacker Army: Protecting Your Data Through Bug Bounty Programs
Explore how ethical hackers form a global freelance security team, supporting internal teams through bug bounty programs and keeping us safer online in the face of cybersecurity challenges.
Tapping Hackers for Continuous Security
Explore how external hackers can enhance security, assess the suitability of bug bounty programs, and learn to build effective vulnerability disclosure programs for improved software development.
Unique Mindset - Hacking Techniques and Favorite Findings
Explore zseano's unique hacking mindset through real-world examples, favorite findings, and insights on identifying critical vulnerabilities in web applications.
Hardware Hacking for the Masses
Explore hardware hacking fundamentals, fields, and affordable entry points. Learn about electronics, UART, JTAG, and car hacking with practical tips and resources for beginners.
GitHub Recon and Sensitive Data Exposure
Learn techniques to locate and identify sensitive data exposed in GitHub repositories, enhancing your cybersecurity skills for ethical hacking and vulnerability assessment.
Bugcrowd University - Advanced Burp Suite
Explore advanced Burp Suite configurations, functionality, and extensions to enhance your web application security testing capabilities and efficiency.
Recon & Discovery
Explore techniques for discovering company assets, including subdomain enumeration, fingerprinting, dorking, and content discovery, to enhance your bug bounty skills.
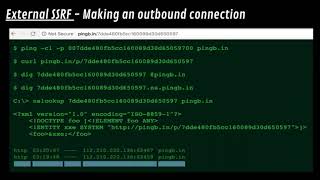
Server Side Request Forgery
Learn to identify, exploit, and mitigate Server-Side Request Forgery vulnerabilities. Covers external and internal SSRF, bypassing blacklists, and includes practical demonstrations and real-world examples.
Car Hacking: A College Student's Perspective - LevelUp 0x04
Explore car hacking techniques, tools, and targets from a student's perspective. Learn about initial access, hardware hacking, and canvas basics for automotive security.
Hacking in Groups: Best Practices for Team Collaboration - LevelUp 0x04
Discover strategies for effective team hacking: finding skilled colleagues, identifying potential teammates, best practices for collaboration, and tools to maximize teamwork efficiency.
LevelUp 0x04 - Blueprint for Becoming a Penetration Tester
Blueprint for aspiring pen testers: expert insights, career tips, and actionable steps to enter the field of ethical hacking and penetration testing.
Bug Hunting as a Team: Challenges and Insights - LevelUp 0x04
Insights on collaborative bug hunting: organizing teams, sharing information, splitting bounties, and overcoming challenges in the evolving field of cybersecurity.
Group Hacking: A Mini Live-Hacking Event - Discovering Internet-Wide Vulnerabilities
Discover how a small team uncovered a widespread vulnerability across multiple bug bounty programs. Learn strategies for effective group hacking, testing, and reporting in cybersecurity.
LevelUp 0x04 - The Infinite Game of Hacking and Future of Crowdsourced Security
Explore the 'infinite game' of hacking and the future of crowdsourced security with Bugcrowd's CEO Ashish Gupta in this insightful welcome address for LevelUp 0x04.
LevelUp 0x04: Advanced Bug Bounty Techniques - Day 2
Explore advanced bug bounty techniques and strategies with industry experts in this comprehensive cybersecurity event focused on enhancing hacking skills and knowledge.
LevelUp 0x04 - Introduction to Ethical Hacking and Bug Bounty - Day 1
Explore cutting-edge cybersecurity insights and strategies at this free conference, featuring expert talks and discussions on the latest industry trends and challenges.