
Hacking Smartphones with QR Codes
Explore smartphone vulnerabilities through QR codes, learning to embed Wi-Fi backdoors, track targets, and hijack data connections. Gain insights into hidden networks, tracking techniques, and rogue access points.

Flashing Tools to the ESP8266 with Only a Browser
Learn to upload hacking projects to ESP8266 microcontrollers using only a browser, making it easy for beginners to load binaries onto devices like the WiFi Nugget without command-line knowledge.
Live with Alex Stamos - Security Approaches at Facebook
Explore Facebook's comprehensive approach to security, from bug bounties to combating misinformation, with insights from Chief Security Officer Alex Stamos on protecting global communities.
Return to the Zombie Gadgets - Undermining Destructive Code Reads via Code-Inference Attacks
Explores techniques to bypass destructive code reads, a defensive strategy against code reuse attacks, through constructive reloads and code association via implicit reads, demonstrating vulnerabilities in this security approach.
Evaluation of the Executional Power in Windows Using Return Oriented Programming
Explore Windows vulnerabilities through Return Oriented Programming, evaluating execution power and discussing implications for system security in this IEEE workshop presentation.
Heap Models for Exploit Systems
Formal modeling of heap exploits as abstract machines, exploring physical and logical heap properties to express attacks as reachability problems in specific heap configurations.
Unambiguous Encapsulation
Explore error-correcting codes for secure data encapsulation, offering resilience against errors and buffer overflows. Learn about code classes, implementation, and future applications in communication technologies.
Missing the Point(er) - On the Effectiveness of Code Pointer Integrity
Explores effectiveness of Code Pointer Integrity (CPI) in preventing memory corruption attacks. Demonstrates vulnerabilities in CPI implementations relying on information hiding, highlighting importance of robust secret protection in security mechanisms.
Unleashing Mayhem on Binary Code
Explore automated exploit generation for binary programs using hybrid symbolic execution and index-based memory modeling. Learn techniques to find and demonstrate exploitable vulnerabilities efficiently.
Analyzing Ground-Truth Data of Mobile Gambling Scam
Explore mobile gambling scam tactics, data analysis, and infrastructure, uncovering social engineering tricks, app delivery methods, and payment channels used by cybercriminals.
Docker for Pentesting & Bug Bounty Hunting
Explore Docker's potential for pentesting and bug bounty hunting. Learn to set up Kali Linux, OWASP Juice Shop, and Bug Bounty Toolkit, enhancing your cybersecurity skills and workflow efficiency.
Docker for Pentesting and Bug Bounty Hunting
Learn to leverage Docker for pentesting and bug bounty hunting. Set up Kali Linux, OWASP Juice Shop, and Bug Bounty Toolkit containers. Explore advantages and practical applications of containerization in cybersecurity.
Cybersecurity Career Paths: CEH vs CISSP, Degrees, and CTFs vs Penetration Tests
Informative discussion on CEH vs CISSP certifications, cybersecurity degrees, and differences between CTFs and penetration tests, offering insights for aspiring infosec professionals.

DNS Enumeration Tutorial - Dig, Nslookup & Host
Learn DNS enumeration techniques using Dig, Nslookup, and Host tools for effective reconnaissance and troubleshooting in network security and administration.
KRACK Attack Proof of Concept on Android and Linux Devices
Demonstration of KRACK Attack Proof of Concept on Android/Linux devices, including installation, configuration, and testing steps for this Wi-Fi security vulnerability.
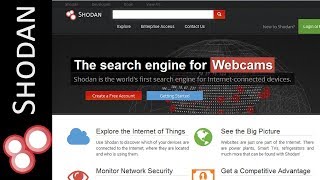
Shodan Search Engine Tutorial - Access Routers, Servers, Webcams + Install CLI
Explore Shodan's capabilities to find internet-connected devices, from webcams to routers. Learn search techniques, filters, and CLI installation for enhanced cybersecurity awareness.
Learn Offensive JavaScript Today
Discover offensive JavaScript techniques including keylogging, data exfiltration, password theft, and CSRF bypass in this concise tutorial on exploiting web vulnerabilities.
Hacking for Fun and Profit - Motivations and Rewards
Explore the motivations behind hacking and its potential for both enjoyment and financial gain with HackerOne CEO Mårten Mickos at Disobey 2017.
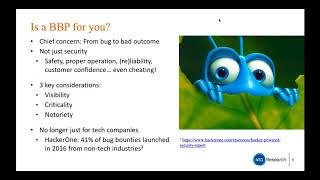
Bug Bounties and the Path to Secure Software Development
Explore bug bounties and vulnerability disclosure policies for secure software development, including implementation strategies, benefits, and best practices.
HackerOne Product Walkthrough - Security Team and Researcher Perspectives
Explore HackerOne's platform from both security team and researcher perspectives, covering report management, rewards, and key features for effective vulnerability disclosure.
Bug Bounty Product Demo - HackerOne Platform Overview
Explore HackerOne's platform for managing security vulnerabilities, leveraging ethical hackers, and enhancing penetration testing with co-founder Michiel Prins.