Colorful Like a Chameleon - Security Nightmares of Embedded Systems
Explore security vulnerabilities in embedded systems, focusing on real-world examples and practical attack scenarios. Learn about potential risks and strategies for enhancing embedded system security.
Bypassing Secure Boot Using Fault Injection
Explore fault injection techniques to bypass Secure Boot in embedded systems, focusing on hardware-based attacks when logical vulnerabilities are absent.
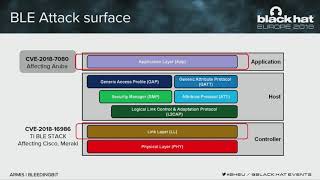
BLEEDINGBIT - Your APs Belong to Us
Explore zero-day vulnerabilities in BLE chips, allowing unauthenticated network penetration. Learn about BLEEDINGBIT, its impact on enterprise APs, and potential attack scenarios.
Apple Neural Engine Internal - From ML Algorithm to HW Registers
Explore the inner workings of Apple's Neural Engine, from machine learning algorithms to hardware registers, with insights into FaceID's neural network and SEP firmware security.
EFIxplorer - Hunting for UEFI Firmware Vulnerabilities at Scale with Automated Static Analysis
Discover automated static analysis techniques for identifying UEFI firmware vulnerabilities at scale, addressing the lack of systemic approaches in x86-based systems research.

Secure Boot Under Attack - Simulation to Enhance Fault Attacks & Defenses
Explore fault injection attacks on Secure Boot, their impact on embedded systems, and strategies for enhancing defenses through simulation techniques.
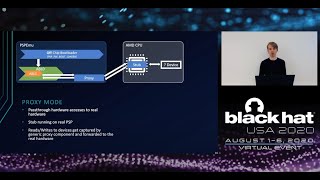
All You Ever Wanted to Know about the AMD Platform Security Processor and Were Afraid to Emulate - Inside a Deeply Embedded Security Processor
Explore AMD's Platform Security Processor: its role in system bootstrapping, security features, and proprietary nature. Gain insights into this embedded ARM core within x86 CPUs.
Black-Box Laser Fault Injection on a Secure Memory
Explore vulnerability research on the Microchip ATECC508A secure memory, examining laser fault injection techniques to bypass cryptographic authentication in IoT devices.
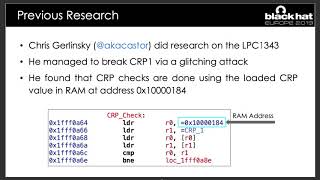
Breaking Bootloaders on the Cheap
Reverse-engineering bootloaders of popular microcontrollers to assess vulnerabilities in readout protection, focusing on software-based attacks and critical flaws in specific chip families.
OEM Finder - Hunting Vulnerable OEM IoT Devices at Scale
Discover a tool for identifying vulnerable OEM IoT devices across thousands of images, revealing security risks in both supplier and vendor firmware distributions.
Backdooring Hardware Devices by Injecting Malicious Payloads on Microcontrollers
Explore techniques for injecting malicious payloads into microcontrollers, from basic to advanced methods, to create hardware backdoors. Learn about firmware entry points and payload execution.
Beyond Root - Custom Firmware for Embedded Mobile Chipsets
Explore reverse engineering techniques to bypass protections and expand functionality of embedded mobile chipsets, going beyond traditional rooting methods for complete device control.
Attacking VxWorks - From Stone Age to Interstellar
Explore vulnerabilities in VxWorks, a real-time operating system, from historical exploits to cutting-edge attack techniques. Gain insights into securing critical infrastructure and embedded systems.
Forging the USB Armory
Explore the development of the USB armory, an open-source hardware device for security applications. Learn about its architecture, security features, and potential uses as a trusted USB device.
Hackers in the Wire and Drones Oh My!
Explore powerful, inexpensive penetration testing using ARM-based devices, from wired/wireless dropboxes to flying drones. Control actions remotely, with devices like BeagleBone Black and Raspberry Pi 2.
Pwning the Nerf Gun
Reversing and hijacking a remote-controlled Nerf tank gun through hardware, firmware, and RF analysis. Includes live demonstration of taking control and potentially shooting the conference organizer.
Checking BIOS Protections Offline With Just the Firmware Updates
Explore system firmware vulnerabilities and their impact on security. Learn about offline analysis of UEFI firmware updates to identify protection gaps and potential risks in modern systems.
Lessons Learned Hunting IoT Malware
Explore IoT malware hunting techniques, honeypot designs, and real-world case studies. Learn reverse-engineering strategies for embedded systems and gain insights into next-generation threat detection.
Holy Smokes, How to Vape Yourself to Root
Explore how e-cigarettes can be transformed into covert exploit platforms, including firmware decryption, custom functionality, and system penetration techniques.
How the BIOS Assures Its Handling of Inputs
Explore BIOS input handling, firmware interfaces, and analysis techniques for formal validation and vulnerability detection, including static, dynamic, and symbolic execution approaches.
Mind the Gap - Studying the Insecurity of Provably Secure Embedded Trusted Execution Architectures
Explore vulnerabilities in embedded trusted execution architectures and learn about potential security gaps in provably secure systems.