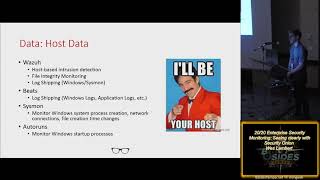
Enterprise Security Monitoring - Seeing Clearly with Security Onion - Wes Lambert
Learn to implement enterprise-level security monitoring using Security Onion, covering tools, data types, interfaces, and deployment strategies for effective threat detection and analysis.
Operating Elasticsearch with Ease at Scale
Discover strategies for operating Elasticsearch at scale, covering common issues, optimization techniques, and best practices for handling massive deployments with billions of ingests and millions of searches daily.
Got Popcorn? What's on the Vuln Channel Tonight?
Explore a platform for automated code scanning and vulnerability data streaming, designed to provide developers with fast, timely information on potential security issues.
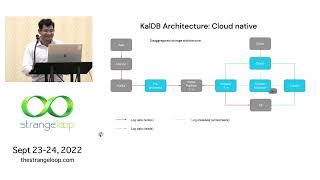
KalDB - A Cloud Native Log Search Platform
Explore KalDB, a cloud-native log search platform addressing Elasticsearch limitations. Learn about its architecture, real-time visibility, automatic field conflict handling, and cost-saving techniques.
ELK Stack for Hackers
Explore ELK stack's potential for hackers: learn to leverage Elasticsearch, Logstash, and Kibana for efficient log analysis, data visualization, and enhanced security insights.
Real Time Data Pipelines
Explore real-time data pipelines for managing massive analytics streams from millions of devices, covering collection, routing, storage, and analysis techniques at high data rates.
Centralized Logging Patterns
Explore centralized logging patterns for organizations with multiple servers or containers. Learn advantages and disadvantages of various approaches, including parsing, sending, structuring, containerizing, and orchestrating logs.
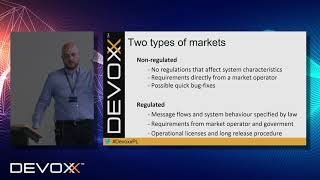
Harnessing Complex Event Processing for Fraud Detection
Explore complex event processing for fraud detection in gambling systems, covering technological evolution and specific use cases in this niche domain.

Live Kubernetes Debugging with the Elastic Stack
Hands-on guide to troubleshooting Kubernetes apps using Elastic Stack, covering health checks, monitoring, tracing, logs, and deployment analysis for efficient problem-solving.
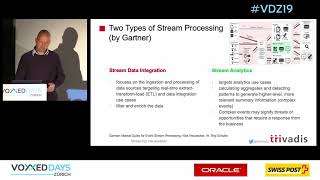
Streaming Visualisation
Explore streaming data visualization techniques, from traditional approaches to dedicated solutions. Learn architecture blueprints and tools for real-time data analysis and presentation.
Elasticsearch + Hibernate - From Artisanal to Industrial Integration
Discover how Hibernate ORM and Elasticsearch can be seamlessly integrated, enabling automatic data synchronization and efficient querying between relational databases and search indexes.
And the Beats Go On
Explore new data shippers for Elasticsearch: Packetbeat for network packets, Metricbeat for machine metrics, and Filebeat for log files. Learn to build custom beats with Libbeat.
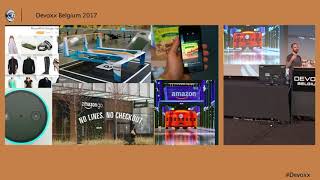
Building Serverless AI Powered Applications on AWS
Explore serverless AI applications on AWS using Amazon Rekognition and Polly. Build image analysis and podcast generation systems with practical demos and deployment techniques.
Elasticsearch and Hibernate
Discover how Hibernate ORM and Elasticsearch can be seamlessly integrated for efficient data synchronization, automatic indexing, and powerful querying capabilities in Java applications.
Tracing Performance of Your Service Calls with Some Help of Sleuth, Zipkin & ELK
Explore how to enhance service performance tracing using Sleuth, Zipkin, and ELK stack. Learn to set up Sleuth in Spring Boot services, utilize Zipkin for identifying bottlenecks, and improve logging monitoring for better insights.
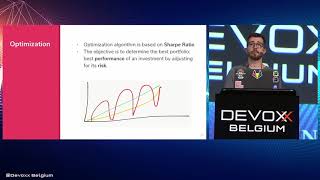
Cryptocurrency, Data Mining and Machine Learning - Winning Combo?
Explore optimizing cryptocurrency portfolios using ElasticSearch, Facebook's Prophet, and custom Python data mining for long-term investment strategies.
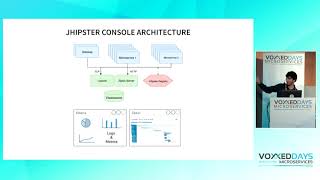
Monitoring a JHipster Microservice Architecture in Practice
Explore efficient microservice monitoring with JHipster Console. Learn to leverage logs, metrics, and traces for improved debugging and scaling in production systems.
Advanced Search for Your Legacy Application
Learn to integrate Elasticsearch into legacy applications, enabling advanced search features without complex SQL. Includes live coding demo, data operations, and performance optimization techniques.
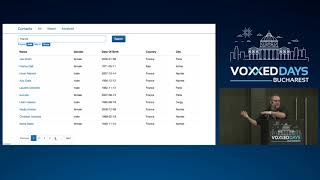
Advanced Search for Your Legacy Application
Enhance legacy applications with Elasticsearch for powerful search capabilities without complex SQL coding. Live demonstration of integration and advanced features.
Application Logging and Logstash
Explore effective application logging strategies, from basics to advanced techniques using Logstash and Kibana. Learn to plan, implement, and leverage logs for debugging and monitoring complex web applications.

Using ELSA for Fun & Profit
Explore advanced ELSA features for security analysis, including Elasticsearch integration, improved syslog-ng, containerization, and new visualization tools like Ankey and geo mapping.