DevOps Tutorial for Beginners in Hindi
Great Learning brings you this 10-hour long tutorial on DevOps for Beginners in Hindi to take you from the starting point through the finishing point of everything you need to know about DevOps and getting started on the journey to master it.
DevOps Tutorial - Full Course
This video teaches DevOps and its key functions and concepts by carrying out simultaneous demonstrations and examples to help you get started on the right foot.
Elasticsearch Tutorial for Beginners
Comprehensive guide to Elasticsearch fundamentals, covering installation, APIs, queries, indexing, and integration with Kibana for beginners in the ELK stack ecosystem.
Learn Elasticsearch
Comprehensive tutorials on Elastic Stack components, covering installation, configuration, and advanced features for efficient log management and monitoring.
Elasticsearch
Learn to set up and configure ELK stack on GCP, including security, monitoring, and analytics features for comprehensive log management and system insights.
Elasticsearch in Depth Tutorial
Comprehensive tutorial on Elasticsearch queries, covering Search Box, Query DSL, autocomplete, and integration with Kibana. Includes installation guide and version 7.0 updates.
Descubriendo Tesoros Ocultos en el Mundo Java - Ekoparty 2023
Explora técnicas avanzadas de reconocimiento, detección y explotación de vulnerabilidades en Java, incluyendo una herramienta integral para automatizar procesos y mejorar la seguridad.
Apache Log Visualization with Elasticsearch and ELK Stack
Learn to visualize Apache logs using Elasticsearch and ELK Stack on Ubuntu. Set up Elastic Stack, configure components, and create visualizations for effective log analysis and monitoring.
Web Application Honeypot Threat Intelligence - Techniques and Implementation
Explore web application honeypots for threat intelligence, using ModSecurity and OWASP Core Rule Set to capture attacker activity and protect software against emerging threats.
Novibet's Journey to the Cloud - Migration Challenges and Solutions
Explore Novibet's 3-year cloud migration journey, from data center to Azure, addressing challenges and implementing tools for automation, CI/CD, and observability.
Enhancing Observability in Cloud-Based Educational Linux Lab Environment
Explore eBPF-based solutions for enhancing observability in cloud-based Linux lab environments, focusing on real-time resource monitoring and user behavior insights with minimal performance impact.
Network Monitoring via SSH and ELK
Netzwerküberwachung ohne SNMP: Verwendung von SSH, Python und ELK Stack für effektives Monitoring. Praxisnahe Einblicke in alternative Methoden zur Datenerfassung und -analyse von Netzwerkhardware.
Using Blue Team Techniques in Red Team Ops
Innovative techniques for advanced red team operations, including infrastructure management, blue team detection, and dynamic adjustments to enhance effectiveness and evasion.
Getting Better with Data
Learn data-driven strategies to streamline network monitoring, reduce alert fatigue, and optimize your time. Discover tools and processes for effective business intelligence and dashboard creation.
My Bro The ELK - Obtaining Context From Security Events
Automate security event analysis using ELK, Bro IDS, and threat intelligence feeds. Learn to integrate frameworks for faster incident response and enhanced threat detection.
Got Popcorn? What's on the Vuln Channel Tonight?
Explore a platform for automated code scanning and vulnerability data streaming, designed to provide developers with fast, timely information on potential security issues.
Tracing Performance of Your Service Calls with Some Help of Sleuth, Zipkin & ELK
Explore how to enhance service performance tracing using Sleuth, Zipkin, and ELK stack. Learn to set up Sleuth in Spring Boot services, utilize Zipkin for identifying bottlenecks, and improve logging monitoring for better insights.
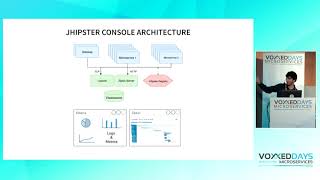
Monitoring a JHipster Microservice Architecture in Practice
Explore efficient microservice monitoring with JHipster Console. Learn to leverage logs, metrics, and traces for improved debugging and scaling in production systems.
Contextual Threat Intelligence - Building a Data Science Capability into the Hunt Team
Learn to build a data science capability into your threat hunting team, enhancing intelligence gathering and analysis for improved cybersecurity operations and threat detection.
Awesome Tools to Level Up Your Spring Cloud Architecture
Explore tools for enhancing Spring Cloud architecture, including documentation, operations, and testing solutions. Learn about visualization dashboards and strategies for managing microservices in production environments.
Log All the Things!
Discover how to collect, clean, store, and analyze log data from various systems using the ELK stack, enhancing DevOps practices and gaining valuable insights into your infrastructure.