Microservices and Enterprise Application Development with Java and Spring Boot
Develop enterprise applications using microservices architecture with Java and Spring Boot. Learn key concepts, tools, and best practices for building scalable and efficient systems.
Elasticsearch 7 for Beginners
Learn Elasticsearch basics, including installation, indexing, searching, and aggregations. Covers core concepts and practical operations for beginners.

Elastic Stack Tutorial - Elasticsearch, Logstash, and Kibana
Learn to install, configure, and utilize the Elastic Stack (ELK) for powerful data analysis and visualization. Master Elasticsearch, Logstash, and Kibana through hands-on tutorials and practical examples.
Learn Elasticsearch
Comprehensive tutorials on Elastic Stack components, covering installation, configuration, and advanced features for efficient log management and monitoring.
Elasticsearch
Learn Elasticsearch basics, setup, architecture, and usage with hands-on tutorials covering installation, indexing, searching, and integration with Kibana and Logstash.
ELK Tutorial in Hindi - Elastic Stack Tutorial
In this tutorial, we have covered all the important topics such as, What is ELK Stack, ELK Architecture, Types of Monitoring, and much more that will help you to understand this concept with ease.
Apache Log Visualization with Elasticsearch and ELK Stack
Learn to visualize Apache logs using Elasticsearch and ELK Stack on Ubuntu. Set up Elastic Stack, configure components, and create visualizations for effective log analysis and monitoring.
Network Flow Monitoring in Kubernetes with Contiv/VPP CNI and Elastic Stack
Explore powerful network flow monitoring in Kubernetes using Contiv/VPP CNI and Elastic Stack for real-time visibility, debugging, bottleneck identification, and security incident investigation.
ELK Stack for Hackers
Explore ELK stack's potential for hackers: learn to leverage Elasticsearch, Logstash, and Kibana for efficient log analysis, data visualization, and enhanced security insights.
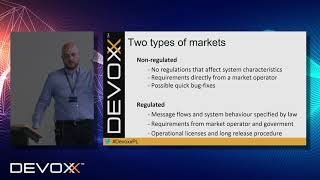
Harnessing Complex Event Processing for Fraud Detection
Explore complex event processing for fraud detection in gambling systems, covering technological evolution and specific use cases in this niche domain.
Application Logging and Logstash
Explore effective application logging strategies, from basics to advanced techniques using Logstash and Kibana. Learn to plan, implement, and leverage logs for debugging and monitoring complex web applications.
Make Sense of Your Logs - From Zero to Hero in Less Than an Hour
Discover how to effectively analyze and make sense of big data using Elasticsearch, Logstash, and Kibana in this insightful presentation on distributed log analysis techniques.
Shield Your Cluster - Security and Elasticsearch
Comprehensive guide to securing Elasticsearch clusters, covering authentication, access control, and integration. Explores various security measures and their implementation in ELK environments.
Proactive Application Security - Karthik Rangarajan
Explore proactive application security strategies, including bug fixing, developer collaboration, code review, centralized logging, and automated access control for enhanced software protection.

Monitoring Infrastructure Using the Elastic Stack
Learn to build a robust monitoring infrastructure using Elastic Stack. Explore Beats, Logstash, Elasticsearch, and Kibana for efficient log and metric analysis in IoT and microservices environments.
Behind the Scenes of an ELK System
Explore the intricacies of managing large-scale log and metric data using ELK stack. Learn from real-world experiences to build resilient, high-availability systems for processing billions of logs daily.
Log Everything with Logstash and Elasticsearch
Centralized logging for multi-server Python apps using Logstash and Elasticsearch. Learn structured logging patterns, GELF transport, and Kibana for analysis and visualization.
Log All the Things!
Discover how to collect, clean, store, and analyze log data from various systems using the ELK stack, enhancing DevOps practices and gaining valuable insights into your infrastructure.