DarkComet From Defense To Offense - Identify Your Attacker
Explore DarkComet's vulnerability to gain insights into attacker campaigns, extract valuable information, and potentially identify the attacker's personal details and infrastructure.
DFIR - Don't Forget Your Roots
Explore essential DFIR skills, from understanding applications and APIs to analyzing C2 beacons, with insights from an experienced practitioner's career journey.
Breaking Full Disk Encryption
Breaking Full Disk Encryption: Explore techniques to bypass custom FDE setups remotely, enhancing forensic analysis capabilities for compromised systems with proprietary encryption.
Car Hacking Virtual Lab
Explore vehicle architecture, CANbus protocol, CAN frames, and car hacking tools in this hands-on virtual lab. Learn from experts in automotive security and gain practical skills in vehicle system penetration testing.
Offensive Memory Forensics
Explore offensive memory forensics techniques and strategies for uncovering hidden threats in digital systems with expert insights from Hugo Teso.
Anti-Forensics - Reverse Engineering a Leading Phone Forensic Tool
Explore vulnerabilities in Cellebrite UFED through reverse engineering, uncovering potential impacts on court cases and discussing the ethical implications of forensic software flaws.
Detecting -Un-Intentionally Hidden Injected Code by Examining Page Table Entries
Explore techniques for detecting hidden injected code through page table entry analysis, covering both intentional malware concealment and unintentional OS paging mechanisms.
Old Dog, New Tricks - Forensics With PowerShell
Explore PowerForensics: a PowerShell-based toolset for live digital forensics and incident response, enabling efficient investigation of advanced cyber threats without system imaging.
Old Dog, New Tricks - Forensics With PowerShell
Explore PowerForensics for live digital investigations using PowerShell. Learn techniques for incident response, threat detection, and forensic analysis without imaging drives.
Analyzing Malicious Office Documents
Learn techniques to analyze malicious Microsoft Office documents using Python tools like oledump and YARA rules. Hands-on exercises guide you through step-by-step analysis without requiring Office software.
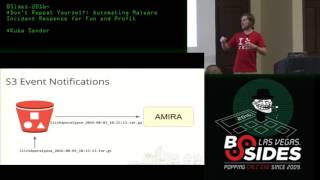
Don't Repeat Yourself - Automating Malware Incident Response for Fun and Profit
Learn to automate malware incident response, saving time and improving efficiency. Explore tools like OSX Collector and ISAC Selector for streamlined digital forensics and analysis.
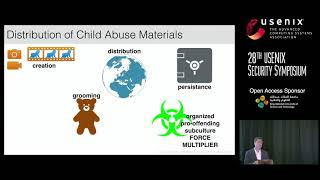
Shining Light on Internet-based Crimes Against Children
Explores Internet-based child exploitation crimes, their long-term impact on victims, and forensic tools for proactive rescue. Discusses privacy technology's role in both protection and potential misuse.
Darwinism vs Forensics
Explore digital forensics in business, covering technologies analyzed, case studies, and anti-forensics efforts. Learn about metadata, EXIF data, and real-world applications in employment and legal matters.
Technical A02 - The Current State of Memory Forensics
Explore memory forensics techniques, acquisition methods, and analysis goals. Learn about Windows 10 memory compression and Virtual Secure Mode impacts on forensic investigations.
Exploring the Wonders of Timesketch and Jupyter
Harness the power of notebooks and Timesketch to solve forensic challenges. Learn data analysis, visualization, and API integration for effective digital investigations.
Volatility 3 Public Beta - The Insider’s Preview
Insider preview of Volatility 3, highlighting new features, architecture, and community contributions for advanced memory forensics. Addresses evolving OS challenges and analyst workflows.
Tools for Cloud Examination
Explore open-source tools for cloud forensics across multiple environments. Learn to handle complexities in cloud acquisition and investigation for effective digital forensics in modern infrastructures.
Happy Holidays from Renzik - What Happened in Autopsy This Past Year
Explore Autopsy's latest features: portable cases, device correlations, enhanced triage, web browser support, OCR, machine translation, and live Windows data collection for digital forensics.
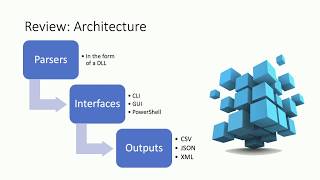
KAPE + EZ Tools and Beyond
Explore latest open-source forensic tools for event logs and NTFS files, including KAPE for efficient data collection and processing. Learn to extend KAPE's capabilities for customized investigations.
Leveraging Vagrant to Quickly Deploy Forensics Environments
Learn to rapidly deploy forensics environments using Vagrant, enhancing efficiency in digital investigations and incident response.
Violent Ruby - A Talk for Hackers, Forensic Analysts, Penetration Testers, and Security
Explore Ruby programming for hacking, forensics, and security testing. Learn techniques for penetration testing and digital forensics using Ruby's powerful capabilities.