How Do I Detect Technique X in Windows - Applied Methodology to Definitively Answer This Question
Learn a systematic approach to detect specific techniques in Windows, enhancing your ability to identify and analyze potential security threats and vulnerabilities.
Forensicating Windows Artifacts - Investigation Without Event Logs
Discover essential Windows artifacts for forensic investigations without event logs. Learn to leverage prefetch files, registry keys, and browser data for effective incident response.
Hacking and Forensics on the Go
Explore mobile hacking and forensics techniques using BeagleBoard. Learn platform selection, OS building, compilation methods, and hardware accessories for on-the-go security operations.
Disinformation Campaigns vs. Attribution Claims
Explore disinformation campaigns and attribution claims in cybersecurity, examining their impact and challenges in accurately identifying threat actors.
Háček - Computing a Hacker Experience
Explore the intersection of hacking and computing through an innovative performance experience, blending technology, music, and interactive elements.
Memory Forensics & Security Analytics - Detecting Unknown Malware
Explore advanced techniques in memory forensics and security analytics for detecting unknown malware, enhancing your cybersecurity skills and threat detection capabilities.
Launching an InfoSec Career
Explore diverse paths to cybersecurity careers, from CTFs to bug bounties. Learn key strategies for success, including self-teaching, building a unique skill set, and leveraging your online presence as a resume.

How the Feds Caught Russian Mega-Carder Roman Seleznev
Uncover the intricate investigation that led to the capture of Russian hacker Roman Seleznev, responsible for massive credit card fraud and point-of-sale hacks, through electronic evidence and international cooperation.
Memory Forensics Using Virtual Machine Introspection for Cloud Computing
Explore memory forensics in cloud environments using virtual machine introspection. Learn techniques for trustworthy data collection without system interference, ideal for digital forensics in virtualized settings.
What's the DFIRence for ICS?
Explore digital forensics for industrial control systems, focusing on embedded devices in critical infrastructure. Learn data collection and analysis techniques for RTUs in electric substations.
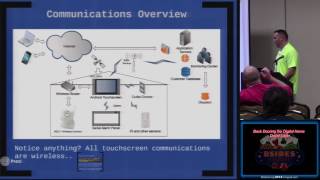
Back Dooring the Digital Home
Explore techniques for compromising smart home devices and networks, uncovering vulnerabilities in digital home security systems and IoT appliances.
Poppin' - Digital Locks
Explore password security vulnerabilities in physical and digital systems, with demonstrations of attack techniques and countermeasures for both mobile and web applications.
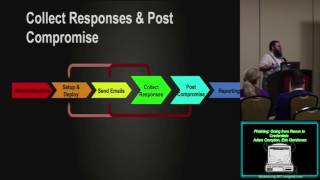
Phishing - Going From Recon to Credentials
Learn effective phishing techniques, from reconnaissance to credential harvesting. Explore tools, automation, and the Speed Fishing Framework in this comprehensive overview.
ZOMG It's OSINT Heaven!
Explore advanced OSINT techniques and tools for gathering intelligence from open sources, enhancing your cybersecurity and investigative skills.
Yes, You Too Can Perform Daring Acts of Live Acquisition
Learn techniques for live digital forensics, including memory acquisition, disk analysis, and artifact collection. Explore free tools and best practices for gathering crucial system information.
Flaying the Blockchain Ledger for Fun, Profit and Hip Hop
Explore blockchain technology, Bitcoin mechanics, and data analysis techniques to uncover insights from cryptocurrency transactions and wallets.
Früher oder später erwisch ich euch alle! Über Digitalforesnik und ihre Möglichkeiten
Einblick in die Welt der Digitalforensik: Entdeckung und Analyse digitaler Spuren, Methoden zur Beweissicherung und Herausforderungen bei der Aufklärung von Cyberkriminalität. Praxisnahe Beispiele veranschaulichen die Arbeit von IT-Forensikern.
Lord of War - Investigating the Theft of a Gambling Platform and Outsmarting the Thieves
Forensic investigation of a gaming platform theft in Ukraine, using original evidence. Insights into cybercrime, hacker tactics, and investigative techniques in hostile jurisdictions.
Blue Is the New Black - Privacy Leaks and Re-Victimization from Police-Auctioned Cellphones
Explore privacy risks and re-victimization issues arising from police-auctioned cellphones, uncovering potential data leaks and their implications for personal security and law enforcement practices.
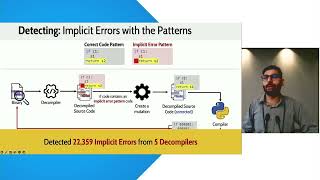
PyFET - Forensically Equivalent Transformation for Python Binary Decompilation
Explore forensically equivalent transformation techniques for decompiling Python binaries, enhancing reverse engineering capabilities and code analysis.

The Investigators Labyrinth - A Data-Driven Perspective
Explore data-driven perspectives on digital forensics and incident response, focusing on cognitive challenges, investigation processes, and analytical strategies for security professionals.