Privacy Risks and Protections in Machine Learning Systems
Explore privacy vulnerabilities in ML systems and learn robust protection strategies to safeguard sensitive training data while maintaining system effectiveness and user trust.
Privacy-Aware Compression for Federated Data Analysis - Seminar 86
Explore privacy-aware compression techniques for federated data analysis, focusing on innovative methods to balance data privacy and efficiency in distributed learning environments.
Missing Mass and Optimal Discovery in Power Systems Security Analysis
Explore advanced statistical modeling and machine learning concepts through probabilistic expert advice, focusing on security analysis in power systems and Good-Turing missing mass estimation techniques.
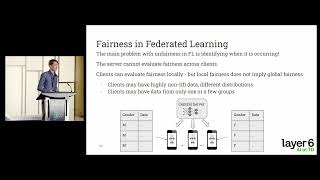
Navigating the Tradeoff Between Privacy and Fairness in Machine Learning
Explore the intersection of privacy and fairness in ML, addressing challenges and research-based solutions for regulated industries.
Privacy-Preserving Machine Learning: Strategies and Tools
Explore privacy-preserving machine learning tools and strategies through practical examples, considering risk, implementation complexity, and computational resources.
Privacy-Preserving Machine Learning
Explore strategic approaches to privacy-preserving machine learning, including federated learning, encryption, and differential privacy, with practical examples and risk considerations.
Federated Learning Tutorial: Concepts, Applications, Challenges, and Framework
Explore federated learning concepts, applications, challenges, and frameworks. Gain insights into collaborative machine learning while preserving data privacy and security.
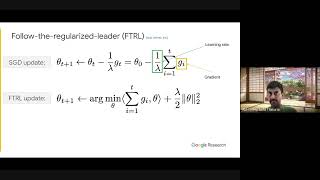
Federated Learning with Formal User-Level Differential Privacy Guarantees
Explore federated learning with user-level differential privacy guarantees. Discover scalable algorithms for industrial workloads in data privacy and machine learning.
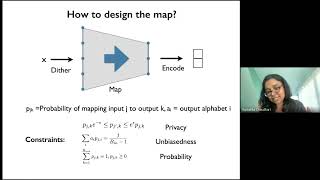
Privacy-Aware Compression for Federated Learning
Explore privacy-aware compression techniques for federated learning, addressing challenges and implementing local differential privacy mechanisms to enhance data protection in collaborative AI.
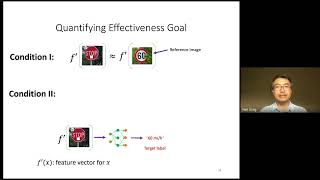
Secure Self-supervised Learning: Challenges and Solutions
Explore secure self-supervised learning techniques, focusing on backdoor attacks, data auditing, and membership inference for pre-trained encoders in machine learning.
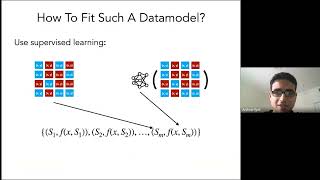
Mapping from Training Data to Predictions with Datamodels - Differential Privacy in Machine Learning
Explore datamodels in machine learning, from training data to predictions. Learn about model brittleness, data counterfactuals, and applications in ML pipelines.
Example Memorization in Learning: Batch and Streaming - Differential Privacy for ML
Explore example memorization in machine learning, covering batch and streaming scenarios, space requirements, and implications for natural models and future research directions.
Differentially Private Diffusion Models Generate Useful Synthetic Images
Explore privacy-preserving synthetic image generation using diffusion models. Learn techniques for fine-tuning pre-trained models to achieve state-of-the-art results on CIFAR-10 and Camelyon17 datasets.
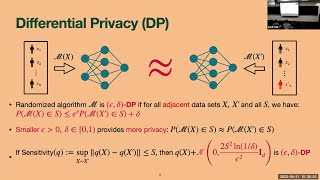
Private Stochastic Optimization with Large Worst-Case Lipschitz Parameter
Explore differentially private stochastic optimization techniques for loss functions with large worst-case Lipschitz parameters, addressing outliers and heavy-tailed data for improved excess risk bounds.
Practical Cryptographic Solutions for Secure Inference and Private Benchmarking
Explore practical cryptographic solutions for secure inference and private benchmarking in machine learning, presented by Nishanth Chandran at PPML 2024.
Samplable Anonymous Aggregation for Private Federated Data Analysis
Kunal Talwar explores samplable anonymous aggregation for private federated data analysis, discussing innovative approaches to privacy-preserving machine learning in distributed settings.

Privacy Backdoors: Stealing Data with Corrupted Pretrained Models - Explained
Explore how tampering with pretrained models can compromise privacy, enabling attackers to reconstruct finetuning data. Learn about privacy backdoors in transformers and their implications for machine learning security.
Differentially Private Release of Spatio-Temporal Data Statistics
Explore strategies for releasing spatio-temporal data statistics with differential privacy, focusing on sample mean and variance calculations while minimizing reconstruction errors in urban data management.
Flipped Huber - A New Additive Noise Mechanism for Differential Privacy
Discover a novel additive noise mechanism for differential privacy that combines Laplace and Gaussian distributions, offering enhanced privacy protection while maintaining data accuracy in query responses.
Efficient Speech Processing
Explore cutting-edge research in speech recognition, generation, and privacy. Learn about self-training algorithms, error correction models, joint text-to-speech modeling, and privacy-preserving techniques in speech processing.
Defending Against Data Reconstruction Attacks in Federated Learning: An Information Theory Approach
Explore advanced defense strategies against data reconstruction attacks in federated learning through information theory, focusing on privacy preservation and efficient training methods.