Jumpstarter: Enabling Open Hardware-in-the-Loop Testing
Automate embedded software testing with Jumpstarter, integrating hardware-in-the-loop into CI/CD pipelines for faster, more consistent results. Explore the dutlink-board and its expandable functionality.

Securing the Supply Chain: A Practical Guide to SLSA Compliance from Build to Runtime
Practical guide to securing software supply chain using CNCF tools. Covers SLSA compliance, GitHub Actions, Cosign, Kyverno, in-toto, and Kubescape for build-to-runtime security in Kubernetes ecosystems.
Enforceable Supply Chain Security Policy with OPA Gatekeeper and Ratify
Explore container supply chain security using OPA Gatekeeper and Ratify. Learn to enforce policies, verify images, and establish trust in deployments for a more secure container ecosystem.

Accelerating Electric Vehicle Innovation with Cloud Native Technologies
Explore how NIO leverages cloud native tech like Containerd, Kubernetes, and KubeEdge to enhance EV software development, driving innovation in vehicle intelligence and connectivity.
DevSecOps: Connecting Developers, Security, and Operations
Explore DevSecOps methodology, connecting developers, security, and operations. Learn about tooling, cloud security automation, and the importance of continuous learning in fostering a collaborative DevSecOps culture.
Reproducible Builds with BuildKit for Software Supply Chain Security
Learn how BuildKit enables reproducible builds to enhance software supply chain security, ensuring verifiable and trustworthy Docker images through bit-for-bit identical reproduction from source code.
Guide to Authentication and Authorization for Cloud Native Applications with Keycloak
Explore Keycloak for robust authentication and authorization in cloud-native apps. Learn about single sign-on, passwordless auth, social login, and secure API profiles for enhanced security and user experience.
Beyond Guidelines - Designing and Implementing Robust Build Pipelines
Learn to design and implement secure build pipelines beyond standard guidelines. Explore practical tools and methods to enhance supply chain security and protect against rising attacks.
Fully Automated Power Measurement Solution with IC Temperature Control
Explore automated power measurement and temperature control for embedded Linux platforms, featuring innovative solutions for characterization and Operating Performance Points optimization.
The 'S' in IoT Stands for Security - Securing Connected Devices
Explore IoT security challenges, recent breaches, and how containerization can enhance device protection. Learn best practices for building secure IoT devices and managing their lifecycle.
Safety vs Security: A Tale of Two Updates
Explore the tension between safety and security in product updates, focusing on embedded systems. Learn strategies to balance these conflicting needs in development and maintenance.
Everything-as-Code: Pushing the Boundaries of SAST
Explore the evolution of SAST in the "everything as code" era, examining challenges in analyzing infrastructure, contracts, and circuits, with focus on Bicep and Solidity languages.
Navigating the Software Supply Chain Defense Landscape
Explore software supply chain security tools and frameworks, their integration, and how to select the right combination for comprehensive protection against rising cyber threats.
The Power of Observability - Merging, Scaling and DevSecOps
Explore observability's role in merging, scaling, and DevSecOps. Learn how Dustin Web Development harmonized their monitoring landscape for improved efficiency and security.
The End of DevSecOps? - Leveraging New Tools and AI in Engineering-First Security
Explore how Generative AI and new tools can simplify communication, reduce toil, and integrate security seamlessly into engineering processes, moving beyond traditional DevSecOps.
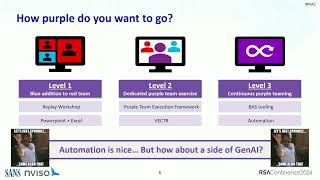
The Always-On Purple Team: Automated CI/CD for Detection Engineering
Innovative architecture for automated detection engineering CI/CD pipeline, merging SOC technologies, SIEM/XDR, SOAR, BAS, and ChatGPT. Includes live demo of creating, testing, and deploying detection analytics.
Open-Source Margo Initiative - Tackling Interoperability Challenges in Industrial Automation
Explore the Margo Initiative's approach to solving interoperability issues in industrial automation, focusing on orchestration at scale for edge applications and devices.
Mapping CI/CD Attack Surfaces - Strategies and Insights
Explore CI/CD attack surface mapping with insights on problem areas, blind spots, and actionable strategies. Learn about future advancements in reducing vulnerabilities in CI/CD ecosystems.
Leveraging Sigstore Capabilities in a Local Environment
Explore Lockheed Martin's integration of Sigstore for secure, auditable software development. Learn about internal Kubernetes deployments, certificate authorities, and streamlined GitLab pipelines for enhanced security.
Securing Software Repositories - EMEA Friendly
Explore strategies for securing software repositories, focusing on best practices and tools to protect against vulnerabilities and ensure code integrity.
Breaking Barriers: Triumphs of Cultural Diversity in Global Open Source Communities
Explore the growth of Indian contributors in global open source, focusing on strategies for mentorship, leadership, communication, and accessibility to foster diversity and inclusion in OSS communities.