What's New in Dynatrace - Release 1.293
Explore Dynatrace v1.293 updates: AI-driven quality gating, histogram charts, enhanced zooming, document ownership visibility, Snyk fix recommendations, Grail events, Davis problem querying, and team ownership features.
Using Snyk to Find & Fix Vulnerabilities
Learn to use Snyk for finding and fixing vulnerabilities in web applications, including hands-on practice with a vulnerable app and a CTF challenge involving prototype pollution and RCE.
Custom Java Deserialization Exploit - Serial Snyker
Explore Java deserialization vulnerabilities and create custom exploits for remote code execution in this hands-on tutorial, featuring practical examples and step-by-step guidance.
Snyk Integrations
Learn key Snyk integrations for beginners: IDE setup, reporting, CLI usage, Git onboarding, and Jira ticket creation. Ideal for new users or administrators seeking to optimize their Snyk experience.
Impact of Open Source Adoption on Software Security
Explore the impact of open source on software security with insights from Linux Foundation and Snyk's joint research, covering key findings and industry trends.
Open Source Cybersecurity - Addressing Challenges in Software Security
Explore open source cybersecurity challenges and solutions with industry experts, discussing survey findings, enterprise impacts, and automation strategies for improved software security.
Addressing Cybersecurity Challenges in Open Source Software - June 29, 2022
Explore cybersecurity challenges in open source software, focusing on organizational priorities, improvement strategies, and policy drivers. Gain insights from Snyk and Linux Foundation research.

Fixing Security Flaws in Spring Boot Applications with IntelliJ IDEA and Snyk
Learn to identify and resolve security vulnerabilities in Spring Boot applications using IntelliJ IDEA and Snyk. Discover techniques to maintain secure code and manage open-source library risks effectively.
Shifting Security from Right to Left
Discover how to integrate security into your development workflow using Snyk's tools in IntelliJ IDEA, enabling early detection and remediation of vulnerabilities in project dependencies.
Hands-on Introduction to Snyk - Security Scanning for Dependencies, Code, and Containers
Comprehensive introduction to Snyk, covering dependency security, code analysis, container scanning, and Kubernetes YAML scanning. Hands-on demonstration of Snyk's features for identifying and addressing vulnerabilities.
7 Must-Know Steps to Making Modern Web Apps Ultra-Secure
Learn 7 essential steps to enhance web app security. Master prevention of vulnerabilities, implement secure authorization, add security layers, logging, and testing for robust protection.
MacGyverOps: Secure Your Development Environment with the Tools Around You
Leverage existing tools to create focused security feedback, minimizing distractions while enhancing development velocity and security in DevOps environments.
Securing Supply Chains in C++, Java and JavaScript - Episode 133
Explore supply chain security across C++, Java, and JavaScript ecosystems. Learn about challenges, dependencies, versioning, and software bill of materials (SBOMs) from industry experts.
Malicious Packages and Malicious Intent - Episode 123
Explore malicious attacks, open source security, and practical tips for improving company safety with Liran Tal, director of developer advocacy at Snyk and Github Star.
Exploiting AI-Generated Code Vulnerabilities and Their Solutions
Discover vulnerabilities in AI-generated code and learn how to exploit and fix them. Gain insights into potential security risks and implement effective solutions using Snyk.
Developer Security Essentials
Discover how attackers exploit code vulnerabilities and learn to identify and fix complex security issues efficiently. Participate in a hands-on hacking session to address open source security problems.
Container Security for Developers - Best Practices and Exploit Prevention
Explore container security essentials, from vulnerability scanning to runtime hardening. Learn practical techniques to build secure containers and minimize exploit risks in Kubernetes environments.
Integrations 101
Learn essential Snyk integrations for IDE setup, reporting, CLI usage, Git onboarding, and Jira ticket creation. Ideal for new users, administrators, and those seeking to enhance their Snyk experience.
Snyk Image Scanning for Node.js and Docker Best Practices
Explore Node.js and Docker best practices with industry experts, focusing on image scanning and security considerations for containerized applications.
Docker Build: Build Secure Containers with Docker and Snyk
Learn to secure containers using Snyk Vulnerability Scanning integrated with Docker Desktop and Docker Hub. Discover a workflow for building safer, more robust containerized applications.
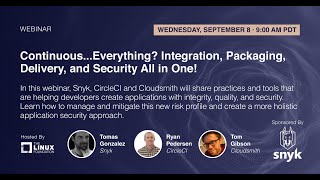
Continuous Integration, Packaging, Delivery, and Security - Best Practices for Modern Application Development
Explore modern application delivery pipelines, focusing on security, quality, and integrity. Learn to manage open-source components, mitigate supply chain risks, and implement continuous security practices.