Attacking and Defending Supply Chains - How We Got Admin in Your Cloud
Explore software supply chain vulnerabilities leading to secrets exfiltration and privilege escalation, with best practices for securing reference architectures and production environments.
The Secret Life of Secrets - Designing Secure API Keys
Explore API key design strategies, security measures, and best practices for creating robust and secure API authentication systems.
Accelerating Electric Vehicle Innovation with Cloud Native Technologies
Explore NIO's use of cloud native technologies to enhance EV software development, addressing challenges in consistency, testing, and data utilization between simulated and real-world environments.
Network ACLs Made Easy: Establishing Zero Trust Network Policies
Learn to automate Zero Trust network policies using AWS VPC Flow Logs and Terraform. Discover techniques for analyzing traffic data, optimizing security groups, and implementing efficient access controls without third-party solutions.
Threat Modeling for AI Apps with Attacks as Code
Explore automated threat modeling for AI apps using Secops-Chaos framework. Learn to encode TTPs as security experiments and map MITRE ATLAS TTPs to AI apps in Kubernetes environments.
Scan, Patch, VEX - Using Open Source Tools to Manage Vulnerabilities in Containers
Learn to manage vulnerabilities in cloud-native environments using open-source tools like Trivy and Copacetic, and standards like VEX. Improve security across development, testing, and production.
How to Generate VEX Automatically for Your Project
Learn to automate VEX generation for Kubernetes workloads, reducing false positives in security scans and streamlining vulnerability management using Kubescape and a new GitHub Action.
SPIFFE Ecosystem: MTLS and Identity with Linkerd and Teleport
Explore SPIFFE ecosystem growth, focusing on Linkerd and Teleport's implementation for workload identity verification across Kubernetes clusters and external environments.
Securing Open Source Software with Platform One and Canonical
Explore securing open source software, minimal containers, and security scanning with Platform One and Canonical experts.
Let's Encrypt Certificates Management with TLS-certificates-interface and ACME Operators
Learn to automate Let's Encrypt certificate management using TLS-certificates-interface and ACME operators. Discover how to create software operators for various DNS service providers quickly and efficiently.
BuildSafe Deep Dive - Getting Supply Chain Security Right Using Nix
Explore BuildSafe's capabilities for secure application builds using Nix, including package search, CVE information, and simplified development workflows.
Supply Chain Security - The First Steps
Explore supply chain security essentials, including zero trust, SBOMs, and sigstore. Learn to generate and utilize SBOMs to enhance software development security and meet compliance requirements.
Increase Security Posture in Software Delivery with Red Hat Trusted Software Supply Chain
Enhance software security with Red Hat's Trusted Supply Chain: protect components, predict vulnerabilities, and improve resilience through advanced tools and practices.
Hunting Down the Monsters Hidden in Your Software Supply Chain
Uncover and mitigate hidden threats in your software supply chain. Learn effective strategies to enhance security and protect against vulnerabilities.
Secure Your App: DevSecOps Trusted Application Supply Chain
Explore DevSecOps principles and implement a trusted application supply chain to enhance app security and streamline development processes.
Building a Security Audit Logging System on a Shoestring Budget
Learn to build a robust, security-focused audit logging system for fast-growing companies with limited resources. Discover cost-effective strategies and lessons from combining software engineering and hacker culture.
Rollout Hardcoded Secrets Detection with Minimum Effort and Maximum Impact
Learn effective strategies for detecting hardcoded secrets in your codebase, minimizing effort while maximizing impact on security and compliance.
Preserving Anonymity in Data Collection - The Story of Differential Privacy
Explore differential privacy techniques for collecting user data while preserving anonymity. Learn key concepts, historical development, and potential applications in software telemetry.

Gaining Initial Access by Exploiting Leaked Credentials
Explore how attackers exploit leaked credentials to breach organizations and learn effective prevention strategies for safeguarding sensitive information.
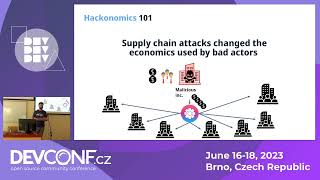
The Internet is Broken: Breaking Down the Software Supply Chain
Explore modern software vulnerabilities, recent supply chain attacks, and actionable steps to build secure applications in an insecure internet environment.
An Introduction to Sigstore for Pythonistas
Explore Sigstore for securing Python projects: learn to sign, verify, and protect software artifacts, addressing supply chain vulnerabilities with accessible tracing methods.