Common Webapp Vulnerabilities and What to Do About Them
Explore common web app vulnerabilities and practical mitigations based on the OWASP Top 10 List, focusing on injection attacks, authentication issues, and data exposure risks.
Implementing Physical Units Library for C++
Explore challenges and solutions in designing a Physical Units Library for C++, leveraging C++20 features for improved usability, maintainability, and extensibility.
The Anatomy of an Exploit
Explore exploit development through C and x86_64 assembly, gaining insights into security vulnerabilities and the attacker's perspective for more secure coding practices.
Assume Worst Intent - Designing for the Abusive Ex
Explore designing apps with consideration for vulnerable users, focusing on potential misuse by stalkers or abusive individuals. Learn threat models and strategies to enhance user safety.
M-PIN Authentication in Vehicle Tracking
Explore Apache Milagro for secure IoT authentication in vehicle tracking. Learn about post-PKI internet, stronger security, and independence from third-party trust authorities through a C++14 fleet management example.
Delivering Software That Is Secure and Usable - Whose Job Is It?
Explore the intersection of security and usability in software development with insights from a leading expert in human-centered security and privacy solutions.
Secure by Design - Security Principles for the Working Architect
Explore key security principles for system design, focusing on practical application in mainstream development. Learn to create securable systems without relying on specialized security engineering jargon.
Make Your Programs More Reliable with Fuzzing
Explore fuzzing techniques to enhance program reliability when handling external data. Learn about its history, current tools, and real-world applications in libc++ and Boost.
Dynamic Polymorphism With Code Injection and Metaclasses
Explore advanced C++ techniques for dynamic polymorphism using code injection and metaclasses, offering alternatives to traditional virtual functions and inheritance for improved performance and flexibility.
API Vulnerabilities and What to Do About Them
Explore top API security vulnerabilities and practical mitigations. Learn about OWASP's API Security Top 10, current threat landscape, and essential strategies to protect your APIs from common attacks.
A Friendly Introduction to Rust for C++ Developers
Friendly introduction to Rust for C++ developers, highlighting key features, similarities, and differences. Includes code comparisons and insights on memory safety, performance, and low-level control.
The Hip Approach to Safeguarding Your Users
Explore innovative approaches to cybersecurity, privacy, and harm prevention in software development. Learn to make informed safeguarding decisions using industry-wide security information and DevOps tools.
Classic Vulnerabilities
Explore classic software vulnerabilities, their recent resurgence, and modern tools for detection and prevention. Learn from history to enhance security in today's development practices.
Do You Want Fries With That? From Punched Cards to DevOps and Beyond
Explore software development's evolution from punched cards to DevOps, examining why security is often seen as an 'extra' responsibility and celebrating developers' adaptability across eras.
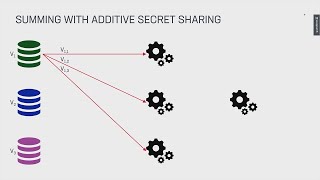
Introduction to Secure Multi-Party Computation
Explore secure multi-party computation techniques for joint calculations on private data without revealing inputs. Learn about homomorphic encryption, garbled circuits, and secret sharing.
Dirty Samba Hacks to Make Your Life Easier
Discover practical Samba hacks for efficient user management, file handling, and system integration. Learn tips for scripting, querying, and implementing secure solutions in enterprise environments.
How Much Do You Trust That Package? Understanding the Software Supply Chain
Explore software supply chain security risks, including package vulnerabilities and malicious code injection. Learn strategies to mitigate these risks in modern software development.

How to Disappear Completely
Explore urban camouflage techniques to evade facial recognition, delving into the technology, ethics, and legislation surrounding biometric identification.

My Year on the Front Line - Cleaning Infected Sites
Insights from a year cleaning infected WordPress sites: memorable cases, favorite malware, persistent attackers, and tips to protect your site from compromise.
Disaster Recovery Book
Learn to create effective operational runbooks for software development teams, covering industry standards, best practices, and guidelines for writing, maintaining, and utilizing these essential tools for incident response and support.
FPGA Based Mobile Phone - Creating a Truly Open and Trustable Mobile Communications Device
Explore the creation of an open-source, trustable mobile device using FPGA technology, addressing privacy concerns and digital sovereignty while offering unique features like C64 compatibility.