Practical SMEP Bypass Techniques
Explore practical techniques for bypassing Supervisor Mode Execution Prevention (SMEP) in system security, enhancing your understanding of kernel exploitation and protection mechanisms.
Exploit Engineering: Attacking the Linux Kernel
Explore Linux kernel exploitation techniques, from attack surface mapping to vulnerability discovery and exploit development. Gain insights into advanced kernel exploitation methods and tools.
Abusing Linux In-Kernel SMB Server to Gain Kernel Remote Code Execution
Explore Linux kernel vulnerabilities and gain insights into exploiting the in-kernel SMB server for remote code execution.
SLUB Internals for Exploit Developers
Explore SLUB allocator internals and slab memory shaping strategies for Linux kernel exploit development. Gain insights into controlling memory corruption and implementing effective exploit techniques.
From BYOVD to 0-Day - Unveiling Advanced Exploits in Cyber Recruiting Scams
Unveiling sophisticated cyber-attacks disguised as job recruitment, featuring 0-day exploits and advanced rootkit capabilities. Explores novel attack methods targeting Asia, bypassing security measures.
Breaching the Depths of the Abyss: Exposing Rootkits - Track 2, Session 4
Dive deep into rootkits: explore their inner workings, detection techniques, and countermeasures. Learn to identify and neutralize these stealthy threats using advanced tools like Living Off The Land Drivers.
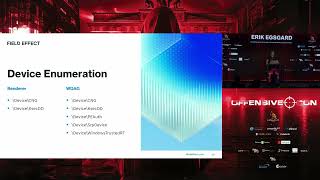
Attacking Windows Device Drivers: Almost Escaping the Sandbox
Explore techniques for attacking Windows device drivers and potential sandbox escape methods in this advanced security analysis presentation.
Practical Exploitation of Registry Vulnerabilities in the Windows Kernel
Explore practical exploitation techniques for Windows kernel registry vulnerabilities, enhancing your understanding of system security and potential attack vectors.
Your Mitigations Are My Opportunities - Windows Exploitation and Bypass Techniques
Explore Windows exploitation techniques, bypassing security measures like HVCI and EDR, with insights on disabling drivers and practical demonstrations.

Ring 0 to Ring -1 Exploitation with Hyper-V IPC
Explore advanced exploitation techniques targeting Hyper-V's inter-process communication, moving from kernel-level to hypervisor-level vulnerabilities in virtualized environments.
HotBPF++ - A More Powerful Memory Protection for the Linux Kernel
Explore HotBPF++, an advanced Linux kernel memory protection system. Learn about its automatic deployment, on-the-fly enabling, and lightweight design for preventing and detecting various memory corruptions beyond heap exploitation.
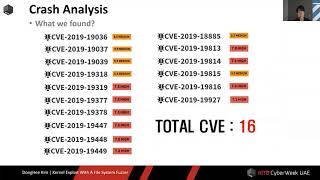
Kernel Exploitation with a File System Fuzzer
Explore kernel exploitation using a filesystem fuzzer, uncovering vulnerabilities and demonstrating R/W primitive attacks and control flow hijacking in Linux systems.
Kernel Pwning with eBPF - A Love Story
Explore eBPF technology, its impact on Linux kernel capabilities, and potential security vulnerabilities. Learn about verifier exploits and achieving code execution in the kernel.
Android Universal Root - Exploiting Mobile GPU - Command Queue Drivers
Explore GPU hacking techniques and vulnerabilities in Android device drivers, focusing on rooting methods and security implications for mobile systems.
Turning - Page Tables - Bypassing Advanced Kernel Mitigations Using Page Tables Manipulations
Explore advanced kernel exploit techniques using page table manipulations to bypass Windows 10 mitigations. Learn virtualization-based security and memory management concepts.

Exploiting Race Conditions Using the Scheduler
Explore techniques for exploiting race conditions in Linux and Android using scheduler manipulation, focusing on real-world vulnerabilities and practical exploitation strategies.
XNU Heap Exploitation - From Kernel Bug to Kernel Control
Exploración detallada de la explotación del heap XNU, analizando dos vulnerabilidades del kernel y tres exploits. Cubre internos de XNU, técnicas de explotación y cambios entre versiones de iOS.
iOS 10 Kernel Heap Revisited
Detailed exploration of iOS 10 kernel heap implementation, discussing Apple's counter-measures against exploitation techniques and potential attacker adaptations in iOS 9 and 10 beta versions.
Swiping Through Modern Security Features
Exploring iOS 6 security features and jailbreak techniques, including kernel ASLR, code signing, and exploit methods. Insights from expert developers on bypassing modern mobile security protections.
Exploiting Kernel Races through Taming Thread Interleaving
Explore advanced techniques for exploiting kernel race conditions by manipulating thread interleaving, overcoming limitations of conventional brute-force methods and addressing challenging vulnerabilities.
Social Engineering the Windows Kernel - Finding and Exploiting Token Handling Vulnerabilities
Explore Windows kernel token handling vulnerabilities, learn to identify and exploit them for privilege escalation, and understand patterns for conducting security reviews.