A Short Course in Cyber Warfare
Explore cyber warfare's complexities, including policy, strategy, and tactics. Gain insights into organizational structures and factors contributing to success in this evolving domain of conflict.
Uncovering Large Scale Fraud Operations
Uncover advanced fraud techniques targeting digital credentials and learn strategies to counter large-scale account takeover threats in the wake of accelerated digital transformation.
Your Metrics Suck - 5 SecOps Metrics That Are Better Than MTTR
Explore effective SecOps metrics beyond MTTR, focusing on business confidence, driving change, and improving SOC performance. Learn about configuration, analyst activity, and process deviation.
Top Active Directory Attacks - Understand, then Prevent and Detect
Explore common Active Directory attacks, prevention strategies, and detection methods. Learn to secure enterprise networks against prevalent hacking techniques and enhance cybersecurity practices.
Biohacking - The Invisible Threat
Explore bio-hacking, bio-implants, and their impact on physical and digital security. Learn about augmented humans, contactless technology risks, and mitigation strategies.
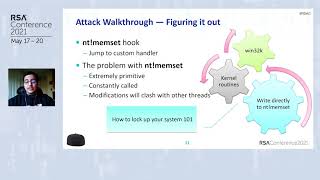
Windows Kernel Patch Protection - Achilles Heel - PatchGuard
Explore critical flaws in Windows Kernel Patch Protection, learn attack techniques to disable PatchGuard, and discover proposed mitigations for enhanced system security.
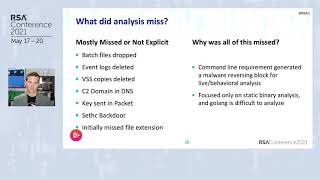
Ransomware - Creation, Detection, and Response
Explore ransomware creation, detection, and response strategies. Learn evasion techniques, novel detection methods, and tailored incident response approaches from real-world engagements.
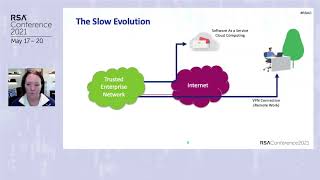
Building Secure and Reliable Systems at Scale
Learn Google's best practices for building secure, reliable systems at scale through automated security, containment, and multi-party techniques that foster a culture of review and resilience.
CISO Leadership - Building Your Personal Action Plan
Develop leadership skills for security teams through actionable strategies, including team building, feedback models, strategic planning, and career management techniques.
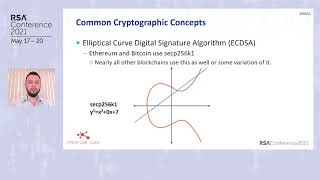
Blockchain Security Guarantees and Exploits
Explore blockchain security, private key generation, and vulnerabilities. Learn about scanning techniques, potential exploits, and best practices for protecting digital assets.
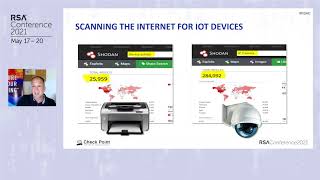
Into the Mind of an IoT Hacker - How to Protect IoT Networks & Devices
Explore IoT hacking techniques and learn effective strategies to secure networks and devices against cyber threats, vulnerabilities, and attacks in various organizational settings.
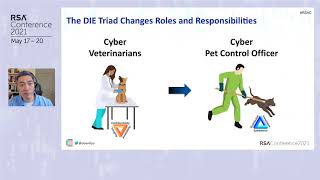
Death to CIA! Long Live DIE! - How the DIE Triad Helps Us Achieve Resiliency
Explore the DIE Triad (Distributed, Immutable, Ephemeral) as an alternative to CIA, reducing security burden and enabling true resiliency. Learn to apply DIE principles for tackling security, resiliency, and privacy challenges.
FAIR Controls - A New Kind of Controls Framework
Explore a new framework for measuring cybersecurity control value, enabling more effective resource allocation and decision-making in information security management.

Learning from the Enemy - A Look Inside the Techniques of Ocean Lotus - APT32
Explore tools and techniques of real-world threat actors like OceanLotus/APT32, gaining firsthand insights into cybercriminal operations and enhancing your defense strategies.
Cyber Resilience - Say What?
Explore cyber resilience strategies, implementation methods, and actionable steps to enhance organizational security through existing programs and meaningful metrics.

Building Your Cybersecurity Architecture Planning Toolbox
Learn to build and effectively use a cybersecurity architecture toolbox, covering analytical, informational, and design tools for successful security planning and implementation.
Quantum Computing - One Weird Trick to Break RSA Encryption
Explore quantum computing's impact on encryption, including Shor's Algorithm, current quantum tech status, and future implications for cybersecurity. Learn about quantum cryptography and industry developments.
How You Can Ask the Right Questions to Succeed with Your Security Projects
Learn to ask effective questions in security projects, enhancing discovery, planning, and persuasion skills through real-world examples and practical techniques for better communication and project success.
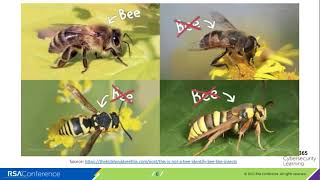
What Cybersecurity Practitioners Can Learn from Honeybees
Explore the fascinating parallels between honeybee colonies and cybersecurity organizations, learning valuable insights for threat detection, risk assessment, and organizational structure.
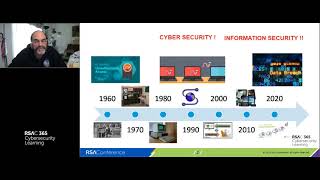
Remember When We Used to Call It "Information Security"? Let's Go Back to That
Experts discuss shifting focus back to information security, exploring advancements in identity management and encryption to better protect data in an interconnected world.
My Threat Model is Your Threat Model
Explore evolving threat landscapes, from nation-state conflicts to sophisticated attacks on individuals and devices. Learn about below-OS mitigations to protect BIOS, firmware, and data.