Blue Team Fundamentals
Explore effective strategies to counter common cyber attacks, including credential stuffing, phishing, and RCE attempts, with practical takeaways to enhance your organization's security posture.
Using Ancient Math to Speed Up Security Assessments of Windows Executables
Discover how to accelerate Windows executable security assessments using Euclidean Distance and Bayes Theorem, enabling rapid triage and efficient risk reduction in regulated environments.
Caught My WebApp Cheating on Me
Exploring techniques to detect and prevent client-side injections and tampering in web applications, ensuring integrity and security of code executed in the browser.
Practical Steps for Reducing Exposure and Detecting Compromise
Strategies for securing DNS services, protecting against common attacks, and monitoring traffic for compromise. Covers both authoritative and recursive perspectives to enhance overall network security.
Moving Security from Cost Center to Revenue Generator
Discover strategies to transform security from a cost center to a revenue generator by communicating its value in financial terms and highlighting revenue enabled by effective security measures.
Unraveling the Threat of Chrome Based Malware
Explore Chrome extension vulnerabilities, their potential for network compromise, and strategies for identifying and mitigating risks in enterprise environments.
Tales of Red Teaming - Continuous Intrusion Continuous Deception
Explore advanced red teaming techniques for attacking large corporate networks, including compromising deployment systems, backdooring software, breaking out of containers, and exploiting misconfigurations in multi-tenant systems.
Overcoming Obstacles in Operationalizing Security - A Tale from the Trenches
Practical insights on implementing security strategies in startups, addressing challenges like limited budgets and talent shortage. Learn to anticipate obstacles and make sensible trade-offs in real-world scenarios.
From Bounties to Bureaucracy - The Hidden Market Factors of Exploit Economics
Explore the evolution of bug bounty programs, their impact on cybersecurity, and how they shape the vulnerability marketplace. Learn about exploit trends, disruption of threats, and future predictions in this insightful talk.
Fuzzing Ruby and C Extensions
Explore fuzzing techniques for Ruby and C extensions, focusing on security implications and using AFL fuzzer to identify vulnerabilities in Ruby language and gems.
PostgreSQL Threats and Attacks in the Wild
Explore PostgreSQL vulnerabilities through honeypot findings, including exploits, malware, and brute force attacks. Learn about honeypot development and integration with security tools.
Privacy for Safety - OPSEC When the Threat is in the Home
Exploring digital safety strategies for individuals facing threats within their homes, focusing on improving awareness and tools to protect vulnerable groups from domestic abuse.
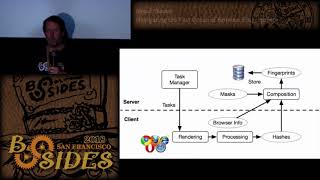
Navigating the Vast Ocean of Browser Fingerprints
Explore browser fingerprinting and machine learning for fraud detection, combining techniques to create effective blue team applications and enhance cybersecurity measures.

Hacking the Law - Are Bug Bounties a True Safe Harbor?
Explore the legal risks and challenges of bug bounty programs, examining potential liabilities for hackers and suggesting steps to create safer legal environments for vulnerability disclosure.
The SecDevOpronomicon - Arcane Secrets for Scaling Your Company’s Security
Uncover arcane secrets for scaling security efforts in fast-paced development environments. Learn high-value engineering techniques, custom analyses, and CI/CD pipeline integration to enhance SecDevOps practices.
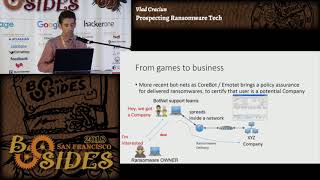
Prospecting Ransomware Tech
Análisis detallado de las tecnologías y tendencias de ransomware en 2017, explorando mezclas de técnicas maliciosas, métodos de propagación y algoritmos de cifrado utilizados por diversas familias de malware.
Your Secrets are Showing - How to Find if Your Developers are Leaking Secrets
Discover tools and techniques to identify and prevent sensitive information leaks in source code repositories, both within corporate networks and on public platforms.
Hacking the Bank - Figuring Out What the Cost of Hacks May Be
Exploring the financial impact of cyber breaches, including accounting discrepancies, disclosure issues, and real-world case studies. Offers insights on improving cost estimation and accounting for hacking attacks.
The End of Security Stupidity
Experts discuss the end of ineffective practices in information security, predicting a shift towards more meaningful certifications, better training, and effective solutions to combat cyber threats.
Yet Another Type of Application Layer Denial of Service Attack
Explore a novel Application Layer DoS attack exploiting slow data acceptance by clients. Learn about attack vectors, detection methods, and mitigation strategies for this overlooked vulnerability.
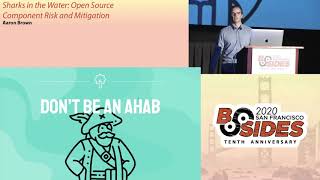
Sharks in the Water - Open Source Component Risk and Mitigation
Explore open source component risks and mitigation strategies, focusing on supply chain vulnerabilities, recent hacks, and preventive measures through education and automated tooling.