Standing Up a Successful Product Security Program
Insights from industry leaders on establishing effective product security programs, covering design, awareness, and response strategies for major cyber threats.
Reality Check - The Story of Cybersecurity
Explore the human element in cybersecurity, challenging simplified views and examining the true narrative behind the industry's characters and realities.
Hacking Your Cybersecurity Career
Learn techniques to break into cybersecurity, including visualizing goals, social engineering, active learning, and skill sharpening. Discover traits of successful professionals and navigate the career triad for optimal job prospects.
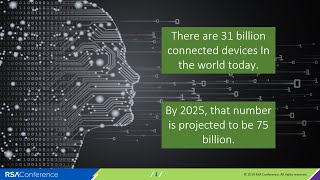
Where Law and Tech Will Collide in 2020
Experts discuss potential friction between technology and privacy laws in 2020, focusing on consumer data protection, privacy by design requirements, and the impact of disruptive technologies.
How to Create a Truly Diverse Cyber-Workforce
Explore strategies to increase diversity in cybersecurity, addressing challenges faced by women and minorities, and understanding the importance of diverse perspectives in combating cybercrime.
Are Spoof-Proof Biometrics Really Possible?
Explore biometric security challenges, spoof attack detection, and best practices for implementing secure, privacy-respecting biometric systems with expert Dr. Stephanie Schuckers.
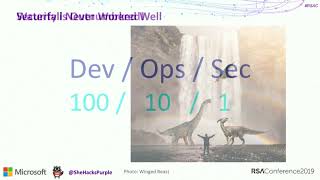
Security Learns to Sprint - DevSecOps
Explore how DevOps can revolutionize application security by integrating it into daily development and operations workflows, enabling faster and more secure software delivery.
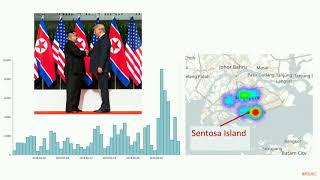
Election Hacking - Trading Malware for Votes
Explore the intersection of cybersecurity and elections, analyzing malware patterns during national polls. Gain insights into strategic traffic analysis and geopolitical correlations for enhanced network security.
Measuring Cybersecurity Effectiveness in a Threat-Based World
Experts discuss leveraging threat data for improved cybersecurity, focusing on DHS, NSA, and NIST initiatives to enhance information protection, detection, and response in government agencies.
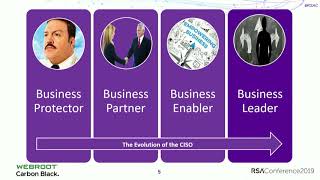
Why the Role of CISO Sucks and What We Should Do to Fix It
Explore challenges faced by CISOs, including stress, career risks, and organizational resistance. Learn strategies to thrive in this evolving role and enhance cybersecurity leadership effectiveness.
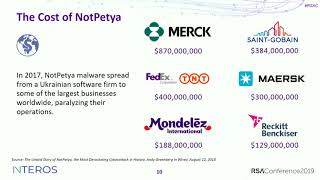
The Power of Ecosystems - A Look Under the Supply-Chain Covers
Explore supply-chain complexities, third-party risks, and nation-state threats in digital ecosystems. Learn to rethink CTI and risk management for today's interconnected business landscape.
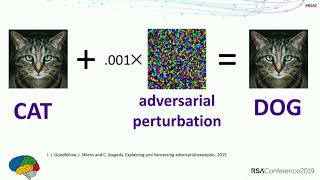
Attacking Machine Learning - On the Security and Privacy of Neural Networks
Explore security vulnerabilities in neural networks, including adversarial examples and data extraction, to understand potential threats and necessary defenses in modern machine learning systems.
Using Automation to Help Achieve Security in a Multicloud Environment
Explore strategies for automating security in multicloud environments, focusing on critical components, tools, and data utilization to enhance operational security and inform decision-makers.

AI - Hacking without Humans - How Can Human Brains Be Hacked?
Explore the security, ethical, and privacy concerns of AI models mimicking human brain functions. Learn about adversarial AI, intelligence sharing, and building strong defenses in cybersecurity.
HTTP Security Headers - A Technology History Through Scar Tissue
Explore HTTP security headers, their evolution, and best practices. Learn to leverage browser-built security controls, with a focus on implementing effective content-security-policy for enhanced web application protection.
Collect All the Data - Protect All the Things
Explore blue team strategies for comprehensive data collection, analysis, and correlation using open-source tools and machine learning to enhance continuous monitoring capabilities.
BADPDF - Stealing Windows Credentials via PDF Files
Discover how PDF files can be weaponized to automatically leak Windows NTLM hashes, potentially compromising user credentials without interaction.
The Memory of a Meltdown
Explore Spectre and Meltdown vulnerabilities through hands-on demonstrations, understanding their impact on memory access and learning how to exploit them using proof-of-concept techniques.
What We Can Learn from Google's Fight with Phishing
Insights from Google's research on phishing attacks, including prevalence, impact, and effective mitigation strategies. Explores prevention methods and provides customized recommendations for different user environments.
Lessons Learned Implementing Meaningful Access Controls to Customer Data
Insights on implementing robust access controls for customer data, reducing internal access by 70% through improved tooling, processes, and automation at Intercom.
Keep it Like a Secret - When Android Apps Contain Private Keys
Análisis de seguridad en apps Android: descubrimiento de miles de claves privadas expuestas, técnicas de craqueo de contraseñas y potenciales riesgos asociados.