Managing the Assets of Your Security Career
Strategies for career growth in cybersecurity: improving influence, visibility, and promotion chances through effective stakeholder management and asset tracking techniques.
How to 10X Your Company's Security - Without a Series D
Discover actionable strategies to dramatically enhance your company's security posture without significant financial investment. Learn from distilled insights and lessons from DevSecOps and modern AppSec experts.
2FA in 2020 and Beyond
Explore the modern 2FA landscape with data-driven analysis, comparing security strength and user experience of various authentication methods like SMS, soft tokens, push, and WebAuthn.
How to Write Like It's Your Job
Practical advice for security professionals on improving technical writing skills, from starting to finishing, with tools and tips for presenting professional work.
Privacy Nightmares while Using ML - AI in Your Applications
Explore privacy challenges in ML/AI applications and learn about a framework that integrates data security with machine learning technologies to address potential nightmares.
MOSE - Using Configuration Management for Evil
Explore MOSE, a post-exploitation tool for leveraging configuration management servers to compromise associated agents en masse, simplifying large-scale system takeovers.
K-Rail - A Tool to Manage K8s Securely at Speed
Explore offensive and defensive scenarios in Kubernetes security, and learn about k-rail, a tool for mitigating risks and managing configurations securely at scale.
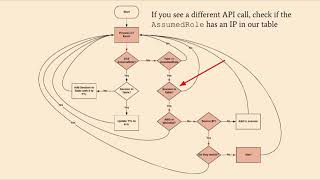
DevSecOps State of the Union
Comprehensive overview of DevSecOps best practices, tools, and methodologies. Distills insights from industry leaders to help AppSec teams improve security integration, automation, and culture.
Ethical Hacking - DIY Mobile Security Workstation for Cheap
Learn to build a cost-effective mobile security workstation using affordable parts and open-source software. Discover how to create a powerful system capable of running Kali Linux or Parrot OS for ethical hacking and network testing.
Implementing a Kick-Butt Training Program - Blue Team Go
Discover a framework for building a robust cybersecurity training program that empowers analysts with hands-on skills in incident response, forensics, and threat hunting.
Treat the Problems, Not the Symptoms
Explore alternative approaches to Active Directory security, focusing on actionable steps for complex multi-domain environments beyond traditional defensive products.
Journey to Command Injection - Hacking the Lenovo ix4-300d
Demonstration of chaining vulnerabilities to remotely exploit a Lenovo NAS device, showcasing command injection, XSS, and CSRF techniques for full system compromise.
Shall We Play a Game?
Develop effective security exercises using MITRE ATT&CK framework. Learn to create, run, and score drills that turn threat intelligence into practiced action for improved incident response.
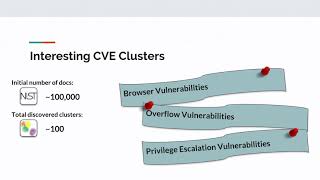
Making Sense of Unstructured Threat Data
Explore how Natural Language Processing and Word2Vec can organize unstructured cybersecurity intelligence, making it actionable by mapping to frameworks like MITRE ATT&CK.
Securing Online Identities with Simple, Secure, Open Standards
Explore the evolution of online identity security, from U2F to FIDO2, and learn how open standards are shaping the future of passwordless authentication across devices.
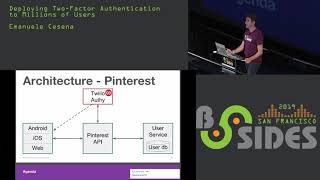
Deploying Two-Factor Authentication to Millions of Users
Comprehensive guide on implementing two-factor authentication for large-scale websites, covering design, architecture, and various methods like TOTP, push notifications, and FIDO security keys.
How to Build an Application Security Program
Practical insights on creating and improving application security programs, drawing from 20 years of experience across various sectors. Covers successful strategies and pitfalls to avoid.
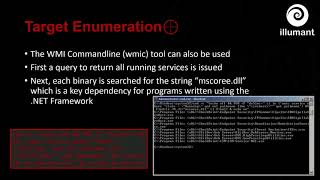
Abusing WCF Endpoint for RCE and Privilege Escalation
Explore WCF vulnerabilities in .NET programs, focusing on privilege escalation and remote code execution. Learn to identify and exploit these bugs through a real-world case study.
Lyft Cartography - Automating Security Visibility and Democratization
Explore Lyft's open-source security intelligence platform for asset tracking, relationship mapping, and automated decision-making. Learn how it improves visibility and empowers teams to enhance security posture.
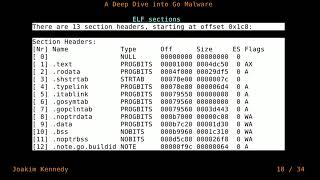
A Deep Dive into Go Malware - Using Metadata to Empower the Analyst
Explore Go malware's unique characteristics, metadata analysis techniques, and insights into malware authorship through examination of stripped Go binaries and their structural elements.
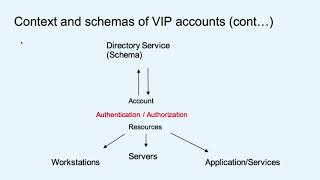
Profiling VIP Accounts Access Patterns in User-Centric Data Streams
Innovative real-time analysis technique for detecting compromised privileged accounts using Kafka streaming, enabling scalable, per-account risk assessment and evolving individual risk profiles.