Dangling Resources Abuse on Cloud Platforms - Identifying and Analyzing Real-Life Hijacks
Unveils real-life cloud resource hijacks, revealing unexpected attacker strategies and developing novel detection methods. Analyzes 20,904 hijacked resources, exposing prevalent abuse tactics and attacker infrastructures.
Spring Security Architecture Principles - 2024
Explore Spring Security's core architecture, building blocks, and customization techniques through diagrams and live coding. Gain practical insights for implementing robust security in your applications.

OAuth, OpenID Connect and .NET - The Good Parts
Explore OAuth and OpenID Connect essentials for .NET developers, focusing on key protocol flows, extensions, and recommended practices for implementing token-based security in modern applications.
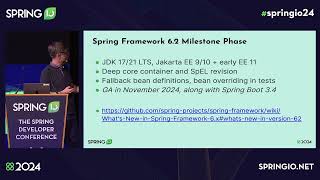
Spring Framework 2024 Keynote
Explore the latest innovations and future directions of the Spring Framework in this comprehensive keynote from the Spring I/O 2024 conference in Barcelona.
A Passwordless Future - Passkeys for Spring Developers
Explore passkeys for enhanced security in Java applications. Learn core concepts, architecture, and implementation using WebAuthn libraries and Spring Security, with step-by-step demos.
The Anatomy of Cloud Attacks
Uncover cloud attackers' tactics and mindsets through honeypot analysis. Learn key defense strategies against threats like Headcrab Kinsing and Teamtnt in this insightful session on cloud security.
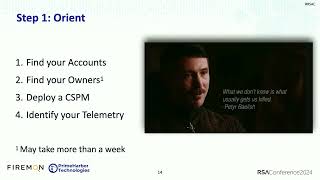
CloudSec Hero to Zero - Building Efficient and Sustainable Cloud Security Programs
Learn proven techniques for triaging and remediating cloud security issues, and build an efficient, sustainable program to tackle thousands of unprioritized findings and inadequate infrastructure.
OAuth Secret: Advanced Exploitation Techniques - NahamCon 2024
Explore advanced OAuth exploitation techniques beyond simple redirect_uri attacks. Learn to chain multiple vulnerabilities for successful account takeovers in modern web applications.
All You Need Is Guest - Securing EntraID Guest Accounts
Explore how EntraID guest accounts can pose security risks, bypass limitations, and gain unauthorized access to corporate resources. Learn steps to harden configurations and prevent attacks.
Fuzz Faster with Turbo Intruder - Account Bruteforcing and MFA Bypass
Learn to use Turbo Intruder for efficient fuzzing, including account bruteforcing and bypassing MFA timers. Hands-on lab exercises demonstrate practical application of this powerful security testing tool.
JavaScript Files Are Your Friends in Bug Bounty Hunting
Discover hidden endpoints and vulnerabilities by diving deep into JavaScript files. Learn techniques to uncover potential bugs and enhance your bug bounty hunting skills.
Cookie Infrastructure at Meta - Managing Consent and Compliance
Explore Meta's cookie management system, featuring a central schema, enforced API, and Content-Security-Policy headers for robust control and compliance with user preferences.
Everything New in Spring Security 6 Baked With a Spring Boot 3 Recipe
Explore the latest advancements in Spring Security 6, including OAuth 2 and OpenID Connect. Learn hands-on techniques for upgrading Spring applications and implementing robust security measures in Java development.
Mobile Application Security: Preventing Credential Leaks - How Millions of Secrets Are Exposed
Explore mobile app security vulnerabilities, focusing on leaked credentials in source code and compiled apps. Learn about common secret types, leak sources, and prevention strategies.
Exposed PII in Public RDS Snapshots - Risks and Remediation
Discover how public RDS snapshots can accidentally expose sensitive data and PII. Learn to prevent, detect, and remediate risks associated with this Amazon service feature.
Cloud Computing Security - Risks and Mitigation Strategies
Explore cloud computing security risks and mitigation strategies, covering topics like data loss, virtualization, compliance, and encryption in emerging large-scale web application deployments.
CSRF Prevention in PHP Using ChatGPT - Part 2
Learn to implement robust CSRF protection in PHP with guidance from ChatGPT, enhancing web application security and preventing potential vulnerabilities.
Offline Apps: The Future of the Web is the Client - Part 2
Explore offline web applications and their potential to revolutionize client-side development, enhancing user experience and functionality in web technologies.
Apps Are the New Edge - Mobile, Edge and Cloud
Explore the evolving landscape of app deployment across mobile, edge, and cloud environments, examining their impact on modern technology infrastructure and development practices.
Becoming Cloud-Native: Shifting Data Management for Application Development
Explore cloud-native databases, their benefits, and how to choose the right one for your workload. Learn to apply cloud-native principles to the data layer for better application development.
4 CI Security Best Practices to Prevent Cloud-Native Supply Chain Attacks
Explore security challenges in CI pipelines and learn best practices to prevent cloud-native supply chain attacks. Discover tips for securing GitHub Actions, GitLab Runner, and CircleCI workflows.