Deconstructing Control Plane Compromise Attacks in Cloud Environments
Explore cloud control plane compromise attacks, learn how hackers exploit architectural flaws, and discover strategies for identifying and mitigating risks in your cloud environment.
Responding to Threats in AWS Linux and Kubernetes Environments
Explore real-life attack techniques in AWS Linux and Kubernetes environments and learn efficient cloud incident response strategies through automation and enhanced visibility.
Development Best Practices - An Overview of Working in the Software World
Explore essential software development practices, from version control to continuous integration, enhancing your skills for efficient and secure coding in the modern tech landscape.
Linux on Mars and Software Supply Chain Security - OSS Keynotes Day 3
Explore Mars exploration, open source insights, and software supply chain security with NASA, Microsoft, and Linux Foundation experts in this keynote series.
The OSPO as a Construct for Global Change
Explore how Open Source Program Offices drive global innovation, from government initiatives to community projects, and their potential for widespread positive impact.
The First Year of the Confidential Computing Consortium
Explore the Confidential Computing Consortium's first year, its impact on open source, and the evolution of software industry partnerships and nonprofit culture.
Keylime: Securing Your Slice of the Cloud
Explore scalable cloud trust attestation with Keylime, leveraging TPM technology for secure identity bootstrapping and system integrity monitoring in untrusted remote infrastructures.
The Latest Research on Cloud Expansion and Security During COVID-19
Explore strategies for successful cloud expansion and security during COVID-19, based on research from Palo Alto Networks. Learn from real-world examples and gain insights for your organization's cloud projects.
Hybrid Cloud Data Management Across Heterogeneous Storages
Explore strategies for managing data across diverse storage systems in hybrid cloud environments, focusing on challenges, solutions, and best practices for seamless integration and optimization.
Open Source Security and Supply Chain Innovations - Keynote Sessions
Explore cutting-edge topics in open source security, including supply chain protection, Sigstore, SPDX, eBPF, SLSA, and memory safety, presented by industry leaders and experts.
Re-Interpreting Open Source in a World of Closing Computing - Keynote
Zeynep Tufekci explores the evolving concept of open source in a world of increasingly closed computing systems, examining its implications for technology, society, and digital freedoms.

PHP and JSON Web Token (JWT) Integration Tutorial
Learn to integrate JSON Web Tokens (JWTs) into PHP APIs using PSR 15 middleware. Demystify JWTs and enhance API security with practical implementation guidance.
A Platform-Agnostic Approach to Securing Workloads
Explore a standardized approach to securing diverse workloads using SPIRE and Envoy, creating a zero-trust foundation with mutual authentication between microservices.
Applying User-Centered Design Techniques for Augmenting Human Perception in Cyber Warfare
Explore user-centered design in cybersecurity, focusing on visualization techniques, cognitive barriers, and gamification to enhance human perception in cyber warfare.
Identifying Your Web Attack Surface - RAWR
Learn to identify and assess web application vulnerabilities using the RAWR methodology, enhancing your ability to secure online systems and protect against potential threats.
OAuth 2.0 - It's the Implementation, Stupid
Explore OAuth 2.0 implementation, covering key concepts, grant types, and security considerations for robust authentication and authorization in web applications.
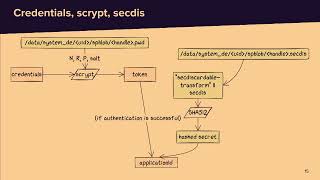
Dissecting the Modern Android Data Encryption Scheme
Explore Android data encryption, focusing on key generation, storage, and vulnerabilities. Learn about File-Based Encryption, TEE, Secure Element, and attack strategies using software vulnerabilities on Samsung A22 and Pixel 3a.
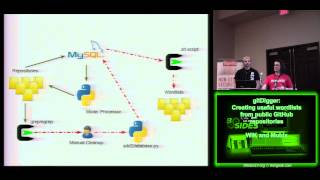
GitDigger: Creating Useful Wordlists from Public GitHub Repositories
Explore gitDigger: Create effective wordlists from GitHub repos for security testing. Learn techniques for mining, parsing, and leveraging public code repositories.

Discovering Dark Matter - Towards Better Android Malware Heuristics
Explore advanced Android malware detection techniques and heuristics to uncover hidden threats in mobile applications, enhancing cybersecurity practices for the Android ecosystem.
Applications, Cloud, and Hackers - Security Challenges in Modern Computing - Lecture 1
Explore cloud application security challenges and solutions in this talk, covering threat landscapes, attack vectors, and defensive strategies for modern cloud environments.
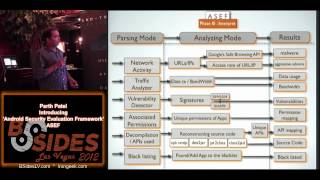
Introducing Android Security Evaluation Framework (ASEF)
Explore ASEF, a framework for evaluating Android app security. Learn about its features, implementation, and how it can enhance mobile app protection and vulnerability detection.