Cloud Native Supply Chain Security: Beyond SBOMs - Perspectives and Practices
Insights on cloud native supply chain security beyond SBOMs. Experts discuss straightforward approaches, simple security practices, and future perspectives using open-source tools and frameworks.
Bringing SPIFFE to Linkerd for Mesh Expansion
Explore how Linkerd integrates SPIFFE/SPIRE to extend service mesh identity beyond Kubernetes, enabling seamless workload integration and mesh expansion.
Confidential Containers for GPU Compute - Incorporating LLMs in AI Lift-and-Shift Strategy
Explore confidential containers for GPU-accelerated AI, integrating LLMs and Kubernetes for secure, high-performance computing while maintaining data privacy in cloud-native environments.
The Rustvolution: How Rust Is the Future of Cloud Native
Explore how Rust addresses critical challenges in modern distributed systems, offering memory safety, fearless concurrency, and zero-cost abstractions for the future of cloud native development.
IAM Confused: Analyzing 8 Identity Breach Incidents
Dissection of 8 real cloud breaches exploiting insecure identities, revealing insights and mitigation strategies for better identity and access management in cloud environments.
How to Implement Biometric Authentication in Your Android App
Implement secure biometric authentication in Android apps using step-by-step guidance. Learn to enhance user experience and protect sensitive data with fingerprint or face recognition.
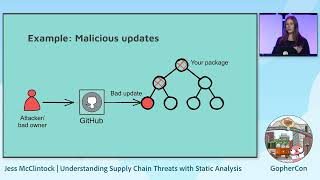
Understanding Supply Chain Threats with Static Analysis - GopherCon 2023
Explore a CLI tool for Go that detects privileged permissions in package dependencies, enhancing security and preventing supply chain attacks.
Java 17 to 21: A Showcase of JDK Security Enhancements
Explore JDK security advancements from Java 17 to 21, covering cryptographic algorithms, configuration, API improvements, and Java Flight Recorder's role in enhancing software security.
Maximizing Security with JDK - Understanding Built-in Capabilities
Explore JDK's native security features, including cryptography and post-quantum enhancements, to simplify development and strengthen application security through live coding demonstrations.
Patching Your Way to Compliance with a Small Team and Technical Debt
Learn strategies to overcome system patching challenges with limited resources, focusing on breaking the cycle of technical debt and meeting security compliance requirements.
Beyond Kubernetes with Linkerd 2.15 and SPIFFE
Explore Linkerd 2.15 and SPIFFE for advanced Kubernetes networking, security, and identity management in cloud-native environments.
Cloudy With a Chance of Security
Explore cloud security challenges and best practices with expert insights on protecting data, managing access, and mitigating risks in modern cloud environments.
XS Leaks - Client-Side Attacks in a Post-XSS World
Explore advanced client-side attacks beyond XSS, focusing on XS Leaks. Learn innovative techniques for exploiting web vulnerabilities and enhancing your security expertise.
Breaking the Cloud - A Tale of Three Breaches
Explore three real-world cloud security breaches, analyzing attack vectors, vulnerabilities, and lessons learned to enhance your organization's cloud defenses and incident response strategies.
Bugs Are Shallow - Finding Vulnerabilities in Top GitHub Projects
Explore techniques for identifying vulnerabilities in popular open-source projects on GitHub, enhancing your security research skills and contributing to safer software.
NoSQL Injection Tutorial Using PortSwigger - With Labs
Learn MongoDB basics and NoSQL authentication bypass techniques using PortSwigger labs. Enhance your cybersecurity skills with practical examples and expert guidance.
Sandboxing Wasm Programs - Syscall Isolation Techniques for Edge Computing
Explore Wasm runtime sandboxing techniques, including SELinux, cgroups, and seccomp. Learn about Callander, a novel syscall sandboxing tool, to enhance security in edge computing platforms.
Auth and RBAC in Multi-Tenant React Apps
Implement user authentication and role-based access control in multi-tenant React applications using Stytch's pre-built UI components and Express.js.
A Tale of Three Service Meshes
Explore the evolution and comparison of three prominent service mesh technologies, highlighting their unique features and use cases in cloud-native environments.

Safety, Security, and C/C++ Evolution - Keynote ACCU 2024
Explore C++ evolution, safety, and security with Herb Sutter. Gain insights on tool adaptation, language distinctions, and future improvements in C and C++ programming.
The Future of Cookies
Explore the evolving landscape of web cookies, their impact on privacy, and recent browser changes affecting their functionality. Learn about challenges and future trends in cookie usage.