Cybersecurity Career Ambassadors - A NIST NICE Community of Interest
Discover NIST's NICE Cybersecurity Career Ambassadors program. Learn how to educate and mentor the next generation of cybersecurity professionals, fostering a diverse and inclusive workforce.
EDR Internals for macOS and Linux - Telemetry Sources and Evasion Techniques
Explore EDR telemetry sources for macOS and Linux, comparing them to Windows equivalents. Gain insights into process monitoring, authentication, networking, and file activity detection techniques.
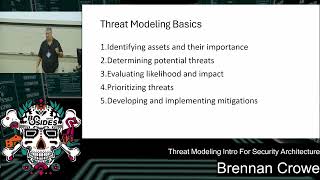
Threat Modeling Introduction for Security Architecture
Aprende a integrar el modelado de amenazas en revisiones anuales de gobernanza y arquitectura de seguridad. Explora conceptos clave como vectores de ataque, superficies de ataque y ciclos de vida de ataques.
Start Early, Stay Safe: The Crucial Role of Cyber in Education
Explore strategies for integrating cyber safety education in schools and homes through interactive methods. Equip educators, parents, and children with tools to navigate the digital world securely.
The Digital Trust Journey: From Key Generation to Signed Certificate
Explore the creation process of digital certificates, from key generation to CA signing. Understand the critical steps ensuring trust and security in online interactions.
Mapping Your External Attack Surface: Illuminating Hidden Vulnerabilities
Illuminate hidden assets and vulnerabilities in your external attack surface using powerful reconnaissance tools. Proactively defend your digital perimeter and stay ahead of potential threats.
The Fault in Our Metrics: Rethinking How We Measure Detection and Response
Rethink detection and response metrics with a practical framework, new maturity model, and visual examples. Learn to measure capabilities effectively and tell a compelling story using micro-purple testing techniques.
Building a DeGoogled, Privacy-Friendly, and Open Source Mobile Ecosystem - The Story Behind /e/OS
Discover the journey behind /e/OS, a privacy-focused, open-source mobile ecosystem designed to be free from Google's influence.
DCMS' Approach to Software Security and Resilience Policy
Explore DCMS' approach to software security and resilience policy with insights from Naomi Gilbert, Head of Cyber Resilience Policy at the Department of Culture Media & Sport.
The Iceberg - How to Mitigate Risks in Your OSS Projects
Explore strategies to mitigate risks in open-source software projects and understand the expanding attack surface in modern development environments.
Open Source Supply Chain Security for Enterprises
Explore enterprise-level open source supply chain security strategies with insights from JPMorgan Chase's Product Security Director.
Breaking Barriers: The Art of Gamified Security Training
Explore gamified security training techniques to enhance cybersecurity skills effectively and affordably, breaking barriers in traditional learning approaches.
The Need for Software Bills of Materials (SBOMs) - Why You Should Disclose Your Software Usage
Explore the importance of Software Bills of Materials (SBOMs) in modern software development and understand their role in enhancing transparency and security.
The Myriad Paths to Improving Open Source Security
Explore diverse approaches to enhance open source security with expert insights from Rory McCune at SOOCon23 Security.
Do You Know the Health of Your OSS Dependencies? Introducing OSSF Scorecard API
Explore the OSSF Scorecard API to assess and improve the health of your open-source software dependencies, enhancing overall security.
Modelling Threats Out in the Open Source - SOOCon23 Security
Explore open-source threat modeling techniques to enhance software security and identify potential vulnerabilities in your projects.
Regulation by Telemetry - How to Fix OS Security by 2030
Explore strategies to enhance OS security through telemetry-based regulation, aiming for improved cybersecurity measures by 2030.
Diversity in Open Source and Cybersecurity - We All Play a Role
Explore the crucial role of diversity in open source and cybersecurity, and learn how everyone can contribute to creating a more inclusive tech environment.
openCRE.org - A Cloud of Knowledge
Explore openCRE.org, a knowledge cloud for cybersecurity, presented by Spyros Gasteratos at SOOCon23 Security.
Manage Open Source, Security and SBOMs for Software Projects and Organizations
Learn to effectively manage open source, enhance security, and implement SBOMs for software projects and organizations.
OWASP LLM Top 10 - Understanding Critical Security Risks for Large Language Models
Explore OWASP LLM Top 10: Gain insights into critical security risks, learn practical steps to fortify applications, and stay ahead in cybersecurity with expert R Nagarjun.