Supply Chain Attacks - Focusing on NPM Vulnerabilities and Defenses
Explore NPM ecosystem vulnerabilities, learn to identify and protect against supply chain attacks, and discover strategies to fortify open-source software security.
Weaving Application Security's Scale - Enabling Business Through Partnerships
Explore AppSec's growth journey and learn how to scale security across organizations by fostering partnerships and enabling wider business objectives.
Misconception About the Security of Open Source Software - Study Case: Ubuntu Linux and LibreOffice
Explore common misconceptions about open-source software security, focusing on Ubuntu Linux and LibreOffice as case studies.

Improving FOSS Security
Explore Canonical's security maintenance process and learn strategies for FOSS projects to enhance vulnerability management and disclosure.
You Wouldn't Hack a Car? A Pentester's Approach to Embedded Security on Automotive ECUs
Explore automotive security testing of electronic control units, focusing on embedded systems in modern vehicles and their vulnerabilities. Learn pentesting approaches for ECU analysis and defense mechanisms.
Secure Firmware Updates Over the Air - RIOT Summit 2024
Explore secure firmware updates over-the-air, including encryption implementation for SUIT example in RIOT. Includes overview, demo, and insights from IoT security experts.
Lightweight Remote Attestation over EDHOC for Constrained IoT Devices
Explore efficient remote attestation for IoT devices using EDHOC protocol. Learn about parallel network authentication and integrity verification for constrained environments like RIOT OS.
Is Remote Attestation Relevant for Embedded Devices? - RIOT Summit 2024
Explore remote attestation's relevance for embedded devices, examining latest developments, challenges, and potential benefits in the context of Trusted Execution Environments and RIOT OS.
What's Next for Security Professionals - Innovations in Threat Prevention and AI-Driven Security
Explore the convergence of security capabilities, AI-driven innovations, and insights from industry leaders to transform your organization's security approach.
ARP Spoofing and Poisoning: Understanding Man-in-the-Middle Attacks - Demo
Explore ARP spoofing: its mechanics, targets, consequences, and prevention. Learn to safeguard your network against this malicious technique that disrupts communication and intercepts data.
Metasploit Auxiliary Modules Demo - TCP Port Scanners, FTP Login, SSH Version, and SSH Login
Explore Metasploit Auxiliary modules, including TCP port scanners, FTP login, and SSH tools. Learn practical techniques for network reconnaissance and vulnerability assessment.
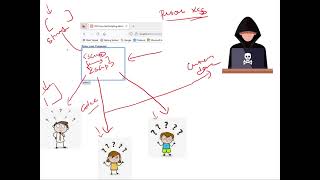
Persistent XSS (Cross-Site Scripting) Attack: What It Is and How to Prevent It
Explore persistent XSS attacks, witness a live demo, and learn effective prevention strategies to enhance web application security.

Ethical Hacking: Using Metasploit to Crack Passwords
Explore ethical password cracking using Metasploit. Learn to create dictionaries, launch attacks, and understand techniques for responsible penetration testing and system security enhancement.
Nikto Web Vulnerability Scanner - Web Penetration Testing
Learn to identify web vulnerabilities using Nikto, an open-source scanner. Explore its features and enhance your web application security skills.
Metasploit Framework Introduction - Modules in Metasploit
Explore Metasploit's core modules: Auxiliary, Exploit, Payload, Encoder, Evasion, and Post-Exploitation. Learn their functions and applications in penetration testing.
Social Engineering Attack Using Mass Mailer in Kali Linux - Demo
Discover how to execute a mass mailing attack using Kali Linux's setoolkit, exploring social engineering techniques for educational purposes.
Corstone-1000: Secure IoT SoC Design with Yocto Project
Explore Arm Corstone-1000's secure IoT SoC design using Yocto Project. Learn about flexible reference packages, built-in security, and support for platform operating systems like Linux.
CVE Triage, CVE Checker Analysis, and Vendor PR in Yocto Project Security - YPS 2023.11
Explore CVE triage initiatives, SRTool enhancements for CVE Checker analysis, and potential "vendor_pr" system to address package patching recognition in Yocto Project security.
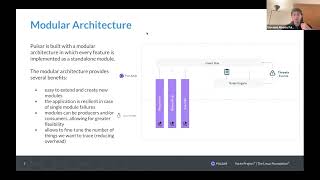
Embedded Runtime Security with Pulsar - YPS 2023.11
Explore Pulsar, an eBPF-powered threat detection system for IoT. Learn its architecture, capabilities, and integration with Yocto Project for enhanced embedded system security.
Yocto Project Security: Now and the Future - YPS 2023.11
Explore Yocto Project's 2023 security updates and upcoming 2024 features, including CVE scanning, SBOM generation, and default options.
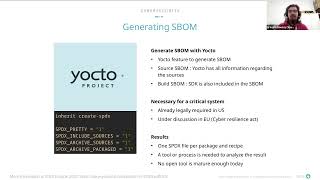
The LF Energy Seapath Project: Yocto Applications in Power Grid Automation
Explore SEAPATH, an open-source platform for power grid substation automation. Learn about its development, transition to virtualization, and the role of Yocto in cybersecurity, SBOM, CI/CD, and licensing.