Impacket Tools for Pentesting Secure Environments - 02-11-2023
Explore advanced pentesting techniques for secure environments using Responder, CrackMapExec, and Impacket utilities. Enhance your cybersecurity skills.
The Depth of Cyber Hygiene: Eliminating Reactive Approaches
Explore layers of cybersecurity, from solutions to human elements. Interact with attendees, review recent cyberattacks, and learn prevention strategies from an experienced expert.
Breaching the Depths of the Abyss: Exposing Rootkits - Track 2, Session 4
Dive deep into rootkits: explore their inner workings, detection techniques, and countermeasures. Learn to identify and neutralize these stealthy threats using advanced tools like Living Off The Land Drivers.
Building a Canarytoken to Monitor Windows Process Execution - Track 2
Explore building Canarytokens to monitor Windows process execution, creating alerts for unexpected commands and strengthening defense against potential attacks.
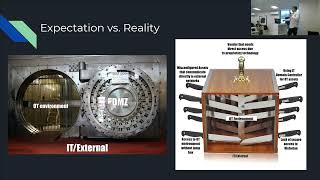
The Things I Wish I Learned Before Starting in ICS Security - Track 1
Explore fundamental concepts of ICS security, including SCADA, DCS, controllers, and OT architecture. Bridge the knowledge gap for IT professionals transitioning to critical infrastructure protection.
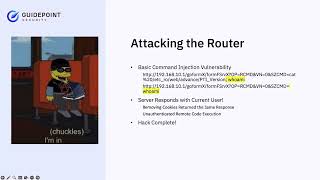
The Route to Success: Hacking a Router to Its End of Life
Explore the process of hacking a Trendnet travel router, from vulnerability hunting to exploit development. Learn methodologies and tools for both newcomers and veterans in IoT security.
Hunting File System Redirection Bugs Through Instrumentation
Explore file system redirection vulnerabilities and learn advanced techniques for identifying and exploiting these security risks in Windows systems.
Detection as Code - Buzzword or Panacea?
Explore the reality of Detection-as-Code in cybersecurity. Separate hype from facts and understand its potential benefits for blue teams and threat detection programs.
How Hacking Works - Web Edition - NDC Oslo 2024
Explore web exploitation techniques and tools to enhance software security through gamified environments. Learn to think like a hacker for safer development.
Advancing DevSecOps Metrics - Creating a Clear Path to Improved Performance
Integrate a clear path to improved performance by advancing DevSecOps metrics. Learn to deconstruct core metrics for accelerated delivery and increased customer value.
Writing Powerful Penetration Testing Reports
Learn strategies for crafting effective penetration testing reports, including key components, proof-of-concept creation, and common pitfalls to avoid. Enhance your ability to deliver impactful security assessments.
Protecting Small Businesses from Cyber Attacks - Strategies and Real-World Scenarios
Explore attacker strategies, real-world scenarios, and cost-effective measures to protect small businesses from cyber threats. Learn to engage employees through gamification for enhanced security.
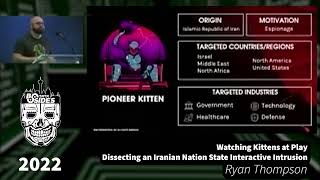
Dissecting an Iranian Nation State Interactive Intrusion - Watching Kittens at Play
Dissect an Iranian nation-state intrusion, gaining insights into adversarial tactics. Learn threat hunting techniques to uncover and counter sophisticated cyber attacks in your environment.
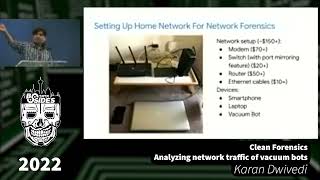
Clean Forensics: Analyzing Network Traffic of Vacuum Bots - Lecture
Explore network forensics of vacuum bots, uncovering security and privacy concerns. Learn step-by-step analysis of bot communication, authentication protocols, and potential vulnerabilities in smart home devices.
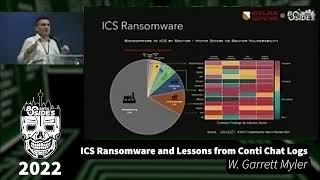
ICS Ransomware and Lessons from Conti Chat Logs
Explore ICS ransomware threats, analyze Conti chat logs, and gain insights into critical infrastructure vulnerabilities. Learn from a cybersecurity expert's perspective on assessing and mitigating cyber risks.
Why You Can Still Get Hacked Even After Signing Your Software Artifacts
Explore artifact poisoning tactics in software supply chains and learn prevention methods, including secure artifact signing, to protect your CI/CD pipeline from malicious injections.
Defense in Depth: Refocusing on Defensive Security Techniques
Explore defensive product security techniques, emphasizing defense-in-depth and supply chain security. Learn key aspects to consider in your application security strategy.
Securing Software Supply Chains Using the SLSA Framework
Implement SLSA framework to secure software supply chains. Learn practical, vendor-neutral examples for code, build process, provenance, and deployment to create a resilient software development lifecycle.
Cyber Attack - Learn Your Lesson from Recent Security Breaches
Explore hacker tactics and analyze a major recent attack case study to enhance your understanding of cybersecurity threats and defense strategies.
Access Control Done Right the First Time
Master physical access control systems with expert tips on secure installation, reliable operation, and tamper-resistant design. Learn best practices for wiring, badge selection, controller security, and ongoing maintenance.
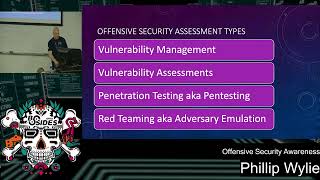
Offensive Security Awareness: Understanding Assessment Types and Methodologies
Demystify offensive security techniques, tools, and assessment types. Gain insights into vulnerability management strategies and learn to choose the right approach for your organization's security needs.