Connecting the Dots: How Threat Intelligence Protects Applications
Explore Cyber Threat Intelligence integration in AppSec programs, automating data collection, and leveraging IoCs and TTPs to prevent and mitigate cyber attacks in today's digital business landscape.
OWASP Top 10 Privacy Risks 2021 - Understanding and Mitigating Web Application Privacy Threats
Explore OWASP's updated Top 10 Privacy Risks for web applications, covering vulnerabilities, consent issues, and data quality. Learn countermeasures to build a more private digital future.
What Shall We Do With a Vendor SBOM? - Understanding Software Bill of Materials
Explore the practical applications of Software Bill of Materials (SBOM) in cybersecurity, covering procurement, vulnerability disclosure, threat intelligence, and forensics.
Modern XSS Defense Strategies - Frameworks, CSP, and Sanitization
Explore modern XSS defense strategies, including JavaScript frameworks, CSP deployment, HTML sanitization, and design considerations for building secure web applications against evolving threats.
Time Lock Puzzles for Good and Evil
Explore timelock puzzles in cybersecurity: their history, offensive and defensive applications, novel constructions, weaponization techniques, detection methods, and challenges in both malicious and benign use cases.
Secure Messengers and Man in the Contacts Attack
Explore the Man in the Contacts attack, its implementation in a mobile game, and its potential for spear phishing in secure messaging apps. Learn about vulnerabilities and possible mitigations.
Scaling Security in Leading Companies - DevOps and CI/CD Best Practices
Discover pro-tips and actionable lessons from mature security teams on scaling security in modern software development. Learn effective strategies for buy-in, engineering projects, analysis integration, and production monitoring.
Don't Feed the Hippos - Improving Security Communication with Developers
Explore common security communication failures and learn effective strategies for collaborating with developers to address software vulnerabilities and enhance overall security practices.
OWASP Serverless Top 10 - Security Risks and Protections
Explore serverless security risks, challenges, and protective measures. Learn about OWASP Serverless Top 10 and DVSA tool for understanding serverless security implications and processes.
Software Security 5D Framework - Evolution of Security Verification
Explore the OWASP Software Security 5D Framework and its impact on integrating security bugs into the software lifecycle, revolutionizing traditional assessment methods.
Secure Coding Lessons for Mobile Apps - Insights from the Trenches
Explore common mobile app coding pitfalls, their real-world impacts, and learn effective strategies to enhance security. Includes demonstrations of attacker techniques and protective code samples.
Trusted Types: End-to-End Injection Safety at Scale
Learn about Google's approach to achieving high-level XSS safety through integrated tools and developer-friendly practices, with insights on implementing similar security in open-source stacks.
Security Culture - Fostering Hackers for Application Security
Explore strategies to foster a security-focused culture among IT professionals, emphasizing knowledge sharing, communication, and developer engagement to enhance application security and overall cybersecurity awareness.
Threat Modeling of Containerized Applications - Three Levels of Complexity
Optimize threat modeling for containerized applications, focusing on efficiency, new dimensions, and real-world impact. Learn to measure success and implement incremental improvements in application security.
Looking Towards the Future of Open Source Vulnerability Management
Explore the evolving landscape of open source security, focusing on vulnerability management strategies, industry trends, and best practices for effective remediation and continuous security integration.
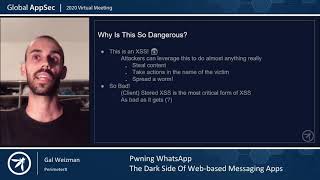
Pwning WhatsApp - The Dark Side of Web-based Messaging Apps
Explore vulnerabilities in web-based messaging apps, focusing on WhatsApp. Learn about potential security risks and exploitation techniques in popular communication platforms.
OWASP Top 10 Maturity Categories for Security Champions
Learn to become an effective Security Champion using OWASP's Top 10 Maturity Categories. Explore key responsibilities, maturity models, and strategies for improving organizational security posture.
Practical Mobile App Attacks By Example
Explore real-world mobile app vulnerabilities and attack techniques through hands-on demonstrations, enhancing your understanding of mobile security risks and defense strategies.
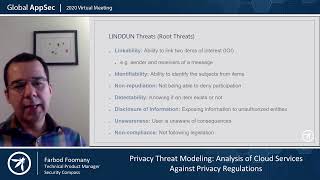
Privacy Threat Modeling - Analysis of Cloud Services Against Privacy Regulations
Learn to analyze cloud services for privacy threats and regulatory compliance using threat modeling techniques, enhancing your ability to protect sensitive data.
America's Online Enemies - Confronting Cybersecurity Threats to Democracy
Explore cybersecurity threats to democracy, infrastructure, and personal data. Learn how government, companies, and individuals can confront state-sponsored and criminal cyber-attacks.
OSINT to Compromise - Techniques for Information Gathering
Explore OSINT techniques for ethical hacking and cybersecurity, learning how to gather and analyze open-source intelligence to identify vulnerabilities and enhance digital defense strategies.