OWASP Distinguished Lifetime Member Award - Jeff Williams' Contributions
Explore Jeff Williams' contributions to OWASP, including foundational projects, non-profit creation, and innovative security concepts, in this insightful 20th anniversary recognition.
OWASP NL Chapter Meeting - SKF News
Learn about the latest developments in OWASP's Security Knowledge Framework (SKF) from experts Riccardo and Glenn ten Cate, enhancing your understanding of web application security best practices.
Virtual AppSec Days Lightning Conference
Explore cutting-edge application security topics with industry experts in this fast-paced, informative conference session from OWASP Foundation.

WebAuthn - Balancing Strong Authentication, Privacy, and Convenience
Explore the balance between robust authentication, user privacy, and ease of use in WebAuthn implementation for enhanced online security.
Does the Internet Need Its Own Geneva Convention? - Cybersecurity and International Governance
Exploring the need for international rules to protect citizens' internet use amid rising cybercrime and cyberattacks, with Microsoft's president advocating for a digital Geneva convention.
Do Certain Types of Developers or Teams Write More Secure Code?
Explore factors influencing secure code development, including team dynamics, developer experience, and human factors. Gain insights into improving software security practices.
Scaling Security through Context-Based Security Assessments
Streamlining security assessments through context-based automation, enabling efficient scaling and tailored workflows for product security teams in rapidly growing organizations.
SBOM SmackDown - Conquering Software Supply Chain Risks with OWASP CycloneDX
Explore Software Bill of Materials (SBOM) and learn how OWASP CycloneDX standard enhances software supply chain transparency, enabling better risk-based decisions and compliance with government mandates.
Practical Threat Modeling for Real-World and Cloud Situations in Hybrid Work Environments
Practical guide to threat modeling for cloud and hybrid work environments, covering creation, identification, addressing, and validation of threats with real-world examples and tools.
Leave It to the Machines - AI and ML in Container Security
Explore how AI and ML empower security teams to proactively secure container-based applications, shifting left security capabilities and streamlining the development process.
Understanding the API Attack Vector - How Attackers Exploit Application Communications
Explore attacker techniques for targeting API-driven applications, including code manipulation, mobile vulnerabilities, and advanced attacks. Learn strategies to secure apps in cloud-native environments.
Normalizing AppSec Issues for Contextual Risk-Based Prioritization at Enterprise Scale
Explore a new approach to Application Security that focuses on critical risks by incorporating contextual intelligence, improving efficiency and delivery in enterprise-scale programs.
Changed Responsibilities in Modern Development Practices
Explore how modern development practices like CI/CD and DevOps impact application security. Learn strategies for integrating security early in the development lifecycle and empowering developers with essential security skills.
Analyzing Google's SLSA Framework for Securing Software Supply Chains
Explore Google's SLSA framework for securing software supply chains, covering key areas, controls, and additional considerations beyond the framework's scope.
OWASP Software Assurance Maturity Model - SAMM
Explore OWASP's Software Assurance Maturity Model (SAMM), a framework for improving software security practices across organizations, presented by expert Bart De Win.
Application Security Verification Standard - OWASP Flagship Project
Comprehensive guide to OWASP's Application Security Verification Standard, covering its history, development, and implementation strategies for robust application security.
OWASP Top 10 - The Making of the OWASP Top 10 and Beyond
Explore the creation process and principles behind the OWASP Top 10, a crucial resource for web application security, including data analysis, likelihood management, and scoring methodologies.
OWASP CycloneDX - Software Bill of Materials Standard
Explore OWASP CycloneDX, a lightweight software bill of materials (SBOM) standard, with experts Steve Springett and Patrick Dwyer. Learn about its features, applications, and importance in modern software development.
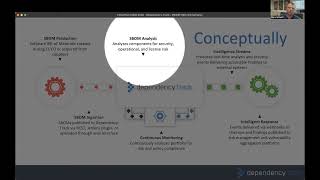
OWASP Dependency Track - Software Composition Analysis and Vulnerability Management
Explore OWASP Dependency Track: manage software components, analyze vulnerabilities, and enhance security with features like Software Bill of Materials, policy engine, and dependency graphs.
OWASP CSRFGuard: Understanding and Preventing Cross-Site Request Forgery
Learn to prevent Cross-Site Request Forgery attacks with OWASP CSRFGuard. Explore real-world examples, detection techniques, and implementation strategies for robust web application security.
Stop the Looters: Method to Detect Digital Skimming Attacks
Discover a method to detect and prevent digital skimming attacks on websites, protecting sensitive customer data from theft by malicious actors like Magecart.