Overwhelmed by Vulnerability Triage - A Blend of Best Practices
Learn effective strategies for managing vulnerability triage, combining industry best practices to streamline your security processes and improve overall risk management.
OD Approach to the Champions Dilemma
Explore an Organizational Development approach to addressing challenges faced by security champions, offering strategies for effective leadership and cultural change.
Learn to Exploit TOCTOU Race Condition Vulnerabilities with OWASP TimeGap Theory
Explore TOCTOU race condition vulnerabilities and learn exploitation techniques using OWASP TimeGap Theory in this comprehensive cybersecurity session.
Measure and Improve Software Supply Chain Assurance with OWASP SCVS
Learn to assess and enhance software supply chain security using OWASP's Software Component Verification Standard (SCVS), improving overall cybersecurity posture.
Blinded by the Weakest Link - A New Perspective on Human Risk in Cybersecurity
Explore a new perspective on human risk in cybersecurity, challenging the "weakest link" mindset and offering innovative strategies to enhance security decision-making and behavior.
Survive Your Nightmare Security Incident and Thrive Again
Learn strategies to effectively manage and recover from major security incidents, enhancing organizational resilience and fostering a culture of continuous improvement in cybersecurity.
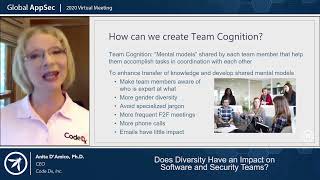
Impact of Diversity on Software and Security Teams
Explore the impact of diversity on software and security teams, examining its influence on team dynamics, problem-solving, and overall effectiveness in the tech industry.
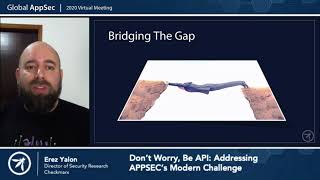
Don't Worry, Be API - Addressing AppSec's Modern Challenge
Explore modern API security challenges and solutions, including OWASP API Security Top 10, authentication issues, and authorization vulnerabilities in this comprehensive overview.
Election Security: The Post-Pandemic Acceleration of Secure Web-Based Voting
Explore election security challenges, lessons from 2016, and advancements in secure web-based voting. Learn about information sharing, auditing, and strategies to protect the integrity of democratic processes.
Security vs. Liberty - Balancing Cybersecurity and Civil Rights in the Digital Age
Debate on balancing security and liberty in cyberspace, exploring encryption, social media's role in terrorism, and government access to digital communications.
Good Bot, Bad Bot: Characterizing Automated Browsing Activity
Explore Aristeus, a system for deploying honeysites to study malicious bot behavior. Learn about bot traffic patterns, attack strategies, and the importance of understanding automated browsing activity for web security.
How to Review Code for Vulnerabilities - OWASP Standard Classification
Learn effective strategies for identifying vulnerabilities through source code review, including key concepts, starting points, and automation techniques. Practice reviewing code samples to enhance your application security skills.
Everything You Always Wanted to Know About Fingerprinting Browser Extensions
Explore browser extension fingerprinting techniques, their implications for user privacy, and current browser defenses. Learn about DOM modifications, stylesheet hijacking, and web-accessible resources.
Threat Modeling the CI/CD Pipeline to Improve Software Supply Chain Security
Explore threat modeling for CI/CD pipelines to enhance software supply chain security, covering key vulnerabilities, data flow analysis, and mitigation strategies.
That Was Then - US-China Relations and Asian Security Challenges
Exploring US-China relations, North Korea threats, South China Sea tensions, and cyber espionage. Experts discuss implications of shifting diplomatic dynamics and potential resolutions to key geopolitical challenges.
Security Chaos Engineering - Turning the Tide in the War on Uncertainty in Cyber Security
Explore security chaos engineering to proactively discover system weaknesses, increase confidence in security mechanisms, and move from subjective assessment to objective measurement through continuous experimentation.
Cyber Risk Success Criteria for Board and Executives - Birds and Buttons Approach
Discover effective strategies for communicating cyber risks to non-technical executives and board members. Learn key success criteria and insights from global CxOs to enhance your cybersecurity leadership skills.

Cyber Intelligence and Security: Distinguishing Signal from Noise
Insights into cyber threats and intelligence challenges from US and UK security leaders, discussing strategies for distinguishing signals from noise in an era of unprecedented digital risks.
DevSecOps in 2031: How Robots and Humans Will Secure Apps Together
Explore the future of DevSecOps in 2031, where humans and robots collaborate to secure applications. Learn about AI pair programming and innovative approaches to tackle evolving cybersecurity challenges.
At the Helm of the Intelligence Community - National Security and Intelligence Challenges
Explore national security events and intelligence challenges with the Director of National Intelligence in a thought-provoking discussion moderated by NBC's Lester Holt.
Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.