The Evolving Community of Application Security
Explore the evolution of Application Security, its growing importance, and the role of the community in addressing future security challenges at scale.
Webhooks Hookups - Abusing API Developers
Explore the security risks of Webhooks in API development, including potential vulnerabilities, real-world examples, and preventive measures. Learn about a new toolkit for auditing Webhook exposure.
Rhyming with Hacks - The Ballad of Supply Chain Attacks
Explore supply chain attacks, their anatomy, and prevention strategies. Learn about real-life examples, existing solutions, and a new DOM monitoring approach with live demonstration.
Hacking Alexa and Cortana: Vulnerabilities in Voice Assistant Partnerships
Explore innovative "Evil Maid" attacks on Windows, vulnerabilities in Cortana-Alexa integration, and the challenges of merging new concepts with existing security mechanisms. Gain insights into AI and IoT security.
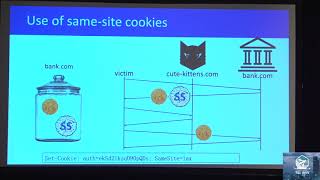
Bypassing Browser Policies and Privacy Extensions for Cookies
Explore bypasses to browser policies and extensions for cookie security. Learn about an automated framework for evaluating countermeasures against cross-site attacks and third-party tracking.
Innovation Fair for Application and Software Security Startups - OWASP Global AppSec Tel Aviv 2019
Explore innovative startups in application and software security at OWASP's first Innovation Fair. Early-stage companies pitch cutting-edge solutions, offering insights into emerging technologies and market trends.
Automated Cyber Security Platform at Scale
Explore the vision and demo of an open-source Automated Security Platform, addressing sophisticated threats through security orchestration and automation to overcome data and process overload.
Software Bill of Materials (S-BoM) - Reducing Risk in Third-Party Components
Explore best practices for managing third-party component risks using software bill-of-materials (S-BoM). Learn to create S-BoMs, identify vulnerabilities, and automate security responses in polyglot environments.
OWASP AppSecCali 2019 Welcome Address - Global Task Force and Innovations
Explore OWASP's global task force, key figures, and innovations in application security at AppSecCali 2019. Gain insights into the organization's global impact and leadership in setting industry standards.
The Art of Vulnerability Management - Transforming Security Collaboration
Transforming vulnerability management from a nuisance to a collaborative process that drives accountability and transparency in software security through decentralization and empowerment.
Securing In-House Execution of Unsafe Third-Party Executables
Explore a framework for securely executing third-party code in production environments, addressing challenges and implementing best practices to mitigate risks associated with untrusted executables.
Securing Third Party Applications at Scale - AppSecCali 2019
Learn best practices for securing third-party applications at scale, including tooling, processes, and manual reviews. Gain insights from Salesforce's experience in reviewing over 4000 AppExchange applications to prevent vulnerabilities.
An Attacker's View of Serverless and GraphQL Apps
Explore attack vectors and security vulnerabilities in serverless and GraphQL applications from a red-team perspective. Learn practical exploitation techniques and defense strategies for modern distributed systems.
Adding Privacy to Threat Modeling - Game On!
Explore how LogMeIn extended the Elevation of Privilege card game to incorporate privacy considerations, bridging knowledge gaps between development, security, and compliance teams through gamification.
Eradicating Vulnerability Classes: Embracing Secure Defaults and Invariants
Explore innovative approaches to application security, focusing on secure defaults and invariants instead of traditional SAST methods to effectively eliminate vulnerability classes.
Falling Water Vulnerability Disclosure for Medical Devices
Explore vulnerability disclosure in medical devices, focusing on the Falling Water approach and its implications for healthcare cybersecurity and patient safety.
How to Break APIs - Security Testing Techniques
Comprehensive guide to identifying and exploiting vulnerabilities in APIs, focusing on practical techniques for security testing and penetration.
A Warrior's Journey - Building a Global AppSec Program
Discover strategies for establishing a robust global application security program, drawing insights from real-world experiences and best practices in the field.
AppSec is Dead - Long Live DevSecOps
Explore the shift from AppSec to DevSecOps, focusing on creating secure code, working smarter, and implementing key pillars for effective security integration in software development.
Creating a Security Policy Framework That Works
Learn to develop an effective security policy framework, covering governance, compliance, and change management for robust organizational cybersecurity.
Who Deserves Cybersecurity? Expanding Our Circle of Care
Eva Galperin explores expanding cybersecurity access for vulnerable populations, drawing on her expertise in privacy, malware research, and advocacy for digital rights and protection worldwide.