Top 10 Security Best Practices for Securing Microservices
Comprehensive guide to securing microservices, covering TLS, authentication, authorization, DDoS protection, monitoring, encryption, and more. Essential for developers and architects building scalable, secure APIs.
Fixing Mobile Application Security - OWASP Mobile Security Testing Guide
Introduction to OWASP Mobile Security Testing Guide and Mobile Application Security Verification Standard, addressing challenges in mobile app security testing and best practices for secure development.
Android Password Manager Security Analysis - AppSec EU 2017
Explore Android password manager security, common vulnerabilities, and best practices for protecting stored secrets. Learn about implementation pitfalls and design failures in popular apps.
Fixing Mobile Application Security - The OWASP Mobile Project
Explore OWASP's Mobile Application Verification Standard and Security Testing Guide, addressing key mobile app security challenges and best practices for secure data storage, communication, and API usage.
NOSQL Web Application Vulnerabilities and Mitigation
Explore NOSQL database vulnerabilities, including injection methods and CSRF, and learn mitigation strategies for enhanced security in web applications.
HTML5 - Security Risks and Tools in Modern Web Applications
Explore HTML5's security implications, from potential risks to innovative tools for enhanced authentication and session tracking. Learn how new features impact web application security.
Scripting Android Applications for Social Botnet Creation - Network Exploitation Techniques
Explore techniques for scripting Android applications, including APK manipulation, API exploitation, and creating realistic social botnets using JRuby sessions and network data.
OWASP PHP Security Project - Securing Web Applications with PHP Libraries and Tools
Explore secure PHP development with OWASP's project, featuring decoupled libraries and tools for enhanced web application security. Learn encryption, password management, and protection against common vulnerabilities.
Enhancing Envoy: Certificate Handling at the Edge
Explore OpenSSL support in Envoy, enabling FIPS 140-2 compliance and improved cryptographic conformance. Learn about SSL/TLS engines and their impact on proxy server security.
Back to the Future - Next-Generation Cloud Native Security
Explore the future of cloud native security, examining emerging technologies, architectural patterns, and potential challenges. Gain insights into next-gen security pipelines and industry advancements.
ZeroTrust Microservices with WebAssembly and WireGuard
Explore zero-trust architectures for cloud computing using WebAssembly and WireGuard. Learn to implement end-to-end encryption and role-based access controls in microservices for enhanced security.
The Secret to Brewing Up a Good API
Learn essential techniques for creating robust, user-friendly APIs, covering documentation, design, typing, pagination, error handling, authentication, and security best practices.
Integrating Rust into Tor - Successes and Challenges
Explore Tor Project's journey integrating Rust: challenges, successes, and lessons learned in enhancing a decade-old C codebase with modern language features.
Securing Norway's Welfare System: Transparent End-to-End Encryption in the Cloud
Explore how Norway's welfare system secures its cloud-based platform, balancing developer convenience, reliability, and security for 1600+ applications on Kubernetes, with focus on transparent end-to-end encryption.
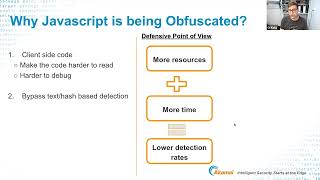
JavaScript Obfuscation: It's All About the Packers
Explore JavaScript obfuscation techniques, focusing on packers and their impact on code security and readability in this informative OWASP presentation.
Don't Mind the Gap - Securely Accessing Cloud Resources with SPIFFE/SPIRE
Explore secure cloud resource access using SPIFFE/SPIRE for identity federation. Learn to access AWS and other services without managing API keys, simplifying cross-cloud interactions.
IPVM Community Call: Progress on Homestar Implementation - November 2023
Explore IPVM's progress on Homestar, a WebAssembly-based system for content-addressed data and PKI, enabling interoperable and secure computation across platforms.
Confidential Computing - Why It Has to Be Cloud and Open
Explore Confidential Computing's role in enhancing data security, reducing supply chains, and protecting sensitive applications. Learn about its implementation across major cloud platforms and the importance of open-source development.
Multi-Scheme Password Hashing Implementation in Rust - Episode 4
Implement multi-scheme password hashing in Rust with HMAC/SHA512 and Argon2, featuring auto-upgrade and static dispatch for enhanced web application security.
The Unbreakable Code Whose Breaking Won World War II - Enigma Machine Emulator in Ruby
Explore the Enigma machine's history and mechanics through an OOP-based Ruby emulator, uncovering WWII code-breaking secrets and drawing parallels to modern development patterns.
Detecting Malicious Dependencies at Scale with Static Analysis
Explore static analysis techniques for identifying malicious dependencies in open-source packages, including Semgrep rules and metadata analysis to enhance software supply chain security.