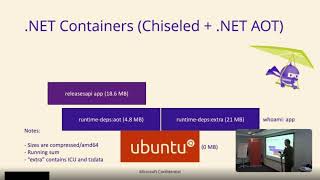
Enhancing Security with .NET on Chiseled Ubuntu Containers
Explore how Microsoft and Canonical enhance security for .NET applications using chiseled Ubuntu containers, improving the software supply chain and enabling confident production deployment.
When Confidential Containers Meet Arm Confidential Computing Architecture
Explore Confidential Containers' integration with Arm CCA, focusing on standardizing confidential computing for Kubernetes and leveraging TEE for enhanced container and data protection.
Confidential Containers: Why, How, and Where Are We?
Explore Confidential Computing's role in enhancing cloud data security. Learn how Confidential Containers democratize this technology, enabling seamless deployment of sensitive workloads with minimal changes.
Cloud Native Application Security with Open Source
Explore cloud native app security risks, identification methods, and open-source tools for risk mitigation in developer-friendly environments. Learn to integrate security into workflows.
The Security Evolution of gRPC Services in the Mesh
Explore the evolution of securing gRPC services in containers and service mesh, focusing on Istio's role in enhancing security posture for east-west traffic without sidecar complexity.
The Ever-Shifting Habits of Cloud-Focused Malware Campaigns
Explore evolving cloud-focused malware campaigns, their diverse objectives beyond cryptojacking, and cloud-specific TTPs. Gain insights into recent trends and the use of cloud services in supporting malware attacks.
Infusing Security Into the Application Development Process
Explore integrating security into software development, covering topics like SBOMs, vulnerability scanning, and supply chain security. Learn practical strategies for secure coding practices.
Java in Containers: Evolution and Best Practices
Explore JVM evolution for containers, best practices for Java workload deployment, and container security insights in this informative session by Oracle's Java Developer Advocate.
Attacking and Defending JWT Tokens - The Ultimate Guide
Comprehensive guide on JWT tokens: basics, vulnerabilities, exploitation techniques, and best practices for securing modern web applications. Includes real-world examples and developer strategies.
Vulnerabilities and Misconfigurations in Cloud-Native Security - Two Sides of the Same Risk Coin
Explore cloud-native security risks, focusing on vulnerabilities and misconfigurations in modern applications. Learn proactive defense strategies for comprehensive protection across entire application stacks.

Deep Dive Into AWS Instance Metadata - NahamCon 2024
Explore AWS instance metadata across EC2, ECS, and EKS, from basics to advanced container scenarios, enhancing your ability to maximize bug impact in cloud environments.
KubeSecRay - Fortifying Multi-Tenant Ray Clusters on Kubernetes
Discover how to secure multi-tenant Ray clusters using KubeSecRay, implementing robust Kubernetes security features for isolation, access control, and resource management in distributed computing environments.
Kubernetes Data Security and Management - Best Practices for State of the Art Protection
Master essential security practices for protecting databases on Kubernetes, from container scanning and encryption to operator-based protection and infrastructure hardening techniques.
Kata Containers 4.0 - Full Lifecycle GPU Management for AI/ML Workloads
Discover how Kata Containers 4.0 revolutionizes GPU management for AI/ML workloads through CDI framework integration, enhanced security features, and streamlined resource allocation in Kubernetes environments.
KubeHound - Identifying Attack Paths in Kubernetes Clusters at Scale
Discover how to efficiently identify and analyze attack paths in Kubernetes clusters using KubeHound, focusing on scalable security assessment and threat detection techniques.
Building Secured Container Images with Wolfi - Zero CVE Container Development
Discover how to achieve zero CVE container security using Wolfi OS, a modern alternative to traditional distroless solutions, with practical insights from VPBank's successful implementation.
Towards Kata Containers 4 - When Kata Containers Meet Service Mesh
Explore security challenges and solutions for Kata Containers in service mesh environments, focusing on threat models, infrastructure sidecar designs, and performance benchmarks.
Zero Trust Architecture for Containers with Kata and Confidential Computing
Dive into advanced container security using Kata and Confidential Computing to implement zero-trust architecture, protect sensitive workloads, and achieve attestable pod integrity in Azure environments.
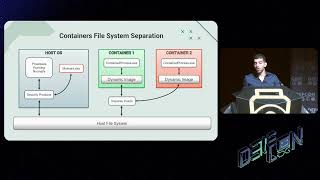
Staying Undetected Using the Windows Container Isolation Framework
Delve into Windows Container isolation mechanisms, file system separation techniques, and security implications, including methods to manipulate container frameworks for enhanced system protection.

Securing Kubernetes Applications by Crafting Custom Seccomp Profiles
Learn to create custom seccomp profiles for Kubernetes workloads, enhancing container security. Explore manual and automated techniques, multi-architecture profiles, and in-cluster enhancements for application-specific security.
Towards the Hardened Cloud-Native Cornerstone: Container Runtime Protection
Explore advanced container runtime protection techniques, from kernel-aided to hardware-assisted solutions, addressing security risks and privacy concerns in cloud-native environments.