Developing and Managing eBPF Programs with Rust
Explore eBPF programming with Rust, covering network programs, eBPF maps, container security, and LSM support for enhanced system observability and performance.
Runtime Security in the Cloud Native World
Explore runtime security in cloud-native environments, focusing on detecting and mitigating security breaches in production. Learn about essential tools and strategies for maintaining robust security measures.
How to Achieve Comprehensive Protection for Cloud Native Applications and Workloads
Learn comprehensive protection strategies for cloud-native applications, covering web security, runtime risks, and predictive models. Explore practical solutions and benefits through demos and real-world examples.
Armoring Cloud Native Workloads with LSM Superpowers
Explore how KubeArmor leverages Linux Security Modules to enhance container security, abstracting complexities and providing context for modern cloud-native workloads.
Enterprise Cloud Native Artifact Registry - Advanced Features and Management
Explore advanced features of Harbor for OCI artifact management, including cloud environments, attachments, high concurrency, and high availability deployments.
Efficient Storage Handling for Sandboxed Runtimes in Kubernetes
Exploring efficient storage solutions for sandboxed runtimes like Kata Containers, focusing on direct storage assignment for improved IO performance and security in containerized environments.
WebAssembly with Docker and Kubernetes - Achieving Nanosecond Cold Start Speeds
Explore WebAssembly's potential with Docker and Kubernetes, featuring demos on nanosecond cold start speeds, small size, and enhanced security. Learn about runwasi, WASI spin functions, and Spiderlightning apps.
How to Secure the Journey to Big Data Microservices - Fraud Management at Arvato
Explore Arvato's secure migration to microservices for fraud detection, featuring Docker containers, data protection compliance, and machine learning integration in a Big Data environment.
Securing Microservices with a Service Mesh in the Real World
Explore real-world strategies for enhancing microservices security using service mesh technology, presented by VMware expert Michael Farinacci.
Build Serverless with Kubernetes, Kata Containers and Bare Metal Cloud - Alibaba's Approach
Explore Alibaba's serverless infrastructure using Kubernetes, Kata Containers, and bare metal instances. Learn about multi-tenancy, isolation, and performance optimizations in cloud environments.

IAM Credentials for Containers in Mesos Clusters Using mesos2iam
Learn to implement isolated IAM profiles for Mesos tasks using mesos2iam, enhancing security and resource access control in containerized environments without storing credentials.
Getting Familiar with Security Observability Using eBPF and Cilium Tetragon
Explore security observability using eBPF and Cilium Tetragon. Learn to extract data, monitor activities, and detect container escapes for enhanced incident prevention and response.
Detecting Cloud and Container Threats - Kubernetes Security
Prepare, detect, and respond to security threats in containers and Kubernetes while maintaining agility. Learn to create perimeters, assess container content, and catch anomalies in fast-paced cloud environments.
Confidential Containers: The Next Episode in Workload Isolation
Explore advanced container isolation using Kata-CC, leveraging Trusted Execution Environment features for enhanced security in multi-tenant environments through workload attestation and memory encryption.
Confidential Containers Made Easy
Learn to provision and run Confidential Containers (CoCo) for cloud-native confidential computing. Explore integration of open-source projects, hardware technologies, and CRI runtimes using a Kubernetes operator for simplified deployment.
Cloud Native Security Landscape - Myths, Dragons, and Real Talk
Explore cloud-native security across the software lifecycle, from open-source creation to runtime threat detection. Learn about key projects, developer-security team collaboration, and separating real risks from myths.
Cloud Native Security 101 - Building Blocks, Patterns and Best Practices
Explore cloud native security fundamentals, attack vectors, and best practices for implementing continuous security in cloud applications without compromising innovation.
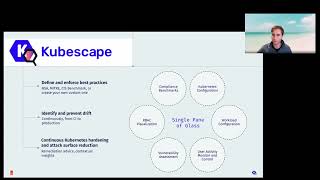
Securing the Cloud with Canonical Kubernetes and Kubescape
Learn to secure cloud environments using Canonical Kubernetes and Kubescape, exploring key strategies and tools for robust protection in modern containerized infrastructures.
Past, Present, and Future of Tetragon - First Production Use Cases and Future Trajectory
Explore Tetragon's journey from inception to v1.0, including production use cases, security challenges, and future goals. Learn how BPF-based security pitfalls were avoided and performance issues solved.
Cilium: From Service Mesh to Kubernetes and Beyond with eBPF
Explore Cilium's advancements in cloud native networking, observability, and security using eBPF. Learn about container networking optimization, service authentication, and expanding beyond Kubernetes.
Using Static Analysis to Catch Configuration Vulnerabilities
Learn to secure containers and IaC using static analysis. Discover how to identify misconfigurations, prevent vulnerabilities, and implement early detection in your development workflow for improved application security.