Navigating the Quantum Readiness Journey - Open-Source Cryptography, PKI and Signing Tools
Explore post-quantum cryptography standards and their implementation in open-source tools, focusing on IoT, container security, and software supply chain protection through quantum-resistant solutions.
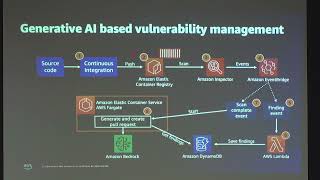
Applying Generative AI to Container CVE Remediation in CI Pipelines
Discover how to leverage generative AI for automating container vulnerability remediation in CI pipelines, with practical demonstrations and implementable solutions for efficient security management.
GitOps System Security - Protecting Against Privilege Escalation
Discover critical security insights for GitOps systems, including vulnerability analysis, misconfiguration prevention, and practical protection strategies against privilege escalation and cluster takeover threats.
Microsegment Your Network Like Mastercard with AdminNetworkPolicy
Discover how to implement cluster-wide network security using AdminNetworkPolicy in Kubernetes, featuring Mastercard's approach to enforcing granular controls and achieving PCI compliance through multi-tenant isolation.
Common Kubernetes Attack Vectors and How to Secure Your Cluster
Discover essential security strategies for Kubernetes deployments, covering authentication, network policies, pod security, and threat detection techniques for robust cluster protection.
Keyboards, Kiosks, and Kubernetes - Containerizing HID Workloads
Discover how to containerize GUI applications and kiosks in Kubernetes, enabling efficient device management, resource sharing, and enhanced security while maintaining host/workload decoupling.

Stop Kubernetes' Revolving Door: A Hands-on Tutorial to Secure a Kubernetes Cluster
Master essential Kubernetes security practices through hands-on exercises covering authentication, authorization, network policies, and pod security to effectively protect and fortify your clusters.
Reinventing Seccomp with eBPF and KRSI for Enhanced Kernel Security
Explore how eBPF and KRSI can enhance Linux kernel security beyond traditional Seccomp capabilities, with practical demonstrations for implementing advanced syscall filtering in containerized environments.
Demystifying the First Few Minutes After Compromising a Container
Explore essential post-container compromise techniques and immediate actions for security professionals, focusing on critical first-response strategies and containment methods.
Cloud Native's Next Decade: Stable, Secure, and Ready for Disruption - The Future of Cloud Security
Explore the future landscape of cloud native security, examining emerging challenges like AI system protection while understanding why current stability might precede a new wave of innovation.
Using Notary Project to Ensure Authenticity and Integrity of Artifacts Within the Enterprise
Discover how to implement Notary Project for securing software artifacts in enterprise environments, covering selection criteria, implementation steps, and latest features for ensuring authenticity and integrity.
Securing the Future of Ingress-NGINX
Discover essential security improvements and future roadmap for Ingress-NGINX, including hardening guidelines, default security features, and transition plans to Gateway API implementation.
Practical Supply Chain Security: Implementing SLSA Compliance from Build to Runtime
Discover practical strategies for implementing SLSA compliance, from using GitHub Actions and Cosign for artifact signing to enforcing runtime policies with Kyverno and securing keys with HSMs.